Loading article...

ZachXBT said on Oct 5 he fronted 349,700 USDC to infiltrate a Chinese-language laundering syndicate tied to the Bybit hack, tracing a $12 million cluster.
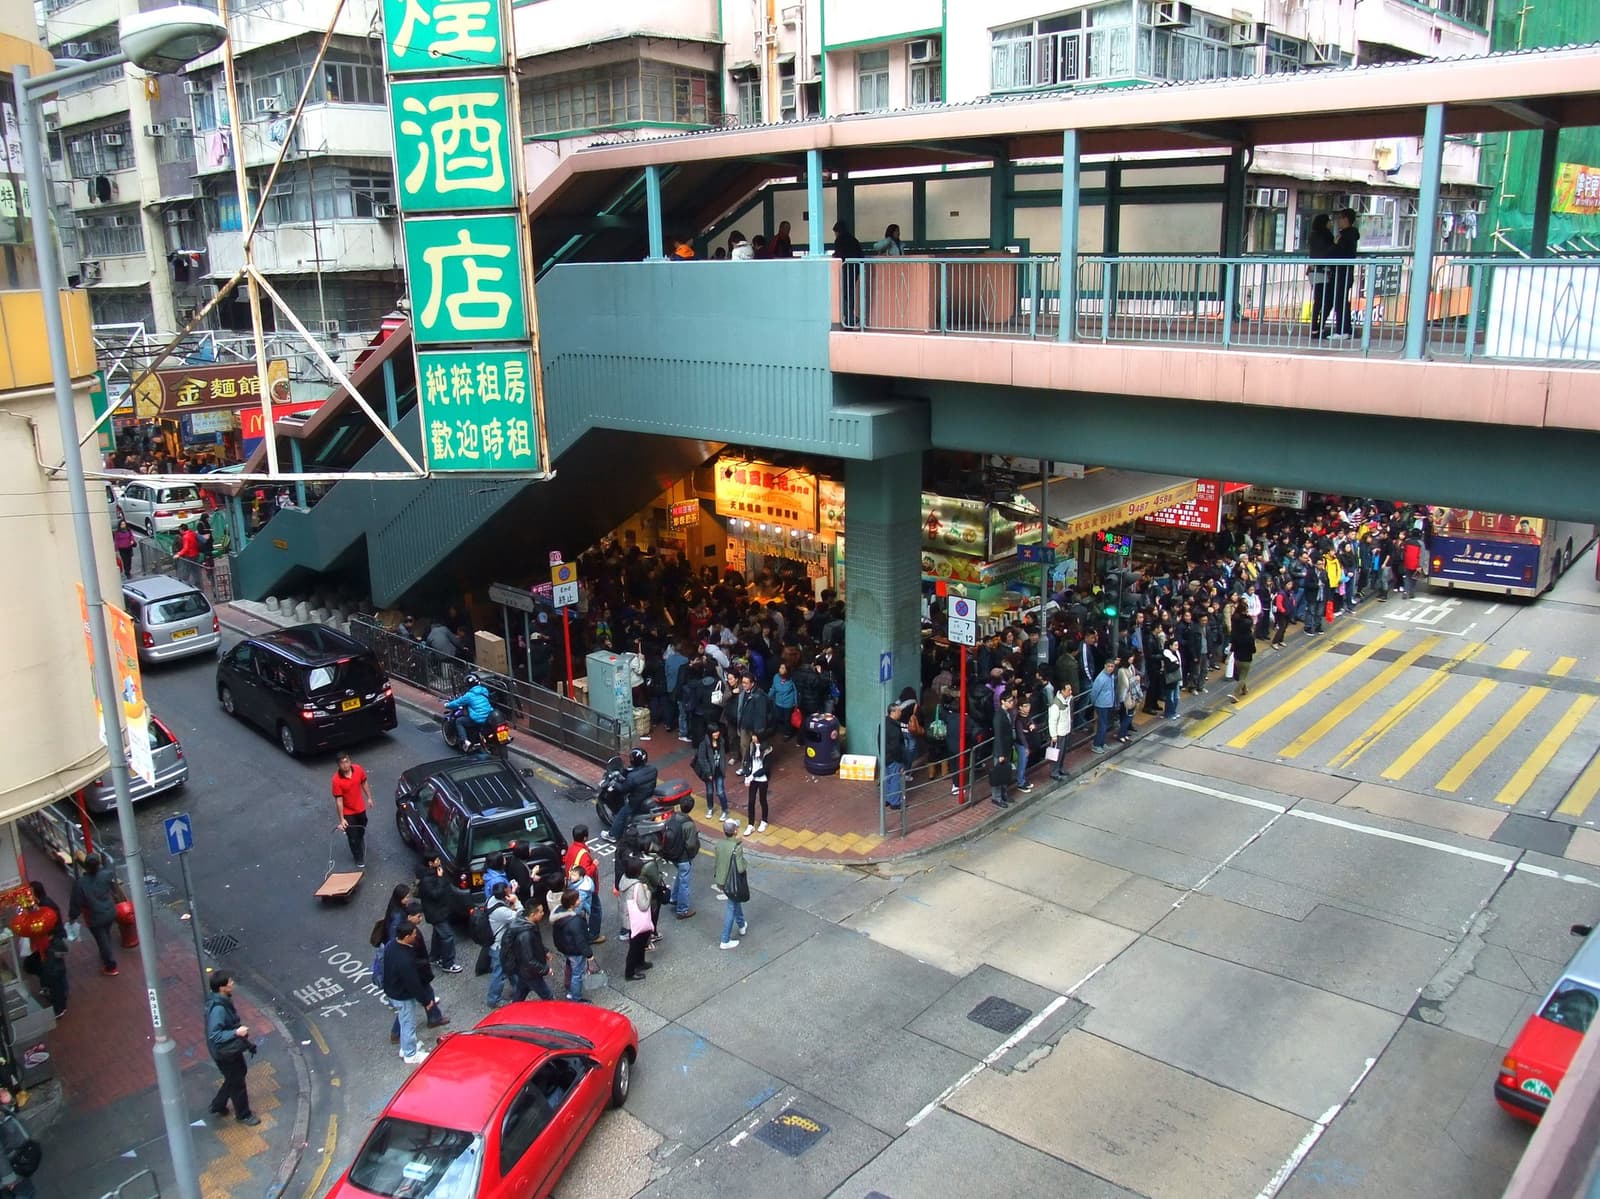
Mong Kok Road and Tung Choi Street in Hong Kong, where part of the laundering operation ran, according to the investigator. Photo: Mk2010 via Wikimedia Commons (CC BY-SA 3.0). Source
Blockchain investigator ZachXBT said he wired $349,700 of his own money to a Chinese-language laundering syndicate while posing as a customer. He laid out the operation in an Oct 5 thread on X, writing that he gathered intelligence that helped freeze funds from the February 2025 Bybit exploit. Decrypt reported the disclosure on Oct 5, quoting his line that he posed as a client to track the loot in real time.
"Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain," he wrote in the opening post. The exploit drained about $1.5 billion from Bybit on Feb 21, an attack the FBI attributed days later to North Korean hackers it tracks as TraderTraitor. ZachXBT alleges the launderers he met worked for that same network across Hong Kong and mainland China, a claim that rests on his own chats and chain traces rather than any official filing.
The hunt began in chat rooms. Shortly after the Bybit theft, ZachXBT said he watched more than 15 accounts ask for help with orders tied to stolen funds in Telegram and Discord groups. He started messaging them, and one contact using the name Jimmy Green on Telegram turned into his way in.
On March 6, 2025, he funded a fresh Ethereum address with 349,700 USDC to prepare several trades with Jimmy Green. The arrangement sent his USDC on Ethereum in exchange for the contact's USDT on Tron. The address Jimmy gave him had received gas from a wallet traceable to Bybit exploit funds and listed on the public Bybit exploit blacklist site, according to the account Decrypt published. After a few more swaps to build trust, Jimmy began talking about moving Bybit money for North Korea in advance, plus basic details of the setup in Hong Kong and on the mainland.
Jimmy said funds would move to Solana, and the movement happened within 24 hours. Staying inside cost a steady cut. "At this point, I realized I needed to continue losing 5% per order and gamble on capturing as much actionable intel as quickly as possible," ZachXBT wrote. He added that he fronted the full $349,700 with no promise Jimmy would not vanish with it, on top of the personal risk of dealing with the group.
Jimmy wanted more volume. On March 10 he kept pushing the fake persona until ZachXBT, in character, said the delays made him lose trust in the business. The reply was that the team had $1 million prepared and stood ready to start at any time. In another chat Jimmy sketched the division of labor, saying the crew takes the "u," shorthand for USDT, and spreads it among different receivers.
The chats turned into chain evidence on March 12, 2025. Jimmy sent a screenshot of himself bridging funds, and ZachXBT matched its amounts and timing to an order created minutes after the message on the THORChain explorer, the public log of swaps across blockchains. Jimmy then shared three Solana addresses that opened a cluster of more than $12 million in Bybit funds swapping in real time, hopping from Bitcoin to Ether to Solana and finally to Tron. Tether later froze 442,000 USDT tied to the cluster, according to the write-up of the thread.
Jimmy also dropped history the investigator could test. He said a team he knew had about $300,000 frozen in 2024, and ZachXBT found the freeze on-chain at 332,000 USDC tied to the Poloniex exploit, the November 2023 theft of more than $100 million that researchers link to Lazarus. Then came a Cambodia connection. Jimmy said he had washed $3 million in fraud proceeds for another client, and the trail led to a hot wallet used by Huione Guarantee, the Telegram marketplace for laundering services and stolen data.
Huione sits inside a larger enforcement file. The U.S. Treasury's FinCEN targeted the Huione Group over alleged laundering of at least $4 billion, Telegram banned the marketplace in May 2025, and Chinese authorities arrested former chairman Li Xiong after Cambodia deported him, according to the same account of the thread.
Between crime talk the two men chatted about ordinary life. "Throughout our conversations, Jimmy and I had a lot of small talk in between discussing laundering for DPRK," ZachXBT wrote. Mahjong, hunting wild rabbits, food, family life and Disney vacations all came up. Cointelegraph picked out those details in its Oct 6 report, which put the alleged syndicate total above $1 billion laundered across multiple exploits for Lazarus.
That top-line number needs care. The $1 billion-plus figure is ZachXBT's allegation about the network's past work, distinct from the $12 million cluster he says he traced and the $442,000 that Tether froze. Cointelegraph framed it the same way, treating the syndicate total as the investigator's finding while the FBI's attribution covers the theft itself. Chainalysis data cited in that report says hackers tied to North Korea stole at least $6.75 billion in digital assets through 2025.
The investigator says this was not a one-off. Since 2022 he has helped action more than $75 million in freezes tied to North Korean incidents, funding the riskier cases through foundation grants and individual donations. He sent the Bybit findings at once to trusted private-sector investigators and the law enforcement team on the case, and held off publishing because the investigation stayed sensitive.