Loading article...

The SEC's proposed transfer-agent rules would permit technology-neutral electronic master securityholder files while imposing record-control, access, processing and risk-management requirements on the registered agent.
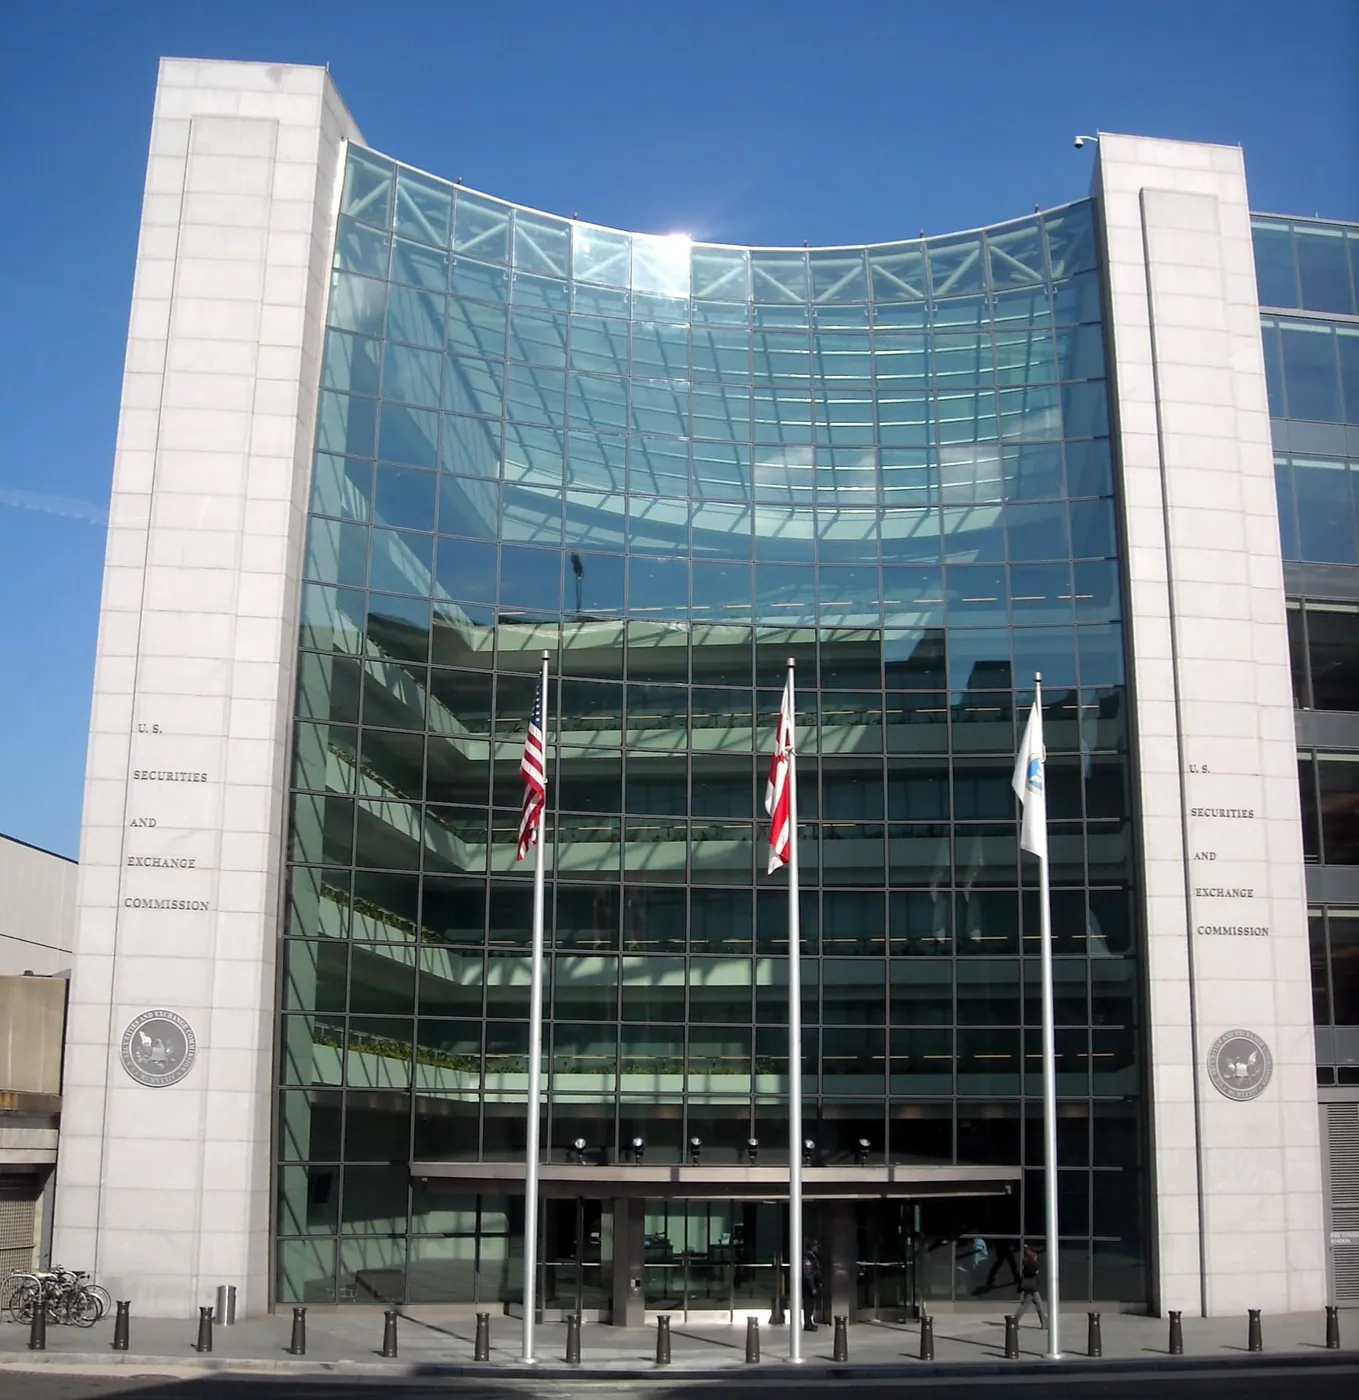
The U.S. Securities and Exchange Commission headquarters at 100 F Street NE, Washington, D.C. Photo: AgnosticPreachersKid via Wikimedia Commons (CC BY-SA 3.0). Source
The Securities and Exchange Commission has proposed revised rules for registered transfer agents that would require the official list of an issuer's individual securityholder accounts to be kept electronically and allow that file to consist of multiple linked files or systems. The proposal does not prescribe a blockchain, but it is written to cover distributed-ledger recordkeeping and asks transfer agents to disclose when they use that technology for a master securityholder file. The SEC published the proposal in the Federal Register on Sept. 4; comments are due by Nov. 3 under Release No. 34-106246.
For tokenized securities, the relevant change is not that a token would automatically become the legal record of ownership. The proposed definition would give a registered transfer agent discretion over the technology, systems and files that make up its master securityholder file, provided the agent keeps exclusive control over that file. A blockchain ledger could be part of such a recordkeeping arrangement, but the proposal does not remove the transfer agent's responsibility for the official record, its accessibility, or its accuracy.
That distinction is central to the operational problem described by CoinDesk. The publication reported that tokenized securities often operate with an onchain ledger and a separate legally recognized shareholder register. Joris Delanoue, chief executive of SEC-registered transfer agent Fairmint, told CoinDesk that the proposal recognizes a blockchain as a possible database for the master file rather than only a copy of it. Eli Cohen, chief legal officer at Centrifuge, told the publication that an authoritative blockchain record could replace a two-ledger process.
The SEC's text supports the possibility of a single electronic recordkeeping arrangement, but it attaches conditions that are absent from a description of token ownership alone. The filing's proposed master-file definition, its requirements for position data, its one-business-day posting standard and its proposed controls for electronic records all remain directed at the registered transfer agent. The rulemaking is a proposal, not an approval of a particular token, ledger, network or transfer-agent business model.
Transfer agents act for issuers at points where a security is issued, transferred, cancelled or otherwise recorded. The SEC describes the master securityholder file as the official list of registered owners: it records the accounts through which the issuer and its transfer agent identify who holds registered securities and in what amount. That differs from the much larger market for securities held in street name. In that arrangement, an investor is generally a beneficial owner through a broker or bank, while the depository's nominee is the registered owner on the issuer's books, according to the proposing release.
The release says a transfer agent's statutory functions include countersigning securities at issuance, monitoring issuance to prevent unauthorized issuance, registering transfers, exchanging or converting securities, and transferring record ownership through bookkeeping entries. It treats the official ownership file as part of the national clearance and settlement system, rather than as a customer-facing balance display. The proposal applies to registered transfer agents and the qualifying securities for which they perform those functions; it is not a general rule for every digital asset that calls itself a tokenized security.
Under the proposed definition, the master securityholder file would be maintained in electronic form and could comprise multiple linked files or systems. The language is deliberately broader than a central database or a particular distributed ledger. It would allow a recordkeeping design to combine systems, but the registered transfer agent would have to maintain exclusive control over the master file at all times. The proposal also retains the principle that there can be only one recordkeeping transfer agent for a given securities issue, meaning one registered agent must maintain and update that official file.
The SEC's description of a transfer makes the consequence concrete. For an uncertificated security, a book-entry transfer is completed when the transfer agent registers the change in ownership on the master securityholder file. The proposal says that prompt posting is therefore the transfer turnaround for uncertificated securities. A token transfer recorded on a ledger does not, by itself, answer whether the recordkeeping transfer agent has completed its regulated registration function. The answer depends on the recordkeeping arrangement and whether the relevant ledger entry is part of the master file under the agent's control.
The release also preserves the control book, a separate record of the issuer's authorized, issued and outstanding shares or debt principal. The aggregate amounts in the master file must be capable of being compared with the control book to detect record differences and prevent overissuance. The proposal would define an overissuance as an out-of-balance condition in which issued and outstanding securities exceed the authorized and outstanding amount reflected in that control book. For an overissuance caused by an agent that knows of it, the proposed rule would retain the requirement to buy in equivalent securities within 60 days, subject to specified exceptions.
Those mechanics help explain why a tokenized register has to be more than a transfer log. The recordkeeper has to identify the issue, accounts, holdings and changes in ownership, while also maintaining the issuer-level total that tests whether the recorded positions exceed what the issuer authorized. A ledger may provide one part of that system. The SEC's proposed definition permits linked systems, but it does not say that a public ledger's balance history alone satisfies every recordkeeping obligation.
The proposal would replace the older term "certificate detail" with "position detail" so the rules expressly cover uncertificated as well as certificated securities. For each position, the proposed minimum information includes a unique security identifier, the number of shares or principal amount, the securityholder's full name and identifying information, contact information sufficient for communications and payments, a physical mailing address, issue and cancellation dates, and other information the agent reasonably needs for its operations or to research record differences.
The presence of those requirements does not mean every item must be publicly visible on a blockchain. The proposed master file may use linked systems, and the SEC does not prescribe where each data element must sit. It does mean that an arrangement seeking to make an onchain ledger part of the official file has to account for ordinary shareholder administration, including payments, legal notices and communications. CoinDesk reported that Delanoue cited deaths, inheritance, ownership restrictions and mailed documents as examples of functions a digital transfer agent would still need to handle.
The proposed rules would also tighten the time for recording transactions. A recordkeeping transfer agent would have to post the required debits and credits to the master securityholder file within the shorter of one business day or the time specified by Exchange Act Rule 15c6-1(a). The SEC says that, under the current settlement-cycle standard, this would generally require posting within one business day of a security's transfer, purchase, issuance or redemption. Co-transfer agents would have one business day to provide the recordkeeping agent with transfer data and one business day to answer its related inquiries.
The SEC ties that schedule to the same processing requirement for certificated and uncertificated securities. Its explanation is that electronic communication and automated processing allow faster handling than the paper and mail processes on which the existing rules were built. A tokenized system could make an ownership event observable quickly, but the proposal's benchmark remains the agent's accurate posting to the official file. The rule would measure the agent's performance, rather than treating a network's block time or transaction confirmation as a substitute for that standard.
The proposal also establishes conditions for electronic recordkeeping systems generally. A transfer agent using one would need reasonable controls for the integrity, accessibility, reproducibility, redundancy and continuity of its records. The enumerated controls include safeguards against unauthorized alteration or loss; retrieval that permits immediate production in human-readable and reasonably usable electronic formats; an audit trail showing access, modification and deletion, including the user and time of the event; and a way to recover altered, damaged or lost records.
Those provisions are technology-neutral rather than blockchain-specific. The SEC says an electronic recordkeeping system can be any system designed to maintain, retain or preserve digital records. It asks commenters whether that definition is sufficiently broad for cloud platforms, distributed-ledger systems and AI-driven tools. The proposal further says a transfer agent using a blockchain or other distributed ledger has independent access to records when it can regularly view them without a third party's intervention, permit regulatory examination and promptly furnish copies.
That is a functional test. The release does not say that recording data on a blockchain establishes independent access in every deployment. It describes the access, examination and production abilities a transfer agent must have. Where another company maintains records and the transfer agent does not have independent access, the proposal would require the agent to obtain and file a legally binding agreement under which that third party permits regulatory examination and promptly provides complete current copies. In either case, outsourcing record storage would not relieve the transfer agent of its responsibility to maintain the records.
The SEC's modernization proposal is wider than record-file terminology. Its accompanying fact sheet says the agency would replace several old processing and recordkeeping requirements, rescind an exemption rule, change Forms TA-1 and TA-2, and add rules on compliance and restrictive legends. On the annual Form TA-2, transfer agents would report the number of issues for which they maintained the master securityholder file using distributed-ledger technology during the reporting period. They would also report data about tokenization models under the proposed revisions.
The proposed risk-management rule would require written policies and procedures reasonably designed to protect securities and funds in the transfer agent's possession, custody or control from specified risks, and to identify, measure, monitor and mitigate material risks from its business and operations. The fact sheet says the proposal would also require a separate bank account for issuer, securityholder and third-party funds, along with a written business-continuity plan. These requirements apply to the transfer agent's regulated function; they would not be displaced by using a smart contract for part of an issuance or transfer process.
Proposed Rule 17ad-30 would require transfer agents to adopt written compliance policies and procedures for applicable federal securities laws and transfer-agent rules. Proposed Rule 17ad-31 would address restrictive legends, including requirements for placing and removing them. The SEC says the rule would restrict a transfer agent's involvement in an unregistered securities transaction unless it has a reasonable basis to believe the transaction does not violate, or form part of a chain of transactions that violates, Section 5(a) of the Securities Act.
That makes the proposal a poor fit for the claim that tokenized securities would become permissionless. The SEC's release says its rules need to account for tokenized securities, distributed-ledger technologies and smart contracts, while the fact sheet specifies compliance, recordkeeping and risk-management obligations for registered transfer agents. CoinDesk similarly reported that a public blockchain could hold an ownership record while identity checks and transfer restrictions remain part of the asset and the agent's process.
The proposal also addresses operational continuity. A transfer agent that stops serving an issue would have 15 calendar days to deliver, provide or make available specified records to the issuer or its designee, such as a successor transfer agent. The SEC said issuer complaints have included disputes in which outgoing agents delayed securityholder records. The proposed delivery requirement covers master securityholder files, transfer journals, control books, cancelled-certificate records and other listed materials. A blockchain record that can be viewed by participants would not eliminate that delivery obligation or the agent's duty to make usable copies available.
Chairman Paul S. Atkins said in the SEC's Sept. 1 announcement that the proposal would update the agency's rules for current transfer-agent processes, including electronic communications and blockchain technology in securities offerings and share transfers. The SEC says most of the current transfer-agent rules date from the late 1970s and early 1980s. Its release identifies 327 registered transfer agents as of June 30, 2026, while noting that some registered agents may not be active and that annual reports can be late or missing.
The Commission's own economic analysis says it cannot quantify many of the proposal's expected effects or the cost for agents to meet the proposed one-day processing standard and new risk-management requirements. It requests data and comment on those issues, including whether electronic-recordkeeping controls are workable for emerging systems and whether the proposed definitions accommodate distributed-ledger technology.
No final rule, effective date or implementation timetable has been announced. Interested parties can submit comments under File No. S7-2026-30 through Nov. 3. Until the SEC completes that process, the immediate development is a proposed regulatory framework: electronic master securityholder files may use linked systems and distributed-ledger technology, but the registered transfer agent would remain responsible for controlling the authoritative record and performing the associated securities-law functions.