Becoming a Smart Contract Auditor
An empirical thesis and career guide on becoming a smart contract auditor, covering formal verification, invariant fuzzing, static analysis, adversarial attack vectors, and competitive bug bounty dynamics.
Smart contract auditing represents the most adversarial and high-stakes discipline in decentralized software engineering. In conventional cybersecurity, security assessments evaluate web application boundaries, firewalls, and identity providers to protect private enterprise databases. In Web3 networks governed by the Ethereum Foundation and the Solana Foundation, smart contracts execute on permissionless distributed networks where contract bytecode is public, transaction execution is irreversible, and contracts frequently manage hundreds of millions of dollars in liquid collateral.
A single arithmetic rounding bug, uninitialized proxy variable, or oracle latency discrepancy allows autonomous arbitrage bots and black-hat exploiters to drain protocol reserves within seconds. According to annual web3 security telemetry published by Immunefi and CertiK, more than 1.8 billion dollars in digital assets were stolen across decentralized protocols in 2024 and 2025 alone. As a direct consequence, smart contract auditing has evolved from superficial manual code reviews into a multi-layered verification science combining static analysis, invariant property fuzzing, and formal mathematical proofs.
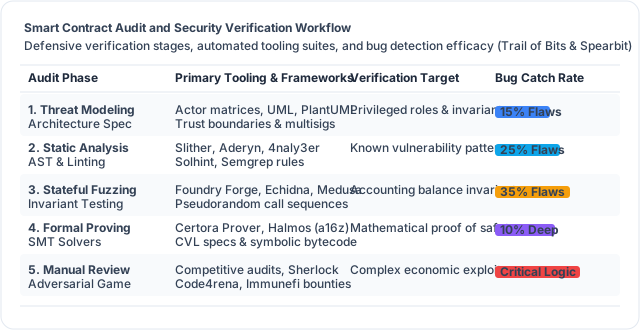
Figure 1: Comprehensive five-stage verification pipeline employed by institutional audit firms and competitive security researchers to identify vulnerabilities prior to mainnet deployment.
The Role of a Smart Contract Auditor
A smart contract auditor does not write user-facing application features. Their singular objective is to break software before malicious actors do. The auditor dissects protocol specifications, models adversarial threat vectors, verifies state transition invariants, and produces comprehensive audit reports that document potential vulnerabilities, exploit proofs of concept (PoCs), and remediation steps.
Auditors work across three primary organizational structures:
-
Institutional Security Firms: Organizations like Trail of Bits, OpenZeppelin, Consensys Diligence, CertiK, and Spearbit provide structured multi-week team audits for protocols preparing for token generation events or major protocol upgrades.
-
Competitive Audit Platforms: Crowd-sourced contest platforms such as Code4rena and Sherlock host time-bound, competitive security reviews. Hundreds of independent researchers (wardens or lead senior watchees) review identical codebases, competing for prize pools proportional to the severity and uniqueness of bugs discovered.
-
Bug Bounty Hunting: Independent security researchers hunt for zero-day vulnerabilities in deployed mainnet protocols via platforms like Immunefi. Leading protocols offer bounties scaling up to five or ten million dollars for critical vulnerabilities that could lead to direct theft of user funds.
While an audit report provides strong assurance, the security community acknowledges that an audit is not a guarantee of absolute safety. It is an empirical time-boxed assessment by experienced security practitioners evaluating code against known and novel attack vectors.
The Five-Stage Security Verification Pipeline
Leading security practitioners execute a structured verification pipeline that combines automated tooling with deep manual code comprehension:
1. Specification Analysis and Threat Modeling
Before opening code editors, auditors study whitepapers, documentation, and mathematical models to establish the protocol's expected behavior. They map out the actor matrix, separating untrusted external users, liquidity providers, protocol governors, and authorized keepers.
Auditors identify the core system invariants: conditions that must remain true under every possible execution state. For example, in a decentralized lending market like Compound Finance or Morpho Protocol, total collateral value multiplied by liquidation thresholds must always exceed total outstanding debt across solvent accounts.
2. Static Analysis and Automated AST Linting
Auditors run automated static analysis tools to catch low-hanging vulnerabilities and anti-patterns. Slither, an open-source static analysis framework developed by Trail of Bits, parses contract abstract syntax trees (ASTs) to flag reentrancy vulnerabilities, uninitialized variables, shadow variables, and gas inefficiencies within seconds.
Tools like Aderyn by Cyfrin and Solhint automate rule-based scanning, allowing auditors to focus manual cognitive effort on complex business logic and cross-contract interactions.
3. Stateful Property-Based Fuzzing and Invariant Testing
Unit tests only verify code against scenarios the developer anticipated. Fuzz testing, in contrast, bombards contracts with thousands of pseudorandom transactions to break system invariants.
Auditors utilize Foundry Forge to write invariant tests in Solidity, alongside dedicated fuzzing engines like Echidna and Medusa. Stateful fuzzers maintain execution state across sequential contract calls, discovering obscure edge cases such as multi-step flash loan liquidations or rounding accumulations.
// SPDX-License-Identifier: MIT
pragma solidity 0.8.28;

import {Test} from "forge-std/Test.sol";
import {LendingVault} from "../src/LendingVault.sol";

contract InvariantVaultTest is Test {
    LendingVault public vault;

    function setUp() public {
        vault = new LendingVault();
    }

// @notice Invariant: Total vault assets must always equal or exceed user deposit accounting
    function invariant_SolvencyAccounting() public view {
        assertGe(
            address(vault).balance,
            vault.totalUserDeposits(),
            "Solvency invariant breached: undercollateralized state detected"
        );
    }
}
4. Formal Verification and Symbolic Execution
For high-value financial primitives, mathematical proof provides the ultimate verification standard. Formal verification tools convert smart contract bytecode into mathematical constraints evaluated by Satisfiability Modulo Theories (SMT) solvers.
Frameworks such as Halmos from a16z and Certora Prover mathematically prove whether any input combination exists that could violate a formally defined specification written in Certora Verification Language (CVL).
5. Manual Code Review and Economic Exploit Modeling
Automated tools catch syntax patterns, but human ingenuity identifies economic design flaws. In manual review, auditors evaluate oracle integration latencies, flash loan manipulability, governance voting attack thresholds, and cross-chain messaging assumptions.
Core Vulnerability Taxonomy in Decentralized Systems
Auditors must master the recurring vulnerability classes documented in the OWASP Smart Contract Top 10 and historical post-mortems compiled on Etherscan:
Reentrancy: Standard, Cross-Function, and Read-Only
Reentrancy occurs when an external contract call transfers execution control before the caller updates internal state balances. While standard reentrancy is well understood, advanced variants continue to compromise protocols:
-
Cross-Contract Reentrancy: An attacker exploits a state discrepancy between two separate contracts that rely on each other for shared accounting data.
-
Read-Only Reentrancy: A contract updates balances during an external call, allowing an attacker to call a separate third-party protocol that reads the un-updated, temporary price state from the first contract within the same transaction.
Mitigations require strict application of the checks-effects-interactions pattern, mutex locks, and the modern adoption of EIP-1153 transient storage opcodes (TSTORE and TLOAD).
Price Oracle Manipulation and Flash Loans
Querying spot token prices directly from decentralized exchange liquidity pools like Uniswap Labs or Curve Finance invites catastrophic attacks. An attacker borrows tens of millions in uncollateralized capital via a flash loan, swaps heavily in an AMM pool to artificially inflate or deflate the asset price, and exploits a lending protocol that uses that AMM as an oracle.
Auditors verify that protocols integrate decentralized oracle networks like Chainlink Documentation or Pyth Network, or compute geometric time-weighted average prices (TWAP) with wide observation windows.
+-------------------------------------------------------------------------+
|                  Flash Loan Oracle Attack Vector Flow                   |
+-------------------------------------------------------------------------+
|  1. Attacker borrows $50M USDC via uncollateralized flash loan          |
|                                |                                        |
|                                v                                        |
|  2. Swaps $50M into DEX pool to artificially distort spot oracle price  |
|                                |                                        |
|                                v                                        |
|  3. Vulnerable protocol reads distorted spot price as true value        |
|                                |                                        |
|                                v                                        |
|  4. Attacker deposits manipulated asset, borrows entire protocol pool   |
|                                |                                        |
|                                v                                        |
|  5. Repays flash loan, exits transaction with millions in stolen profit |
+-------------------------------------------------------------------------+
Upgradeable Proxy Storage Collisions
Modern protocols implement upgradeability patterns like Universal Upgradeable Proxy Standard (UUPS) or Transparent Upgradeable Proxies from OpenZeppelin. In upgradeable contracts, state storage lives in the proxy contract while execution logic lives in implementation contracts called via delegatecall.
If a developer modifies state variable declarations between versions, storage layout collisions corrupt memory pointers, overwriting owner addresses or balance mappings. Auditors audit storage layouts using storage inspection commands (forge inspect <contract> storage) and enforce namespaced storage standards like ERC-7201.
Access Control and Signature Verification
Auditors scrutinize authorization gates, ensuring that initialization functions cannot be front-run by unauthenticated callers. When verifying off-chain signatures via ECDSA, auditors confirm that contracts guard against signature malleability and implement domain separators under EIP-712 to prevent cross-chain or cross-contract replay attacks.
Formal Verification in Depth: Certora Verification Language and SMT Solvers
While fuzzing executes smart contract bytecode using pseudorandom inputs, formal verification employs mathematical logic to prove or disprove system properties across all possible execution inputs.
In formal verification, security researchers write mathematical specifications that describe system invariants. The leading framework in production is the Certora Prover, documented extensively in the Certora Documentation. Auditors author specifications in Certora Verification Language (CVL), a specialized declarative language that interfaces with Solidity bytecode:
// CVL Specification: Solvency Invariant for Lending Pool
methods {
    function totalDeposits() external returns (uint256) envfree;
    function totalBorrows() external returns (uint256) envfree;
    function getReserveBalance() external returns (uint256) envfree;
}

rule systemSolvencyNeverBreached(method f) {
    env e;
    calldataarg args;

/ Pre-condition: System is solvent prior to call
    require getReserveBalance() >= totalBorrows();

/ Execute arbitrary state-transition function
    f(e, args);

/ Post-condition: Reserve balance must always cover liabilities
    assert getReserveBalance() >= totalBorrows(),
        "Solvency violation: reserves dropped below system borrows";
}
Under the hood, formal verification tools compile this specification alongside contract bytecode into Satisfiability Modulo Theories (SMT) formulas. These formulas are ingested by state-of-the-art automated theorem provers such as the Z3 SMT Solver and CVC5. The solver attempts to find a mathematical counterexample. If the solver reports UNSAT (unsatisfiable), it has mathematically proven that no combination of inputs or storage states can ever violate the property. If it reports SAT (satisfiable), it outputs a concrete transaction trace illustrating the exact exploit path.
Complementing Certora, researchers utilize Halmos, a symbolic execution tool developed by Paradigm. Halmos executes tests written natively in Solidity, treating inputs as mathematical symbols rather than concrete values. This enables developers building on networks like Arbitrum, Optimism, and Base to formally verify core invariants on Polygon Labs zkEVM without leaving their native Foundry workflow. Transaction simulation environments like Tenderly empower auditors to reproduce execution state diffs locally.
Autopsies of Major DeFi Exploits: Lessons for Security Researchers
Studying past economic exploits provides auditors with an indispensable mental library of systemic failure modes. Historical exploits demonstrate that vulnerabilities rarely stem from simple syntax typos; they arise from subtle discrepancies in economic assumptions:
The Euler Finance Flash Loan Donation Exploit ($197 Million)
In March 2023, lending protocol Euler Finance suffered a devastating 197-million-dollar drainage. The vulnerability existed in the interaction between liquidations and the newly added donateToReserves function.
Euler allowed users to enter a leveraged position by minting debt tokens (dTokens) and deposit tokens (eTokens). When liquidating an underwater account, liquidators received a discount on collateral. The flaw occurred because the donateToReserves function did not execute a solvency check (checkLiquidity) after a user donated their eTokens.
An attacker borrowed millions in DAI via a flash loan from Aave Governance, deposited collateral, minted excessive dTokens, and then donated their eTokens to the reserve. This artificially threw their own account into severe insolvency. However, because the donation created a mathematical imbalance where collateral value appeared zero while debt remained massive, the protocol's liquidation calculation awarded the liquidator (controlled by the attacker) an enormous liquidation bonus, draining the entire lending pool.
The lesson for auditors: every state transition that modifies balance ratios must trigger complete health factor checks, even if the action ostensibly appears as a benign voluntary donation.
The Curve Finance Vyper Compiler Reentrancy Exploit ($73 Million)
In July 2023, several liquidity pools on Curve Finance were drained due to a compiler-level bug in Vyper versions 0.2.15, 0.2.16, and 0.3.0.
Curve utilized non-reentrant locks (@nonreentrant('lock')) to protect liquidity removal and swap functions. However, due to a bug in the Vyper compiler, the reentrancy lock storage slot was allocated dynamically across separate functions rather than referencing a single global storage slot. Consequently, when an external call occurred during liquidity removal, an attacker was able to re-enter a separate pool function because the lock variable resided in an unshared storage location.
This exploit reinforced a vital reality for auditors: security reviews must extend beyond high-level application source code to evaluate compiler mechanics, intermediate representation (IR) pipelines, and low-level storage layouts documented in the Solidity Documentation.
The Nomad Bridge Zero-Hash Initialization Flaw ($190 Million)
Cross-chain bridges represent critical security choke points. In August 2022, the Nomad bridge was drained of 190 million dollars due to a flawed contract upgrade.
During a routine initialization of the Replica contract, the team set the trusted root of processed messages to 0x00. In the message confirmation logic, an uninitialized or unproven message defaulted to returning 0x00. Because 0x00 was registered as an authorized root in the contract storage mapping, the verification check evaluated to true for completely unproven transactions.
Once a searcher discovered that any arbitrary withdrawal transaction could be submitted, copycat exploiters across the globe copied the transaction calldata, modified the recipient address, and submitted fraudulent withdrawals until all bridge reserves were exhausted. Auditors must rigorously scrutinize initialization parameters and ensure that null values (address(0) or bytes32(0)) can never satisfy authentication checks.
Telemetry tracked across DefiLlama and Dune Analytics confirms that multi-layer audits examining both protocol code and cross-contract integrations significantly reduce the incidence of multi-million-dollar catastrophes.
Practical Wargames and Competitive Auditing Contests
Theoretical knowledge cannot substitute for hands-on vulnerability exploitation. Aspiring auditors validate their skills by solving curated smart contract security wargames:
-
Ethernaut by OpenZeppelin: A browser-based EVM wargame that introduces foundational security concepts, including fallback functions, storage slot layouts, delegatecall injections, and reentrancy.
-
Damn Vulnerable DeFi: The gold standard wargame created by Tincho for learning offensive DeFi security. Challenges simulate real-world DeFi protocols, requiring students to execute flash loan attacks, manipulate price oracles, compromise governance timelocks, and drain ERC-4626 vault shares using Foundry test scripts.
Following wargame completion, candidates enter live competitive audit contests on Code4rena and Sherlock. In these contests, researchers review unpublished production codebases, write reproducible exploit proofs of concept, and earn financial compensation based on bug severity. Top contest participants build public leaderboard reputations that serve as definitive proof of competence for institutional security firms. Macro hiring trends monitored in the Electric Capital Developer Report indicate sustained demand for verified security researchers.
Educational developer platforms like Cyfrin Updraft provide structured courses covering advanced fuzzing, static analysis, and security reporting standards.
Audit Report Writing and Remediation Standards
Discovering a critical vulnerability is only half of an auditor's responsibility. The vulnerability must be communicated clearly so that protocol engineers can implement safe remediations without introducing secondary bugs.
A professional audit finding follows a standardized structure:
-
Title and Severity Classification: Categorized as Critical, High, Medium, Low, or Informational based on the Common Vulnerability Scoring System (CVSS) or competitive platform rules.
-
Vulnerability Description: A concise, technical explanation of the flaw, referencing specific lines in source contracts.
-
Impact Assessment: Explaining the precise economic or architectural consequences, such as complete loss of user deposits or permanent freezing of contract operations.
-
Proof of Concept (PoC): A fully executable, isolated test case written in Foundry Forge that sets up contract state, simulates the attack transaction, and asserts the successful drainage of funds.
-
Recommended Remediation: Providing exact code diffs demonstrating how to fix the flaw using audited patterns.
- // Vulnerable state update after call
- (bool success, ) = msg.sender.call{value: amount}("");
- require(success, "Transfer failed");
- balances[msg.sender] -= amount;

+ // Remediated Checks-Effects-Interactions
+ balances[msg.sender] -= amount;
+ (bool success, ) = msg.sender.call{value: amount}("");
+ require(success, "Transfer failed");
Career Trajectories, Compensation Models, and Market Realities
Smart contract security researchers occupy the highest compensation tier in Web3 engineering due to the extreme capital risks associated with protocol failures. According to industry surveys from Pantera Capital and Web3.career:
Junior smart contract security researchers with strong contest leaderboards and verified wargame completions earn starting base salaries between $100,000 and $140,000 USD. Experienced auditors at recognized firms like Trail of Bits or Spearbit earn base salaries ranging from $150,000 to $240,000 USD, often augmented by project completion bonuses.
Elite independent security researchers who focus exclusively on competitive audit contests and bug bounties on Immunefi frequently earn between $250,000 and $600,000 annually. Legendary security researchers who responsibly disclose critical zero-day bugs in protocols securing billions in TVL have earned bounties ranging from one million to over two million dollars for single disclosures.
To launch a career as a smart contract auditor, candidates should follow a systematic roadmap:
-
Achieve deep proficiency in Solidity, the EVM execution model, and Foundry testing workflows.
-
Complete all levels of Ethernaut and Damn Vulnerable DeFi, publishing documented Foundry solutions on GitHub.
-
Participate regularly in competitive audit contests on Code4rena and Sherlock, studying winning submissions from top-ranked researchers after contest closures.
-
Read published audit reports from premier security firms like Trail of Bits, OpenZeppelin, and Spearbit to analyze how professional auditors dissect complex DeFi protocols.
By developing rigorous adversarial thinking, mastering automated fuzzing and formal verification tools, and demonstrating reproducible vulnerability detection, security researchers can build highly lucrative careers safeguarding the financial infrastructure of the decentralized future.