Loading article...

An in-depth technical examination of advanced blockchain oracle applications, exploring Proof of Reserve, Verifiable Randomness, parametric insurance, and cross-chain messaging.
When software engineers and crypto market participants discuss blockchain oracles, conversation almost invariably centers on cryptocurrency price feeds. In the popular imagination, an oracle exists primarily to tell an on-chain lending contract that Ethereum is trading at $$3,000$ or that Bitcoin is trading at $$60,000$. While price discovery across decentralized exchanges like Uniswap and lending protocols like Aave represents a multi-billion-dollar use case, viewing oracles strictly as asset tickers fundamentally misunderstands their architectural role.
At its core, a blockchain oracle is a general-purpose, verifiable computation and data attestation engine. Blockchains such as the Ethereum Foundation network, Solana Protocol, and Avalanche are deterministic state machines intentionally isolated from the physical world. Any computational logic that requires reading real-world entropy, verifying external physical state, generating unbiased randomness, attesting off-chain collateral reserves, or orchestrating sovereign state transitions across disparate blockchains requires a decentralized oracle.
As institutional capital deploys on-chain through Real-World Assets (RWAs), tokenized sovereign debt, automated insurance derivatives, and decentralized identity systems, oracles are transitioning from simple price broadcasters into the foundational trust rails of global commerce. This technical thesis explores the advanced, non-price applications of decentralized oracle networks, analyzing their cryptographic mechanics, mathematical security models, and production implementations across contemporary Web3 systems.
The collapse of centralized custodial institutions such as FTX, Celsius Network, and BlockFi demonstrated the severe risks of opacity in off-chain balance sheets. Centralized entities repeatedly misrepresented their fractional reserves, issuing unsecured paper claims against non-existent deposits.
In the digital asset ecosystem, two critical categories of assets depend entirely on external custodial backing:
Chainlink Proof of Reserve (PoR) provides automated, on-chain verification of collateral reserves.
Rather than relying on monthly PDF attestation reports from accounting firms that become outdated the moment they are signed, PoR networks query financial custodians and auditing APIs continuously, matching standards verified by CertiK and Halborn Security:
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.24;

interface IProofOfReserveFeed {
    function latestAnswer() external view returns (int256);
}

/// @notice Token contract integrating automated Proof of Reserve minting guardrails
contract SecuredRwaToken {
    IProofOfReserveFeed public immutable porFeed;
    uint256 public totalSupply;
    address public minter;

    error ReserveDeficit();
    error Unauthorized();

    constructor(address _porFeed) {
        porFeed = IProofOfReserveFeed(_porFeed);
        minter = msg.sender;
    }

// @notice Mints new tokens only if total supply remains backed by audited reserves
    function mint(address to, uint256 amount) external {
        if (msg.sender != minter) revert Unauthorized();

        int256 currentReserves = porFeed.latestAnswer();
        if (currentReserves <= 0) revert ReserveDeficit();

/ Enforce that new total supply cannot exceed verified collateral
        if (totalSupply + amount > uint256(currentReserves)) {
            revert ReserveDeficit();
        }

        totalSupply += amount;
/ Balance assignment logic executed here
    }
}
By embedding this mathematical check directly into the minting logic, protocols eliminate the possibility of an unauthorized infinite-mint exploit or fractional reserve insolvency.
Generating unbiased random numbers within a deterministic blockchain is mathematically impossible using native opcodes alone.
Historically, naive developers attempted to derive random seeds using on-chain parameters such as block.timestamp, blockhash, or block.prevrandao. These approaches introduce catastrophic vulnerabilities:
To solve this vulnerability, modern protocols implement a Verifiable Random Function (VRF), formulated by Silvio Micali, Michael Rabin, and Salil Vadhan in 1999 and deployed on-chain by Chainlink VRF.
A VRF is the public-key cryptographic equivalent of a keyed cryptographic hash function. Given a secret key $SK$ and a public seed $X$, the function evaluates:
$$(R, \pi) \leftarrow ext{VRF_Prove}(SK, X)$$
where $R$ is the pseudorandom output value and $\pi$ is a cryptographic proof demonstrating that $R$ was generated correctly. Crucially, any party possessing the corresponding public key $PK$ can evaluate:
$$ ext{VRF_Verify}(PK, X, R, \pi) \in { ext{True}, ext{False}}$$
Because the output $R$ is strictly determined by the seed $X$ and the secret key $SK$, the oracle node cannot alter the random outcome without producing an invalid cryptographic proof $\pi$. Furthermore, because the seed $X$ includes the block hash of the requesting transaction, the requesting smart contract cannot anticipate the random value prior to submitting its transaction.
The proliferation of sovereign Layer 1 blockchains (such as Ethereum, Solana, Avalanche, and Near Protocol) alongside modular Layer 2 rollups (such as Arbitrum, Optimism, and Polygon) has fragmented liquidity across isolated state machines.
Historically, cross-chain communication relied upon custodial multi-sig bridges that suffered over $$2 ext{ billion}$ in catastrophic security exploits (including the Ronin, Wormhole, and Nomad hacks).
To eliminate bridge vulnerabilities, decentralized oracle networks have evolved into generalized cross-chain messaging layers, led by the Chainlink Cross-Chain Interoperability Protocol (CCIP), alongside cross-chain systems like Axelar Network.
CCIP introduces an architectural innovation termed the Active Risk Management (ARM) Network.
Rather than relying on a single network of nodes to both propose and validate cross-chain transactions, CCIP separates responsibilities across two independent networks written in completely distinct software languages:
This defense-in-depth architecture prevents a single compromised key or software bug from catastrophic capital loss.
Traditional insurance models are plagued by extreme operational overhead. When a farmer experiences drought or a traveler encounters a canceled flight, policyholders must submit paperwork, wait for claims adjusters to manually investigate damages, and endure weeks or months of bureaucratic delays.
Parametric Insurance replaces subjective human claims assessment with deterministic mathematical code executed by smart contracts.
Public ledgers face intense regulatory pressure from compliance frameworks such as the FATF Travel Rule and European MiCA regulations. However, forcing users to post passports, tax documents, or banking statements on public ledgers violates foundational privacy rights.
Advanced oracle systems resolve this tension through Zero-Knowledge Web Attestation:
Protocols utilizing DECO by Chainlink Labs and TLSNotary enable individuals to prove creditworthiness, accredited investor status, or legal citizenship directly from existing Web2 portals without requiring those institutions to deploy blockchain APIs.
Similarly, identity protocols such as World Network and Privado ID utilize zero-knowledge proofs to establish human uniqueness, integrating with standards set by the World Wide Web Consortium (W3C) and credential attestation, protecting decentralized voting systems from Sybil manipulation.
Smart contracts are fundamentally passive software artifacts. They cannot execute themselves on a timer or run scheduled background daemon threads. If a loan falls below its collateral maintenance margin on Aave Protocol or Spark Protocol, or if an automated market maker pool on Curve Finance or Balancer requires periodic fee harvesting, an external account must initiate a transaction and pay the associated gas fee.
Historically, protocols relied on centralized cron scripts running on AWS EC2 instances to trigger contract maintenance. If the server crashed, failed to pay gas, or suffered network connectivity issues, liquidations froze, accumulating bad debt across the protocol.
Decentralized oracle networks have resolved this operational vulnerability through Automated Keepers and Decentralized Computation:
Services such as Chainlink Automation, Gelato Network, and OpenZeppelin Defender provide continuous off-chain computation. They execute complex monitoring logic off-chain without consuming on-chain gas, submitting settlement transactions only when predefined state conditions are satisfied.
Beyond purely financial mechanics, oracles power dynamic Non-Fungible Tokens (dNFTs) whose metadata and visual characteristics evolve based on external reality:
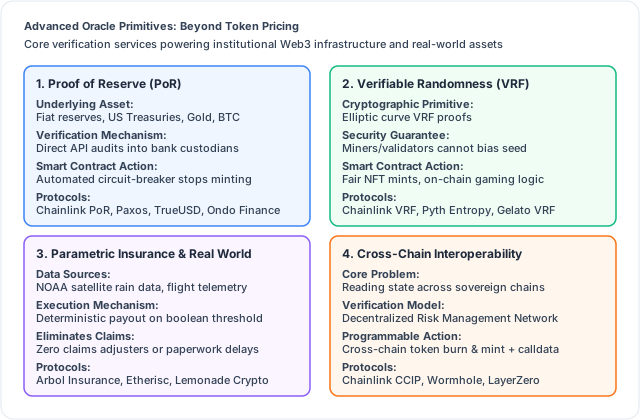
The table below summarizes the technical characteristics and operational profiles of advanced oracle applications:
As public blockchains expand into institutional finance, artificial intelligence, and physical infrastructure, decentralized oracles are cementing their role as the primary compute and data attestation engines of the internet.
By providing verifiable truth, provable randomness, and decentralized computation across deterministic state machines, oracle networks transform isolated distributed ledgers into comprehensive decentralized computers capable of coordinating real-world human enterprise.
Explore more guides and career playbooks