Loading article...

An architectural guide to Web3 reputation systems, soulbound tokens, verifiable credentials, zero-knowledge proofs, and decentralized identity scoring algorithms.
In traditional web paradigms, credit scores, background checks, and identity verification rely on centralized clearinghouses like Experian, Equifax, or LinkedIn. These centralized data silos control access to financial capital access, employment opportunities, and social proof. Public blockchain network infrastructure offers an alternative built on pseudonymous wallet interactions where users interact directly with smart contract protocols.
Pseudonymity introduces systemic operational challenges. When a cryptographic wallet address interacts with a decentralized application, smart contracts cannot inherently distinguish between an automated Sybil bot network, a malicious actor preparing a flash loan attack, or a seasoned protocol contributor with years of verified governance participation. Traditional decentralized finance protocol architectures rely heavily on overcollateralization to manage default risk because smart contracts cannot assess human counterparty risk.
A Web3 reputation system resolves this fundamental trust barrier. By aggregating, scoring, and verifying historical on-chain transactions, protocol governance votes, developer commits, and cryptographic attestations, Web3 reputation systems construct a user-owned, portable digital identity. This detailed guide explores the mathematical foundations, zero-knowledge privacy mechanisms, data aggregation pipelines, and economic models powering decentralized reputation infrastructure across modern web3 ecosystems.
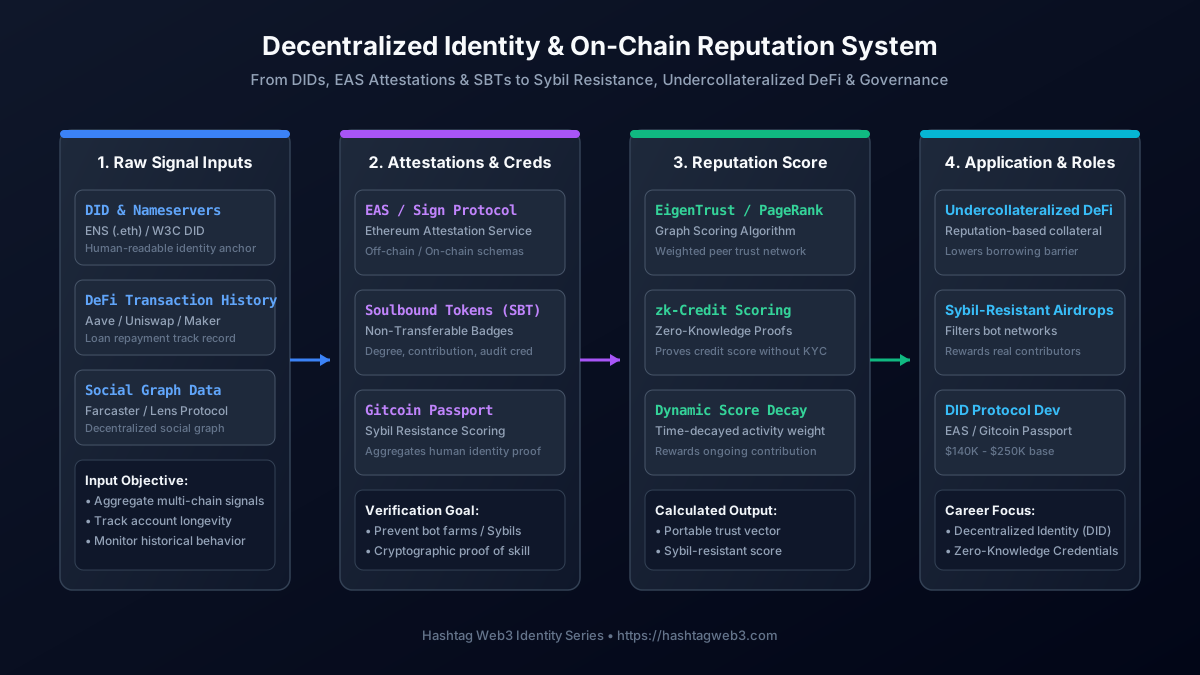
To construct a decentralized reputation system without relying on centralized identity authorities, Web3 protocols combine four foundational technical primitives into a cohesive verification stack.
A Decentralized Identifier is a globally unique, persistent, and cryptographically verifiable identifier that does not require a centralized registration authority. Defined by the W3C standard, a DID resolves to a DID Document containing cryptographic public keys, authentication services, and service endpoints.
In EVM ecosystems, public wallet addresses linked to name resolution services like Ethereum Name Service (ENS) serve as the primary human-readable entry points for DIDs. When an identity engine evaluates vitalik.eth, it queries the underlying resolver contract to map the human-readable string directly to ECDSA public keys and off-chain data pointers.
// Simplified interface for EIP-3643 / DID Resolver binding
interface IDIDRegistry {
    event DIDOwnerChanged(address indexed identity, address newOwner, uint256 previousChange);
    event DIDDelegateChanged(address indexed identity, bytes32 delegateType, address delegate, uint256 validTo, uint256 previousChange);

    function setOwner(address identity, address newOwner) external;
    function addDelegate(address identity, bytes32 delegateType, address delegate, uint256 validity) external;
    function validDelegate(address identity, bytes32 delegateType, address delegate) external view returns (bool);
}
While DIDs establish the identity root, Verifiable Credentials (VCs) and structured attestations encapsulate specific claims made about that identity by third-party entities.
Protocol frameworks such as the Ethereum Attestation Service (EAS) and Sign Protocol provide standardized smart contract interfaces for generating, indexing, and verifying on-chain and off-chain attestations. An attestation consists of a structured data payload signed by an issuer address, referencing a schema UID, recipient address, expiration timestamp, and optional revocation flag.
struct Attestation {
    bytes32 uid;
    bytes32 schema;
    uint64 time;
    uint64 expirationTime;
    uint64 revocationTime;
    bytes32 refUID;
    address recipient;
    address attester;
    bool revocable;
    bytes data;
}
Attestations support diverse use cases across the decentralized ecosystem:
Proposed by Vitalik Buterin, E. Glen Weyl, and Puja Ohlhaver in 2022, Soulbound Tokens are non-transferable non-fungible tokens bound permanently to a specific wallet address or "Soul."
Formalized through ERC-5192 (Minimal Soulbound Tokens) and ERC-4973 (Account-bound Tokens), SBTs prevent secondary market speculation on personal credentials. If a developer earns an audit credential or a university degree represented as a standard ERC-721 token, they could sell that token on OpenSea. ERC-5192 interface specifications block the transferFrom and safeTransferFrom functions, ensuring identity credentials remain strictly non-transferable.
A robust Web3 reputation score cannot rely on static badges alone. Modern reputation engines analyze dynamic execution state across multiple public ledger domains to aggregate transactional telemetry into multi-dimensional reputation matrices.
Decentralized Finance (DeFi) Execution History:
DAO Governance Engagement:
Developer Infrastructure Contributions:
Decentralized Social Graph Telemetry:
Simple transaction counting exposes reputation systems to artificial volume inflation through self-dealing wallet networks. Advanced scoring frameworks employ graph-theoretical algorithms modified from Google PageRank and EigenTrust, combined with temporal decay parameters.
To ensure that historical actions do not grant perpetual high scores to inactive accounts, scores decay exponentially over time unless reinforced by fresh activity:
$$R(t) = R_0 \cdot e^{-\lambda (t - t_0)}$$
Where $R(t)$ represents the current reputation score at time $t$, $R_0$ is the initial score earned at event timestamp $t_0$, and $\lambda$ is the exponential decay constant calibrated based on protocol governance parameters.
To measure trust in decentralized networks, protocols calculate peer-to-peer trust matrices where account $i$ assigns a local trust value $c_{ij}$ to account $j$ based on positive interactions:
$$t_{i}^{(k+1)} = (1 - a) C^T t_{i}^{(k)} + a p$$
Where $C$ represents the normalized trust matrix, $p$ is a pre-trusted seed vector consisting of known highly reputed entities, and $a$ is a dampening factor that bounds Sybil propagation across disconnected subgraphs.
| Platform | Primary Primitive | Storage Layer | Privacy Mechanism | Target Use Case |
|---|---|---|---|---|
| Ethereum Attestation Service (EAS) | Standardized Attestations | EVM Mainnet & L2s | Optional Off-Chain Hashes | Modular Credential Infrastructure |
| Gitcoin Passport | Stamps & Sybil Deduplication | Ceramic Network | Merkle Proof Verification | Airdrop Protection & Grant Allocation |
| Polygon ID / Privado ID | Verifiable Credentials | Polygon & EVM | Zero-Knowledge Proofs (circom) | Sybil-Resistant KYC & Compliance |
| Galxe (Passport) | Credentials & SBTs | IPFS & EVM | Encrypted Identity Vaults | Community Engagement & Quests |
| Otterspace | Non-Transferable Badges (SBTs) | Optimism / Arbitrum | Public On-Chain State | DAO Governance & Contributor Tracking |
Public blockchains record every state change permanently. Storing personal credentials, identity attributes, or credit history directly on-chain creates severe privacy risks, exposing users to public surveillance and identity theft.
Modern Web3 reputation architectures integrate Zero-Knowledge Proofs (zk-SNARKs) to separate identity verification from data disclosure.
Below is a conceptual Circom circuit demonstrating how a user proves their reputation score exceeds a required protocol threshold without revealing their exact score:
pragma circom 2.1.6;

include "../node_modules/circomlib/circuits/comparators.circom";
include "../node_modules/circomlib/circuits/poseidon.circom";

template ReputationThresholdProof() {
/ Private Signals (Known only to the Prover)
    signal input userReputationScore;
    signal input userPrivateKey;

/ Public Signals (Known to the Verifier / On-Chain Contract)
    signal input minimumRequiredScore;
    signal input publicIdentityCommitment;

/ Output Signal
    signal output isValid;

/ 1. Verify identity commitment matching Poseidon(privateKey)
    component hasher = Poseidon(1);
    hasher.inputs[0] <== userPrivateKey;
    publicIdentityCommitment === hasher.out;

/ 2. Check if score is greater than or equal to threshold
    component gte = GreaterEqThan(32);
    gte.in[0] <== userReputationScore;
    gte.in[1] <== minimumRequiredScore;

/ 3. Constrain output to valid binary outcome
    isValid <== gte.out;
    isValid === 1;
}

component main {public [minimumRequiredScore, publicIdentityCommitment]} = ReputationThresholdProof();
Through this zero-knowledge approach, a user can demonstrate to an undercollateralized DeFi lending protocol that their aggregated credit score exceeds 750 without revealing their transaction history or real-world name.
Web3 reputation infrastructure unlocks economic models across decentralized applications that previously required centralized intermediaries.
Traditional DeFi protocols like Aave require borrowers to deposit 125% to 150% of their loan value in collateral to protect lenders against default. This collateral inefficiency limits DeFi adoption for everyday financial applications.
By integrating verifiable reputation scoring engines, protocols can offer tiered collateral ratios:
In standard one-token-one-vote governance models, capital concentration enables whales to outvote broad community consensus. Furthermore, pure one-person-one-vote systems are vulnerable to Sybil attacks, where an attacker generates thousands of automated wallet addresses to manipulate voting outcomes.
Quadratic voting and quadratic funding models mathematically balance funding allocations by weighting the number of individual contributors more heavily than total capital raised:
$$\text{Allocation} \propto \left( \sum_{i=1}^{N} \sqrt{c_i} \right)^2$$
Reputation systems integrated into platforms like Gitcoin Grants verify that each contributor $i$ possesses a unique, high-confidence human reputation score, preventing attackers from splitting funds across automated sub-wallets to extract grants illegitimately.
Hiring in Web3 often suffers from resume inflation and unverified claims. Decentralized labor platforms utilize reputation attestations to verify skills directly:
Recruiters and decentralized autonomous organizations evaluate applicants using verifiable on-chain credentials rather than unverified PDF resumes.
Designing secure reputation systems requires mitigating unique attack vectors native to pseudonymous cryptographic networks.
An attacker creates thousands of sub-wallets, executing low-value transactions between them to simulate authentic user activity.
Mitigation: Reputation engines incorporate cost-of-forge metrics. By requiring historical gas expenditures, minimum holding periods, or cross-chain bridge attestations, protocols make large-scale Sybil generation economically unviable.
A coalition of malicious accounts assigns maximum trust scores to one another, artificially inflating their standing within local reputation subgraphs.
Mitigation: Machine learning graph analysis tools like Spectral and Karma detect dense, isolated subgraphs exhibiting abnormal transaction reciprocity. The scoring algorithm applies dampening factors to discount self-contained loops.
Because a wallet address is controlled by a private key, a user with a high reputation score could sell their seed phrase to a third party, transferring their established trust to an untrusted actor.
Mitigation: Systems combine static wallet scoring with dynamic behavioral biometrics and zero-knowledge identity assertions tied to real-world attributes (e.g., biometric hardware enclaves or multi-factor social recovery guardians).
As public blockchain ecosystems expand toward institutional finance and real-world asset tokenization, decentralized reputation systems will transition from optional governance tools into fundamental web infrastructure.
Future technical developments focus on several key areas:
By establishing verifiable, privacy-preserving, and user-owned identity frameworks, Web3 reputation systems build the foundation for a transparent, efficient, and equitable global digital economy.
Web2 reputation systems are isolated within proprietary databases controlled by single companies (e.g., credit bureaus, Uber passenger ratings, eBay seller scores). Web3 reputation systems store credentials on public blockchains using open standards, giving users complete ownership over a portable digital identity that operates across any compatible application.
No. Standard Web3 reputation implementations rely on non-transferable primitives like EIP-5192 Soulbound Tokens (SBTs) and zero-knowledge identity commitments bound directly to a user's wallet address or Decentralized Identifier (DID).
Zero-knowledge proofs allow a user's wallet to mathematically prove that their off-chain or on-chain data satisfies specific conditions (e.g., having a credit score above a required threshold or holding a valid identity credential) without revealing the underlying transaction history, personal data, or exact numbers to the public blockchain.
Protocols mitigate account selling through behavioral telemetry, multi-factor social graph verification, dynamic attestation renewals, and social recovery mechanisms tied to trusted guardians, making private key purchases unreliable for malicious buyers.
Explore more guides and career playbooks