Loading article...
A comprehensive technical guide to Decentralized Identifiers (DIDs), W3C standards, Verifiable Credentials, Zero-Knowledge proofs, and smart contract registry implementation.
Centralized identity systems rely on centralized authorities (such as Google, Meta, or state identity registries) to issue, manage, and verify user digital identities. This architecture creates single points of failure, invasive tracking across web applications, and data loss risks when central entities suffer security breaches or revoke access.
Decentralized Identifiers (DIDs) are a foundational cryptographic standard specified by the World Wide Web Consortium (W3C). DIDs enable self-sovereign, verifiable digital identities that operate independently of centralized registries, identity providers, and certificate authorities. This technical guide examines DID document architecture, W3C Verifiable Credentials (VCs), Zero-Knowledge proof integration, smart contract registries, and career opportunities in decentralized identity engineering.
A DID is a globally unique URI (Uniform Resource Identifier) string composed of three distinct parts:
                  w3c decentralized identifier (did) structure

       did : ethr : 0x1234567890abcdef1234567890abcdef12345678
      ───┬── ──┬─ ──────────────────────┬──────────────────────
         │     │                        │
       Scheme  DID Method         Specific Method Identifier
did:.ethr for Ethereum, ion for Bitcoin Sidetree, sol for Solana, key for raw public keys).Resolving a DID string yields a JSON-LD DID Document containing public key material, authentication suites, and service endpoints.
{
  "@context": [
    "https://www.w3.org/ns/did/v1",
    "https://w3id.org/security/suites/ed25519-2020/v1"
  ],
  "id": "did:ethr:0x1234567890abcdef1234567890abcdef12345678",
  "verificationMethod": [
    {
      "id": "did:ethr:0x1234567890abcdef1234567890abcdef12345678#controller",
      "type": "EcdsaSecp256k1RecoveryMethod2020",
      "controller": "did:ethr:0x1234567890abcdef1234567890abcdef12345678",
      "blockchainAccountId": "eip155:1:0x1234567890abcdef1234567890abcdef12345678"
    }
  ],
  "authentication": [
    "did:ethr:0x1234567890abcdef1234567890abcdef12345678#controller"
  ],
  "assertionMethod": [
    "did:ethr:0x1234567890abcdef1234567890abcdef12345678#controller"
  ],
  "service": [
    {
      "id": "did:ethr:0x1234567890abcdef1234567890abcdef12345678#identity-hub",
      "type": "IdentityHub",
      "serviceEndpoint": "https://hub.hashtagweb3.com/identity"
    }
  ]
}
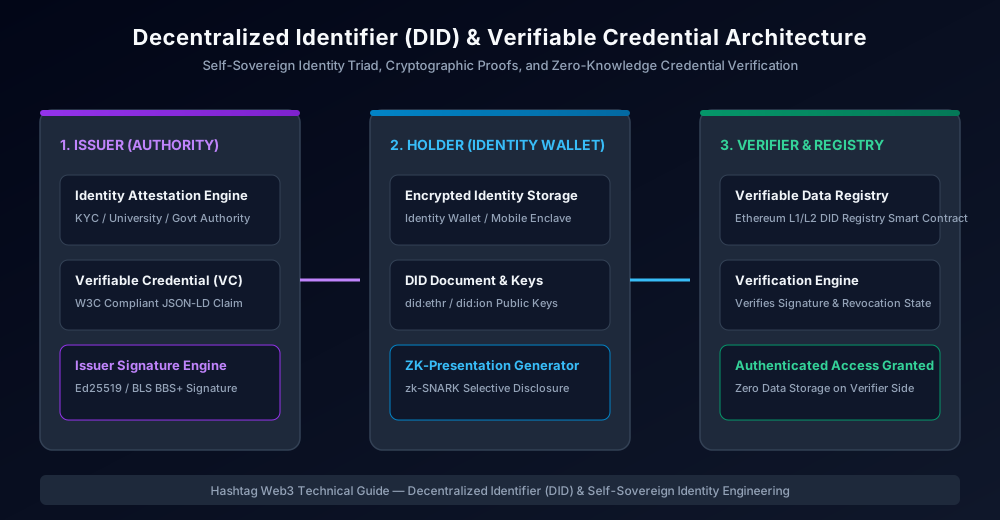
Decentralized identity relies on three primary actors interacting through cryptographic proofs.
                            THE SSI TRUST TRIANGLE

                      ┌─────────────────────────┐
                      │    ISSUER (Authority)   │
                      └────────────┬────────────┘
                                   │ (Issues Verifiable Credential)
                                   ▼
                      ┌─────────────────────────┐
                      │  HOLDER (User Wallet)   │
                      └────────────┬────────────┘
                                   │ (Presents Verifiable Presentation)
                                   ▼
                      ┌─────────────────────────┐
                      │    VERIFIER (dApp)      │
                      └────────────┬────────────┘
                                   │ (Queries DID Registry / Blockchain)
                                   ▼
                      ┌─────────────────────────┐
                      │  VERIFIABLE REGISTRY    │
                      └─────────────────────────┘
A Verifiable Credential (VC) is a tamper-evident digital credential containing claims certified by an Issuer's cryptographic signature.
Standard digital signatures (like ECDSA or Ed25519) require revealing the entire credential to verify the signature. If a VC contains a user's date of birth, home address, and passport number, presenting the VC to prove "Age > 21" exposes unnecessary PII.
Using BBS+ Signatures or zk-SNARKs (such as Polygon ID or Anon Aadhaar), holders generate a Zero-Knowledge Proof that proves specific predicates (e.g., age >= 21 or country != sanctioned) without revealing raw underlying attributes.
// CONCEPTUAL ZERO-KNOWLEDGE CREDENTIAL VERIFIER CONTRACT
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

interface IZkVerifier {
    function verifyProof(
        bytes calldata proof,
        uint256[] calldata publicInputs
    ) external view returns (bool);
}

contract ZkIdentityGate {
    IZkVerifier public immutable zkVerifier;
    mapping(bytes32 => bool) public processedNullifiers;

    event IdentityVerified(bytes32 indexed nullifier);

    constructor(address _zkVerifier) {
        zkVerifier = IZkVerifier(_zkVerifier);
    }

// Verify a ZK proof of age/nationality without revealing identity attributes
    function verifyIdentity(
        bytes calldata proof,
        uint256[] calldata publicInputs,
        bytes32 nullifier
    ) external {
        require(!processedNullifiers[nullifier], "Nullifier already used");
        require(zkVerifier.verifyProof(proof, publicInputs), "Invalid ZK proof");

/ Prevent double-use of credential presentation
        processedNullifiers[nullifier] = true;

        emit IdentityVerified(nullifier);
    }
}
did:ethr)On EVM blockchains, DID resolution relies on lightweight registry smart contracts (such as ERC-1056 EthereumDIDRegistry).
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

contract SimpleDIDRegistry {
    mapping(address => address) private _owners;
    mapping(address => mapping(bytes32 => mapping(address => uint256))) private _delegates;
    mapping(address => uint256) private _changed;

    event DIDOwnerChanged(address indexed identity, address newOwner, uint256 previousChange);
    event DIDDelegateChanged(
        address indexed identity,
        bytes32 delegateType,
        address delegate,
        uint256 validUntil,
        uint256 previousChange
    );

    function identityOwner(address identity) public view returns (address) {
        address owner = _owners[identity];
        if (owner == address(0)) {
            return identity; // Default owner is the address itself
        }
        return owner;
    }

    function changeOwner(address identity, address newOwner) public {
        require(msg.sender == identityOwner(identity), "Not DID owner");
        _owners[identity] = newOwner;
        emit DIDOwnerChanged(identity, newOwner, _changed[identity]);
        _changed[identity] = block.timestamp;
    }

    function addDelegate(
        address identity,
        bytes32 delegateType,
        address delegate,
        uint256 validity
    ) public {
        require(msg.sender == identityOwner(identity), "Not DID owner");
        uint256 validUntil = block.timestamp + validity;
        _delegates[identity][delegateType][delegate] = validUntil;
        emit DIDDelegateChanged(identity, delegateType, delegate, validUntil, _changed[identity]);
        _changed[identity] = block.timestamp;
    }
}
Decentralized applications require Sybil resistance to prevent malicious actors from creating thousands of synthetic DIDs to farm airdrops, manipulate DAO votes, or drain quadratic funding pools.
Decentralized identity is actively transforming enterprise systems beyond Web3 crypto applications:
A major vulnerability of self-sovereign identity is seed phrase management. If a user loses their private key, they risk losing access to their entire digital identity.
Modern DID implementations utilize Account Abstraction smart contract wallets (ERC-4337) with built-in social recovery guardians:
[User Wallet (Key Lost)] ──► [Guardian A (Friend)] ──┐
                                                    ├──► (2-of-3 Threshold Approval) ──► [Key Reset]
                             [Guardian B (Hardware)] ──┤
                                                    │
                             [Guardian C (Passkey)] ──┘
In long-lived identity systems, Issuers must have the ability to revoke credentials (e.g., revoking a driver's license or revoking a compromised security clearance) without compromising user privacy.
revocationListIndex. To check validity, the Verifier fetches the bitmap byte and evaluates whether the target index bit is 0 (Valid) or 1 (Revoked).Storing heavy DID Document metadata or public profile credentials directly on Ethereum L1 is cost-prohibitive. Decentralized identity systems store claims using off-chain decentralized data networks:
Identity in Web3 is fragmented across multiple Layer 1 chains and Layer 2 rollups. Cross-chain DID resolution frameworks bind heterogeneous addresses to unified human-readable handles:
.eth domains to underlying DID documents across EVM and non-EVM chains via CCIP-Read (EIP-3668) off-chain gateways.Decentralized identity frameworks must interface with global regulatory privacy standards, including the EU's eIDAS 2.0 regulations for European Digital Identity Wallets and GDPR compliance:
As autonomous AI agents execute transactions on-chain, DIDs provide cryptographic identity frameworks for artificial intelligence agents:
did:key / did:jwk): Assigning unique cryptographic DIDs to AI agents, enabling agents to authenticate against APIs, sign smart contract calls, and present delegation credentials authorized by human controllers.The Ethereum Attestation Service (EAS) provides an open-source primitive for making on-chain and off-chain attestations about any subject DID:
// SECURE ATTESTATION INTEGRATION EXAMPLE
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

interface IEAS {
    struct Attestation {
        bytes32 uid;
        bytes32 schema;
        uint64 time;
        uint64 expirationTime;
        uint64 revocationTime;
        bytes32 refUID;
        address recipient;
        address attester;
        bool revocable;
        bytes data;
    }

    function getAttestation(bytes32 uid) external view returns (Attestation memory);
}

contract AttestationGate {
    IEAS public immutable eas;
    bytes32 public immutable requiredSchema;

    constructor(address _eas, bytes32 _schema) {
        eas = IEAS(_eas);
        requiredSchema = _schema;
    }

    function verifyAttestationUID(bytes32 uid, address expectedRecipient) public view returns (bool) {
        IEAS.Attestation memory attestation = eas.getAttestation(uid);

        require(attestation.schema == requiredSchema, "Invalid schema");
        require(attestation.recipient == expectedRecipient, "Recipient mismatch");
        require(attestation.revocationTime == 0, "Attestation revoked");
        require(attestation.expirationTime == 0 || attestation.expirationTime > block.timestamp, "Attestation expired");

        return true;
    }
}
When choosing a DID method for production Web3 identity architecture, protocol engineers must balance decentralization, resolution latency, storage overhead, and transaction fees.
| DID Method | Underlying Registry / Transport | Resolution Latency | Cost / Transaction Fee | Key Rotation Mechanism | Primary Target Use Case |
|---|---|---|---|---|---|
did:ethr |
Ethereum Mainnet / EVM L2s | High (RPC block lookup) | Gas fee on rotation | Smart contract state update | On-chain dApps & DeFi compliance |
did:key |
Self-describing Cryptographic Key | Instantiated locally (0ms) | Free (No registry required) | Immutably bound to public key | Static key exchange & ephemeral P2P messaging |
did:ion |
Bitcoin Sidetree Protocol / IPFS | Medium (Sidetree node query) | Batch transaction fee | Sidetree operation delta chain | High-scale enterprise digital credentials |
did:cheqd |
cheqd Cosmos SDK App-Chain | Low (Cosmos RPC node) | Minimal CHEQ token gas | Native Cosmos state transactions | Commercial SSI networks & identity wallets |
did:peer |
Direct Peer-to-Peer Protocol | Instantaneous local cache | Free (No ledger required) | Peer exchange of updated documents | Micro-services & private agent-to-agent channels |
did:key: Encodes raw public key material directly into the DID string format using Multicodec and Base58Btc. Because there is no underlying blockchain registry, did:key documents cannot support cryptographic key rotation or service endpoint update operations. Updating a key creates a completely distinct did:key identity string.
did:ethr: Utilizes the EIP-1056 Lightweight Identity Registry smart contract deployed across EVM-compatible networks. A DID string maps directly to a 20-byte EVM address. Public key updates, delegate additions, and service endpoint configurations are recorded as EVM contract storage updates, maintaining a history of identity state changes without requiring high-maintenance custom node infrastructures.
did:ion: Built on the Sidetree protocol over Bitcoin and IPFS, ION provides massive throughput by batching thousands of identity operation payloads into single Bitcoin transactions. ION resolves DID documents by fetching IPFS content hashes anchored in Bitcoin transactions, allowing scalable enterprise credential issuing without saturating layer-1 block space.
Understanding production implementations illustrates how DIDs and Verifiable Credentials operate in high-throughput enterprise and Web3 environments.
World Network uses did:world to issue uniqueness credentials based on biometric proofs generated by Orb hardware.
did:world credential without revealing their specific identity or wallet address.The European Union's updated eIDAS 2.0 framework mandates that all EU Member States provide citizens with a digital identity wallet based on W3C Decentralized Identifier standards and ISO 18013-5 Mobile Driving License standards.
ageOver18 field rather than their full date of birth or home address.To build a decentralized identity verification pipeline for a Web3 application, follow this software implementation sequence:
did-resolver and ethr-did-resolver packages to resolve did:ethr strings into canonical JSON-LD DID Documents.@veramo/core or walt.id SDKs to verify digital signatures on W3C Verifiable Credentials.As regulatory pressure for digital privacy increases (such as EU eIDAS 2.0 mandates for digital identity wallets), demand for identity protocol engineers is growing rapidly.
                          CAREER PROGRESSION ROADMAP

 [Software Engineer / Security]
           │
           ▼
 [Identity Protocol Engineer]  ──► (Master W3C DIDs, Verifiable Credentials)
           │
           ▼
 [Applied Cryptographer]        ──► (Master ZK-SNARKs, BBS+ Signatures)
           │
           ▼
 [Chief Identity Architect]    ──► (Enterprise SSI & Cross-Border Frameworks)
Decentralized Identity Engineer:
Applied ZK Cryptographer (Identity Focus):
Enterprise Identity Solutions Architect:
Candidates interviewing for Decentralized Identity Engineering positions are routinely evaluated on scenario-based technical questions.
Interview Question: "You are building a DeFi protocol that requires users to prove they are accredited investors using a Verifiable Credential. How do you prevent a malicious user from stealing another user's public VC and presenting it as their own?"
Structured Engineering Answer:
holder == subject).Interview Question: "If an identity holder loses their private key or suffers a device compromise, how does a smart-contract-based DID registry facilitate recovery without relying on a central administrator?"
Structured Engineering Answer:
DIDOwnerChanged event, mutating the DID controller pointer to a new key pair without changing the underlying DID URI.Decentralized Identifiers (DIDs) and Verifiable Credentials represent a fundamental evolution from centralized identity providers to user-owned, self-sovereign digital identity. By combining W3C standards, smart contract registries, zero-knowledge selective disclosure, and social recovery, DIDs enable secure, privacy-preserving authentication across Web3 and enterprise applications.
Mastering DID document resolution, ZK credential verification, and account abstraction provides a direct foundation for a high-impact career in decentralized identity engineering.
Explore more guides and career playbooks