Loading article...

An empirical comparative thesis examining the structural, cryptographic, and economic differences between sovereign sidechains and inherited Layer 2 rollups, focusing on bridge security, consensus models, and failure modes.
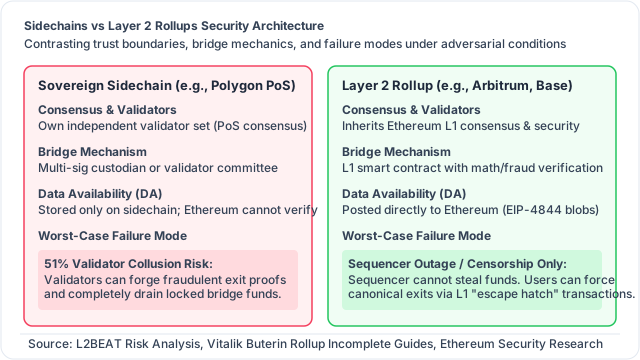
In the quest to scale decentralized computation beyond the throughput limits of base settlement networks like the Ethereum Foundation mainnet, two primary architectures have emerged: sidechains and Layer 2 (L2) rollups. While both frameworks process transactions outside the base layer to achieve high throughput and low execution fees, they are governed by diametrically opposed security paradigms.
A sidechain is an independent, sovereign blockchain running parallel to a base chain, connected through a two-way bridge and secured by its own validator set. A Layer 2 rollup is an execution network that processes transactions off-chain but posts compressed transaction data and state proofs directly to the base chain, mathematically inheriting the security, decentralization, and consensus finality of the underlying Layer 1.
Understanding the difference between these two paradigms is not merely a semantic distinction. It represents the difference between trusting an independent consortium of third-party validators and trusting the unforgeable laws of cryptographic verification.
To understand the operational division between sidechains and rollups, one must analyze where transaction validation, data availability, and dispute resolution take place.
A sidechain operates as an autonomous economic network:
A Layer 2 rollup functions as a cryptographic extension of the base layer:
The critical vulnerability in any scaling solution is the bridge connecting off-chain execution to base-layer liquidity. Comparing how sidechains and rollups handle cross-domain asset transfers reveals the fundamental security divide:
To transfer Ether or ERC-20 tokens to a sidechain:
The fundamental flaw in this architecture is that the Ethereum bridge contract possesses zero mathematical verification of the sidechain state. The Ethereum contract simply checks whether the incoming withdrawal request contains valid signatures from the sidechain validator committee.
If a malicious majority of sidechain validators colludes (or if their private signing keys are compromised via phishing, social engineering, or server intrusions), they can sign fraudulent withdrawal proofs. The Ethereum contract will release locked funds to the attackers, completely draining the bridge treasury even if the user never initiated a transaction.
A Layer 2 rollup bridge does not rely on human attestations or committee trust:
Even if 100% of L2 sequencers attempt to forge an invalid withdrawal, the Ethereum smart contract will mathematically reject the transaction. Stolen funds cannot be withdrawn from a canonical rollup bridge because the base layer acts as an impartial judicial verifier.
The true measure of a distributed system is its resilience under catastrophic failure or adversarial compromise:
forceInclusion or enqueue function). If the sequencer fails to process the forced transaction within a predefined grace period, the rollup enters emergency mode, allowing users to unilaterally withdraw their assets directly to Ethereum mainnet.These technical realities are monitored and graded by L2BEAT, which tracks whether scaling solutions offer genuine escape hatches (Stage 1 and Stage 2 rollups) or rely on administrative multisigs.
A subtle but critical difference between sidechains and rollups lies in the handling of transaction data availability:
In a sidechain, transaction data remains on the sidechain. Ethereum nodes do not store or verify sidechain block contents. If sidechain validators collude to produce a block and withhold the block data from the public (a data withholding attack), users cannot prove their account balances, and the network can be held hostage.
In a Layer 2 rollup, transaction data is posted directly to Ethereum consensus nodes using EIP-4844 blob containers. Even if the L2 sequencer permanently deletes its servers and vanishes, any participant running a standard Ethereum node can download the historical blob payloads, replay every state transition from genesis, reconstruct the complete Merkle state tree, and generate an unforgeable Merkle proof to withdraw their funds on Ethereum L1.
The theoretical vulnerabilities of sidechains have manifested in real-world security disasters that shaped the development of modern Layer 2 rollups:
In March 2022, the Ronin Network, an independent gaming sidechain developed for Axie Infinity, suffered one of the largest financial exploits in computer science history, documented by the U.S. Department of the Treasury and Chainalysis Research.
The Ronin sidechain was secured by a Proof of Authority validator set requiring 5 out of 9 validator signatures to authorize withdrawals from its Ethereum bridge. Adversaries executed spear-phishing attacks against Sky Mavis employees, compromising four validator private keys, alongside a fifth key obtained via a third-party Axie DAO RPC node.
With 5 of 9 keys in hand, the attackers forged withdrawal requests directly to the Ethereum bridge contract, extracting 173,600 ETH and 25.5 million USDC without performing any invalid transactions on the sidechain itself. Had Ronin operated as a true Layer 2 rollup with cryptographic fraud proofs or ZK validity verifiers, the Ethereum contract would have evaluated the mathematical state transition and blocked the transfer, rendering the compromised keys useless.
In August 2021, Poly Network, a cross-chain sidechain protocol, was exploited due to an authorization bypass in its bridge smart contract management logic. The contract allowed an external caller to trigger an internal function that changed the registered "Keeper" public keys. The attacker designated their own address as the sole validator and proceeded to drain hundreds of millions of dollars across Ethereum, Binance Smart Chain, and Polygon.
Recognizing the fundamental limitations of the sidechain security model, Polygon Technology initiated a massive multi-year architectural transition known as Polygon 2.0.
Rather than maintaining Polygon PoS as an isolated sidechain, the network is upgrading its consensus engine into a ZK-powered Validium and deploying the AggLayer (Aggregation Layer). By compiling execution into zero-knowledge circuits and posting validity proofs to Ethereum, Polygon is converting its massive liquidity and user base from a sovereign sidechain into an Ethereum-secured rollup ecosystem.
Operating a sidechain versus a Layer 2 rollup creates radically different economic flows:
Sidechains must maintain high native token valuations to ensure security. If the market capitalization of the staking token crashes, the capital cost to execute a 51% attack diminishes. As a consequence, sidechains must distribute continuous block rewards (token inflation) to validators, diluting token holders over time.
Layer 2 rollups do not require inflationary token issuance to maintain basic consensus security. The security is already paid for by Ethereum mainnet stakers. Rollup operators collect gas fees from users, pay wholesale blob fees to Ethereum validators, and retain the spread as sequencer gross profit, tracked transparently on Token Terminal and DefiLlama.
For engineering leads evaluating where to launch a decentralized protocol, this matrix establishes the key decision criteria:
Deploy on a Layer 2 Rollup if you are building decentralized financial primitives, automated market makers like Uniswap Labs, collateralized lending markets like Aave, or institutional asset tokenization platforms where bridge security and censorship resistance are paramount.
Deploy on a Sovereign Sidechain or Subnet if your application requires a custom consensus mechanism, compliance-enforced permissioned validator sets, or unconstrained execution where low security guarantees are acceptable in exchange for complete operational autonomy.
Explore more guides and career playbooks