Loading article...

Attackers broke into Luxor's Commander fleet software and pointed more than a dozen customer accounts at the OCEAN pool, prompting CEO Nick Hansen to warn that AI-enabled attacks are speeding up.
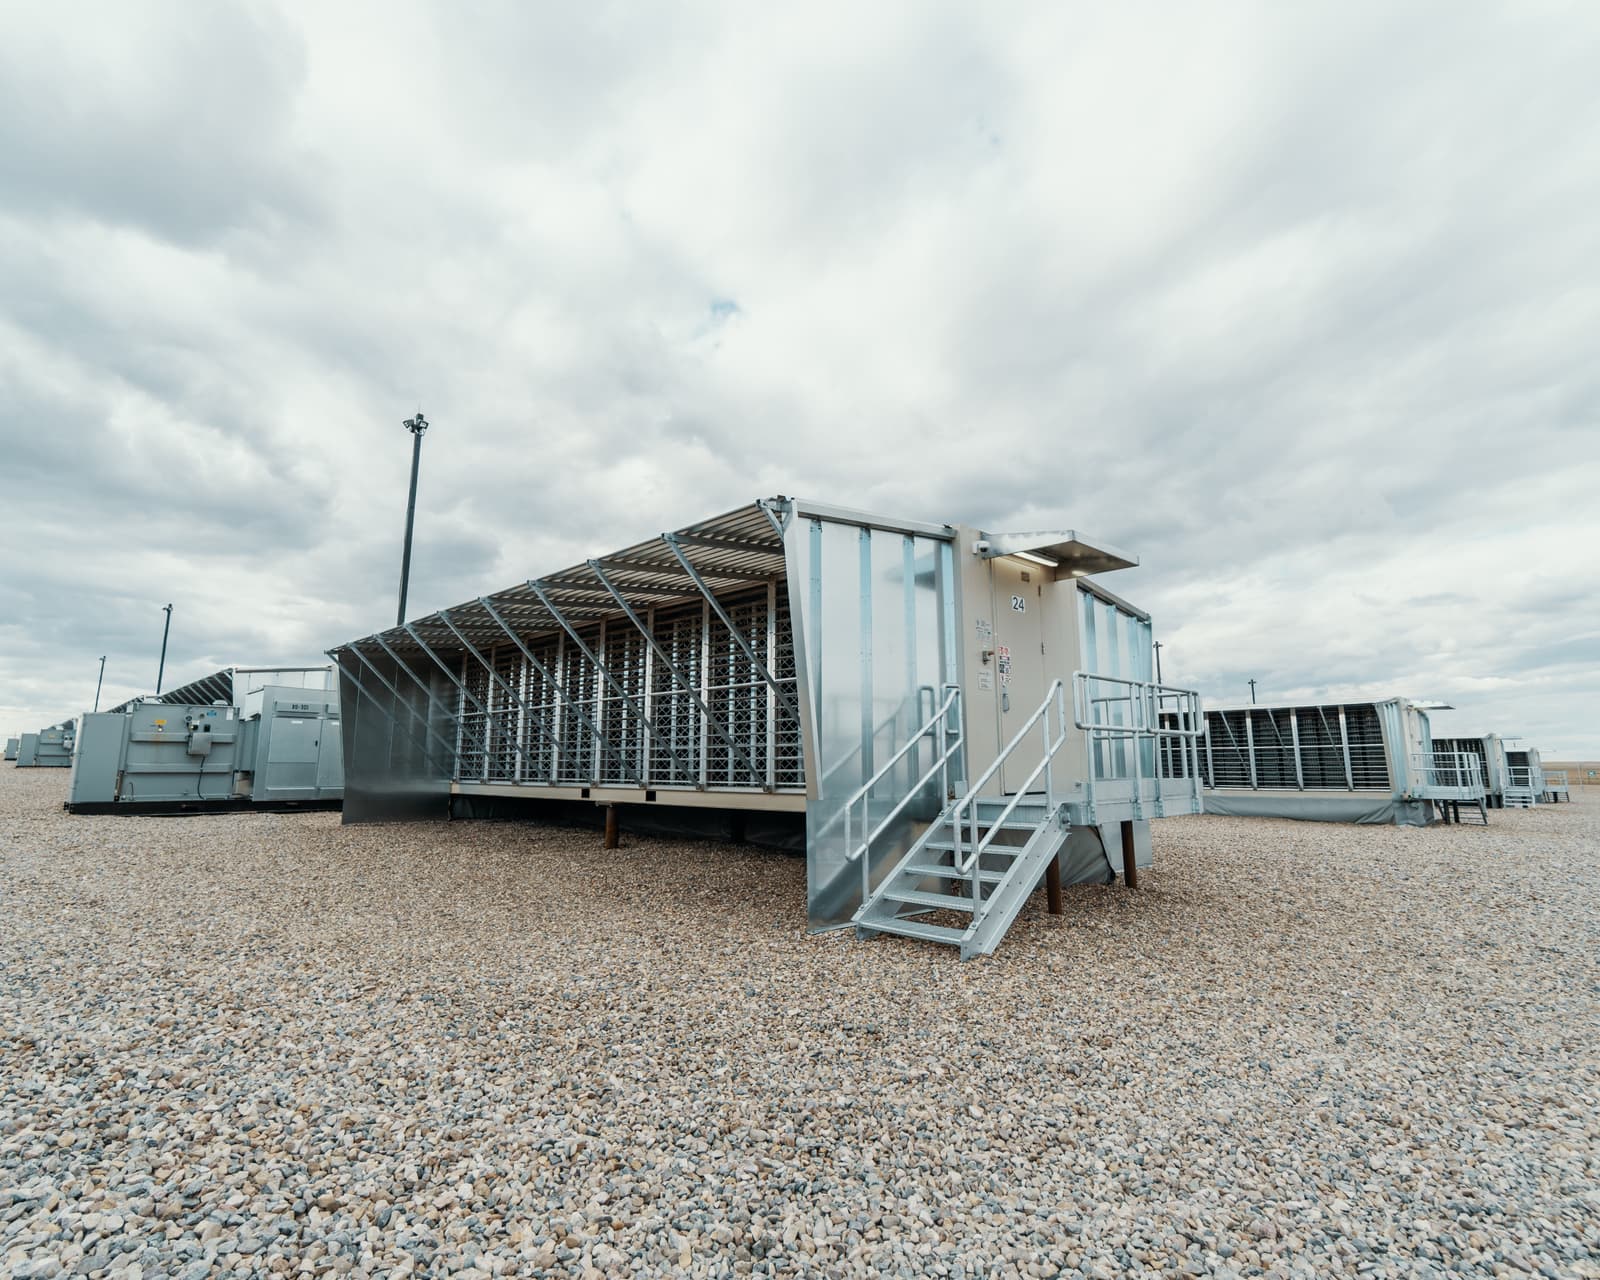
A Bitfury BlockBox AC mining datacenter at Hut 8's site in Medicine Hat, Alberta. Photo: Curtis Huisman via Wikimedia Commons (CC BY 4.0). Source
Luxor, a Bitcoin mining services company, said attackers broke into its Commander fleet-management software and redirected computing power from more than a dozen customer accounts to a different mining pool, a breach the company confirmed on Nov. 15. The intrusion started at about 6:00 PM PDT on Nov. 14, Crypto Briefing reported, and pointed the hashrate of affected accounts to the OCEAN pool, so the machines kept running while the rewards went elsewhere.
Luxor said it patched the vulnerability within two hours of detecting the unauthorized changes and began restoring affected machines to their original pool settings. The company said the incident was isolated to the Commander tool and that none of its other services, including Luxor Pool and the LuxOS firmware, were affected. No customer data was taken, the report said. Luxor also pledged to compensate affected customers in full for redirected mining power and to publish a post-mortem. Customers will be credited as though their hashrate had performed normally through the incident window.
A mining pool combines computing power from many operators and splits the rewards. Redirecting a miner's hashrate to a different pool with a different payout address leaves the operator paying the electricity bill while someone else collects the bitcoin, the report explained. Cointelegraph said it contacted Luxor for comment.
The scale of the diversion is still disputed. Initial reports suggested about 64,000 mining machines representing 13 exahashes per second were moved to OCEAN on Saturday, but Luxor has not confirmed either figure, saying instead that the incident affected just over a dozen customer accounts, Cointelegraph reported. The peak hashrate diverted is estimated at around 13 EH/s, roughly 1.4% of the network's total at the time.
The payout address tied to the redirected hashrate received about 0.162 BTC during the attack window, worth roughly $10,500, according to Crypto Briefing. A Bitcoin address that analytics firm CoreX identified as associated with the incident received two OCEAN payouts totaling approximately 0.162 BTC, Cointelegraph reported.
Chief executive Nick Hansen said in an X post on Sunday that the attack came through a "sophisticated AI-enabled vector," without specifying how AI was used. "At this moment, anyone running any sort of substantial business, especially in crypto, is inundated with AI-enabled attacks," Hansen wrote. "This does not seem to be slowing down; rather, it's speeding up as models get better and more attackers enter the arena."
Hansen also wrote that "abliterated models are running 24/7 against your entire surface, looking for a little crack, which they then use to (almost instantly) expand." Abliterated models are programs that have had their built-in refusal behavior stripped out, so they will produce exploit code that a standard chatbot would decline to write.
Luxor has put the majority of its feature work on hold in order to harden its cybersecurity, Hansen said, and the company bought its own GPUs to run unrestricted open-weight AI models aimed at improving its security posture. He urged operators of similar services to do the same. "It's your only defense in this new AI-powered dark forest," Hansen wrote, quoting an old line about stopping armed attackers with armed defenders.
The warning follows a string of reported AI-assisted intrusions targeting crypto businesses. India's cybersecurity agency warned earlier in November that a group called Crafty Falcon was using AI-powered tools to attack financial companies including exchanges. Chainalysis disclosed in October that an attacker used what it called "offensive agentic techniques" to reach its systems, exposing password hashes, live tokens and other customer information. Anthropic said in a September report that multiple groups had built "automated exploit foundries" that speed up vulnerability research, testing and exploit design.
Initial reports suggested the attackers collected no mining rewards, but the CoreX-linked address later showed two OCEAN payouts during the incident window.