Loading article...

A transition blueprint for Web2 security professionals moving into Web3, covering EVM security primitives, reentrancy vulnerabilities, formal verification, fuzzing tools, and audit methodologies.

Cybersecurity in Web3 operates under fundamentally different threat models than traditional Web2 application security. In Web2, security relies on perimeter defense, role-based access control (RBAC), and private server environments where software patches can be deployed immediately upon vulnerability discovery. In Web3, smart contracts are deployed to immutable, public execution environments where code is open source, financial assets are directly controlled by contract logic, and exploits execute atomically without rollbacks.
For Web2 security engineers, penetration testers, and application security (AppSec) specialists, transitioning to Web3 offers high-impact career opportunities in smart contract auditing, protocol security engineering, and real-time threat monitoring. This comprehensive guide outlines the mental models, technical tools, audit methodologies, and practical steps required to successfully transition into a Web3 Cybersecurity Specialist.
To succeed in Web3 cybersecurity, security professionals must adjust their core security assumptions and threat modeling frameworks.
                         WEB2 vs WEB3 SECURITY PARADIGMS

 Dimension               Web2 Application Security       Web3 Smart Contract Security
──────────────────────────────────────────────────────────────────────────────────────────
 Execution Environment   Private Servers / Cloud VPCs    Public, Immutable EVM Ledger
 Source Code Access      Proprietary / Closed Source     Open Source / Verifiable Bytecode
 Patch Capability        Instant Hotfixes / CI/CD        Immutable (Requires Proxy / Migration)
 Primary Target          User PII & Session Tokens       Direct Protocol Liquidity / Vaults
 Execution Atomicity     Multi-step Distributed DBs     Atomic Block Transactions (Flash Loans)
 Vulnerability Impact    Data Breach / Service Loss      Irreversible Economic Drainage
Transaction Atomicity and Flash Loans: In Web2, exploiting a complex multi-step vulnerability requires persistent state manipulation across separate HTTP sessions over extended timeframes. In Web3, an attacker can borrow tens of millions of dollars in uncollateralized capital via a single flash loan, execute arbitrage or price manipulation across multiple DEX protocols, drain a vulnerable vault, and repay the loan within a single, atomic block transaction.
Public State Visibility & Front-Running: Mempools are entirely transparent across public blockchains. When a security researcher or user broadcasts a transaction to interact with a contract, MEV bots and malicious searchers inspect pending transactions and can front-run or sandwich the execution by paying higher gas fees.
Immutability and Upgradability Patterns: Once bytecode is deployed to an EVM address, it cannot be edited. Security fixes require pre-planned proxy patterns (e.g., UUPS or Transparent Upgradeable Proxies) governed by multi-signature wallets or timelock smart contracts.
Web3 security specialists must master the specific vulnerability classes that plague smart contracts across Ethereum, Layer 2 rollups, and alternative chains.
Reentrancy occurs when an external call transfers control flow to an untrusted contract before state variable updates are completed in the caller contract.
// VULNERABLE CONTRACT - Classic Reentrancy
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

contract VulnerableVault {
    mapping(address => uint256) public userBalances;

    function withdraw() external {
        uint256 balance = userBalances[msg.sender];
        require(balance > 0, "Insufficient balance");

/ UNTRUSTED CALL BEFORE STATE UPDATE
        (bool success, ) = msg.sender.call{value: balance}("");
        require(success, "Transfer failed");

/ State update happens after call - Vulnerable to reentrancy!
        userBalances[msg.sender] = 0;
    }
}
// SECURE CONTRACT - Checks-Effects-Interactions (CEI) & ReentrancyGuard
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import "@openzeppelin/contracts/utils/ReentrancyGuard.sol";

contract SecureVault is ReentrancyGuard {
    mapping(address => uint256) public userBalances;

    function withdraw() external nonReentrant {
/ 1. CHECKS
        uint256 balance = userBalances[msg.sender];
        require(balance > 0, "Insufficient balance");

/ 2. EFFECTS (State updated BEFORE external call)
        userBalances[msg.sender] = 0;

/ 3. INTERACTIONS (External transfer executed last)
        (bool success, ) = msg.sender.call{value: balance}("");
        require(success, "Transfer failed");
    }
}
DeFi protocols that rely on spot AMM reserve ratios (e.g., querying getReserves() on a Uniswap V2 pair) as their price oracle are vulnerable to flash-loan price manipulation.
[Attacker] ──► (1. Flash Loan $50M) ──► [AAVE Pool]
    │
    ├─────────► (2. Dump USDC) ─────────► [Uniswap AMM Pool] (Price Manipulated)
    │
    ├─────────► (3. Borrow Assets) ──────► [Victim Lending Protocol]
    │
    └─────────► (4. Repay Loan) ────────► [AAVE Pool] (All in 1 Transaction)
Protocols must use Time-Weighted Average Price (TWAP) oracles (such as Uniswap V3 TWAP) or decentralized off-chain oracle networks with cryptographic signatures and circuit breakers (such as Chainlink or Pyth Network).
In addition to classic reentrancy, security specialists must audit complex EVM mathematical rounding errors and read-only reentrancy vulnerabilities.
Solidity does not support floating-point arithmetic. All mathematical calculations execute using integer division, which truncates fractional remainders toward zero.
// VULNERABLE CODE - Precision loss due to division before multiplication
function calculateReward(uint256 amount, uint256 rate, uint256 denominator) public pure returns (uint256) {
/ Rounding to zero occurs during amount / denominator step!
    return (amount / denominator) * rate;
}

// SECURE CODE - Multiplication performed before division
function calculateRewardSecure(uint256 amount, uint256 rate, uint256 denominator) public pure returns (uint256) {
    return (amount * rate) / denominator;
}
Read-only reentrancy occurs when a target protocol (such as a lending market) queries another protocol's getter function (such as getVirtualPrice() on Curve) during an active callback function before state balance has settled. Even if state-mutating functions are protected by reentrancy guards, external getter functions remain readable, allowing attackers to manipulate collateral calculations.
Cryptographic signatures (ECDSA) form the security basis for Web3 authorization, meta-transactions (EIP-712), and permit approvals (ERC-2612). Improper signature verification creates severe vulnerability risks.
block.chainid, a valid signature captured on Ethereum Mainnet can be replayed by an attacker on Arbitrum or Polygon to authorize unauthorized withdrawals.ECDSA.sol enforces $s \le \text{secp256k1n} / 2$ to eliminate malleability vectors.// SECURE EIP-712 SIGNATURE VERIFICATION
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;
import "@openzeppelin/contracts/utils/cryptography/ECDSA.sol";
import "@openzeppelin/contracts/utils/cryptography/EIP712.sol";
contract SecureMetaTransaction is EIP712 {
using ECDSA for bytes32;
bytes32 private constant EXECUTE_TYPEHASH = keccak256("Execute(address sender,uint256 amount,uint256 nonce)");
mapping(address => uint256) public nonces;
constructor() EIP712("SecureApp", "1.0.0") {}
function executeWithSignature(
address sender,
uint256 amount,
bytes calldata signature
) external {
bytes32 structHash = keccak256(abi.encode(EXECUTE_TYPEHASH, sender, amount, nonces[sender]++));
bytes32 digest = _hashTypedDataV4(structHash);
address signer = digest.recover(signature);
require(signer == sender, "Invalid signature");
/ Execute authorized logic securely
}
}
Upgradeable proxy patterns (ERC-1967, UUPS, Transparent Proxies) introduce storage collision and uninitialized logic contract risks.
In UUPS proxies, the implementation contract is deployed separately from the ERC-1967 proxy instance. If the constructor or initialize() function on the logic contract itself is left uninitialized, an attacker can call initialize(), take ownership of the implementation contract, and invoke upgradeToAndCall() pointing to a malicious contract containing selfdestruct.
When upgrading proxy implementation contracts, declaring new state variables out of order corrupts the proxy's storage layout, overwriting administrative slots or user balances.
Smart contract functions can be rendered permanently unusable through unexpected reverts or gas exhaustion attack vectors.
// VULNERABLE CODE - Push payment pattern vulnerable to DoS
function payoutUnsafe(address[] memory recipients) public {
    for (uint256 i = 0; i < recipients.length; i++) {
/ If recipients[i] reverts, ENTIRE transaction fails!
        payable(recipients[i]).transfer(1 ether);
    }
}

// SECURE CODE - Pull payment pattern (Users claim individually)
mapping(address => uint256) public pendingWithdrawals;

function claimPayout() public {
    uint256 amount = pendingWithdrawals[msg.sender];
    require(amount > 0, "No pending withdrawal");

    pendingWithdrawals[msg.sender] = 0;
    (bool success, ) = msg.sender.call{value: amount}("");
    require(success, "Transfer failed");
}
Smart contract security specialists must also audit the Web2 components that interface with smart contracts. Many major Web3 hacks (such as the Ledger Connect Kit exploit and BadgerDAO DNS hijacking) occurred at the Web2 infrastructure layer rather than on-chain bytecode:
window.ethereum) to replace recipient addresses during transaction signing.permit() messages or unrestricted ERC-721 setApprovalForAll() transactions.Web2 security specialists bring strong skills in tools like Burp Suite, Nmap, and Wireshark. In Web3, security engineering relies on specialized EVM static analyzers, property-based fuzzers, and formal verification engines.
┌─────────────────────────────────────────────────────────────────┐
│                    WEB3 AUDITING TOOLSTACK                      │
└────────────────────────────────┬────────────────────────────────┘
                                 │
         ┌───────────────────────┼───────────────────────┐
         ▼                       ▼                       ▼
┌─────────────────┐     ┌─────────────────┐     ┌─────────────────┐
│ Static Analyzers│     │ Property Fuzzers│     │ Formal Verifiers│
│ Slither / Mythril│    │ Foundry/Echidna │     │ Certora Prover  │
└─────────────────┘     └─────────────────┘     └─────────────────┘
Slither is an open-source Solidity static analysis framework written in Python. It converts Solidity AST (Abstract Syntax Tree) into an Intermediate Representation (SlithIR) to detect common vulnerabilities:
# Run Slither audit on a project target directory
slither . --detect reentrancy-eth,uninitialized-state,arbitrary-send-eth
Invariant fuzzing tests contract state boundaries by generating hundreds of thousands of random transaction sequences to see if system invariants hold.
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import "forge-std/Test.sol";
import "../src/ProtocolVault.sol";

contract VaultInvariantTest is Test {
    ProtocolVault vault;

    function setUp() public {
        vault = new ProtocolVault();
    }

// Invariant: Total vault token balance must ALWAYS be >= sum of total shares minted
    function invariant_VaultSolvencyMustHold() public view {
        assertGe(
            vault.totalAssets(),
            vault.totalSupply(),
            "INVARIANT VIOLATION: Vault is insolvent!"
        );
    }
}
When conducting professional smart contract security reviews, security auditors follow a structured multi-stage testing methodology.
                            AUDIT METHODOLOGY WORKFLOW

 [1. Architecture Review] ──► (Read Spec, Map System Boundary & Roles)
           │
           ▼
 [2. Automated Scanning]  ──► (Run Slither, Semgrep, Static Checkers)
           │
           ▼
 [3. Manual Code Audit]   ──► (Trace Business Logic, State Transitions)
           │
           ▼
 [4. Invariant Fuzzing]   ──► (Write Foundry/Echidna Invariant Tests)
           │
           ▼
 [5. Remediation Verification] (Verify Fixes & Issue Final Report)
Before looking at code line-by-line, the auditor maps out the target protocol:
Auditors trace data flow and state mutations across every function:
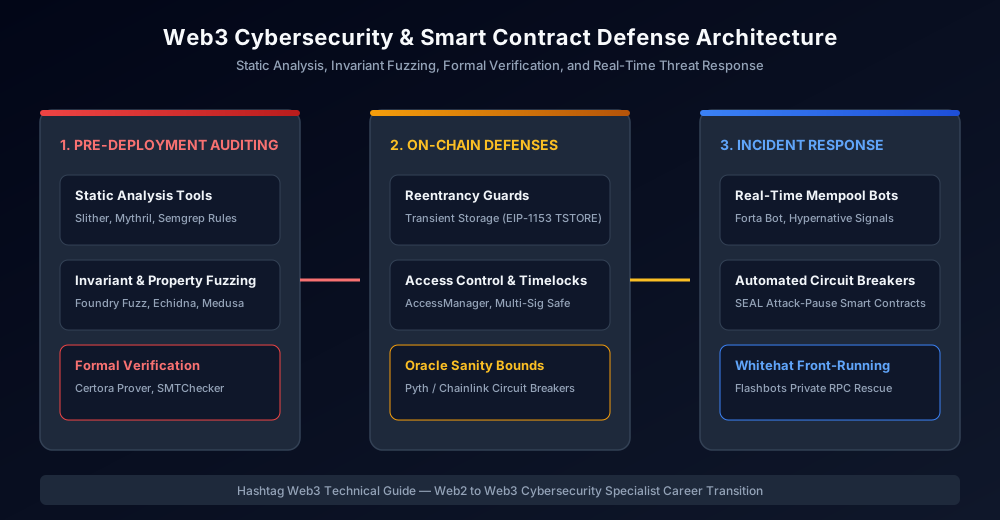
Web3 security extends beyond pre-deployment audits. Modern Web3 security engineers manage real-time monitoring and threat response infrastructure.
Cross-chain bridges are among the most exploited components in Web3 (accounting for over $2 billion in historical losses across the Axie Ronin, Wormhole, and Nomad bridge hacks).
ecrecover returning address(0)).initialize() and call selfdestruct.Web2 security professionals can execute this 90-day roadmap to transition into Web3 cybersecurity:
forge test, cast).Smart contract security professionals operate across several specialized career paths:
| Career Role | Focus Area | Key Tooling / Requirements |
|---|---|---|
| Smart Contract Auditor | Independent pre-deployment security reviews | Slither, Foundry, Invariant Fuzzing |
| Protocol Security Engineer | In-house smart contract hardening & SecOps | Solidity, Timelocks, Safe, Forta Bots |
| Bug Bounty Hunter | Flaw discovery in live mainnet protocols | Reverse engineering EVM bytecode, Flashbots |
| Formal Verification Specialist | Mathematical proof of contract properties | Certora Prover, CVL, Z3 SMT Solvers |
Transitioning from Web2 to Web3 cybersecurity requires shifting from perimeter defense to open, immutable code auditing. By combining Web2 security fundamentals with EVM execution knowledge, static analysis, property-based fuzzing, and real-time monitoring, security specialists play an essential role in safeguarding decentralized protocols.
With financial assets directly controlled by smart contracts, skilled Web3 security engineers will remain among the most valued professionals in the blockchain ecosystem.
Explore more guides and career playbooks