Loading article...

Bitcoin Core published advisories for two medium-severity flaws and a high-severity bug that could halt a mining node's block production, all fixed in releases from October 2025.
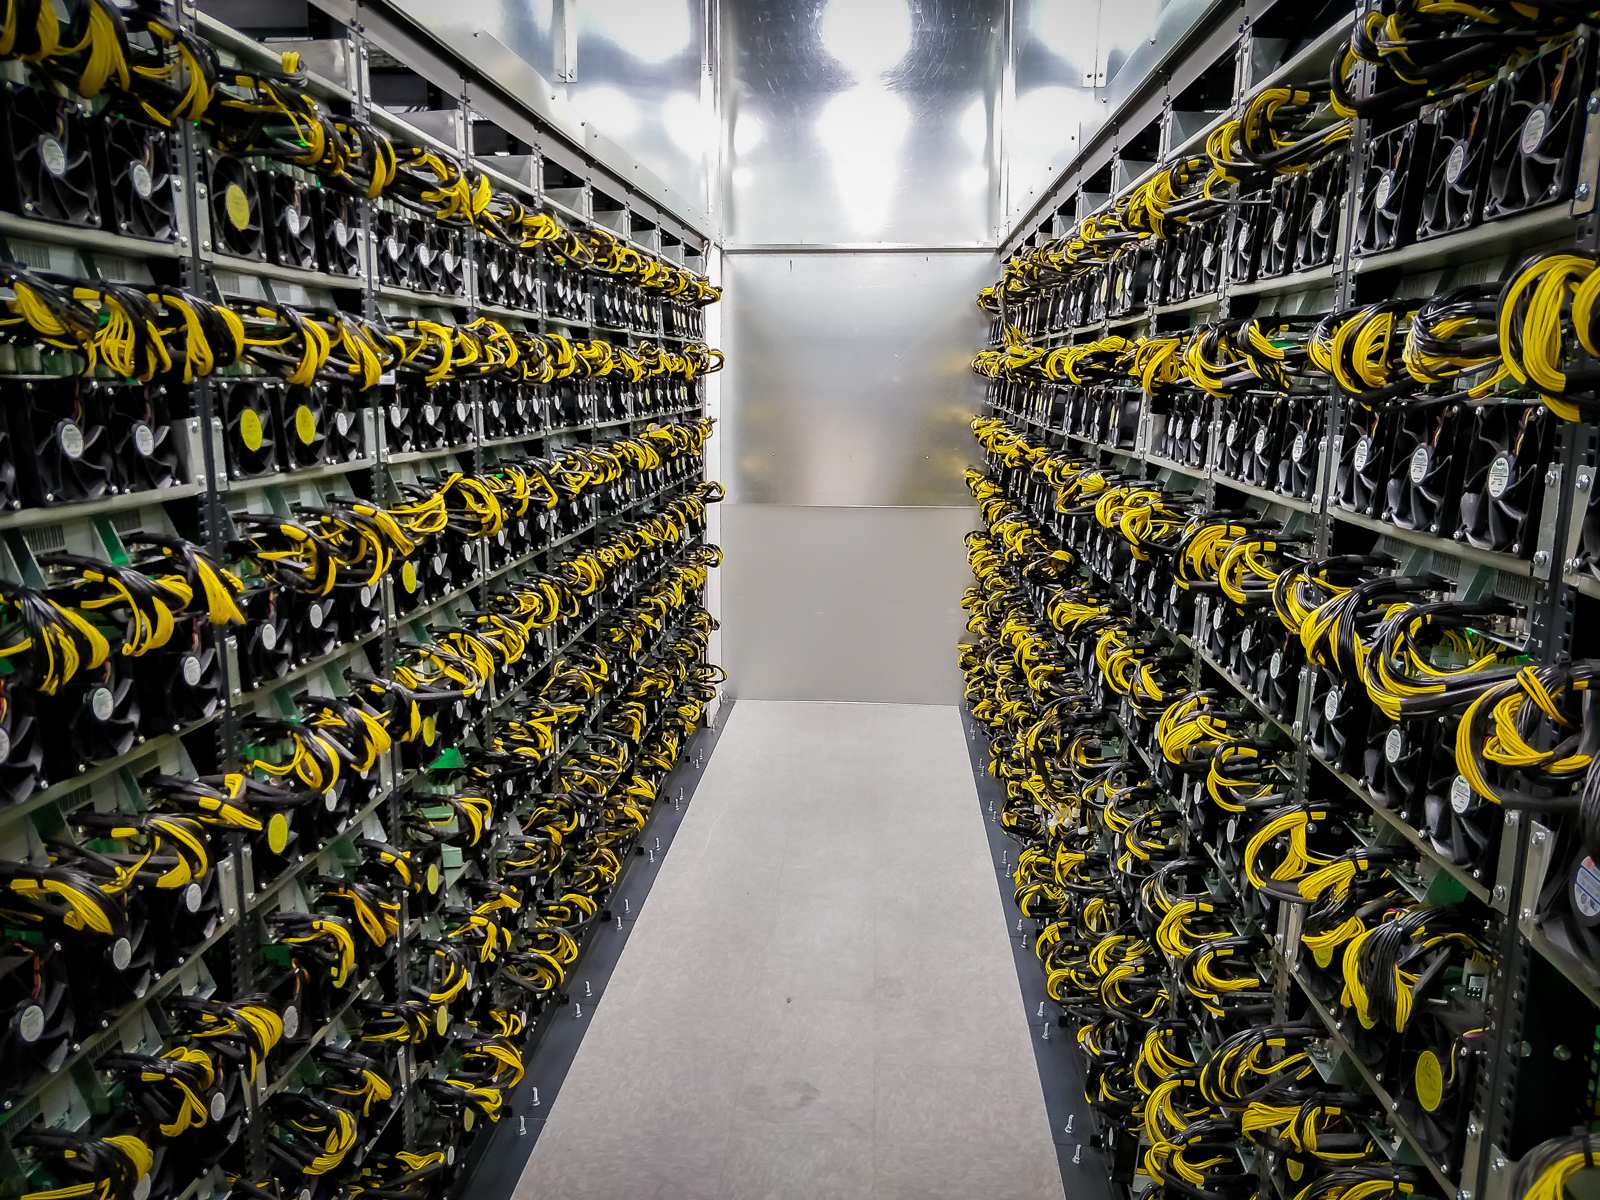
The Argo Blockchain Mirabel mining facility in Quebec. Photo: MikeBogosian via Wikimedia Commons (CC BY-SA 4.0). Source
Bitcoin Core published security advisories on Nov. 10 for three bugs in the software that runs most of the network's nodes, including one high-severity flaw that could stop a mining node from producing blocks. The fixes shipped more than a year earlier, and the project held the details back until its last vulnerable release line reached end of life, Unchained reported.
The high-severity entry, CVE-2025-62861, sits in the mempool, the pool of unconfirmed transactions each node keeps. Bitcoin Core 28.0 added a sibling eviction rule for version 3 transactions, a type BIP 431 limits to one unconfirmed ancestor and one unconfirmed descendant. When a new arrival would give a version 3 parent a second child, the software treats the existing child as a replacement candidate and evicts it if the newcomer pays enough. During a chain reorganization that rule could run while disconnected blocks were being restored with limits bypassed, removing a restored transaction while keeping the transactions that spend it. The miner's block template then failed validation, so the node could not produce blocks until it was restarted, the advisory summary says, with the trade coverage describing the same sequence. Versions 28.0 through 28.2 and 29.0 through 29.1 were affected.
Niklas Goegge reported the bug to the Bitcoin Core security mailing list on Sept. 26, 2025, and Greg Sanders opened pull request #33504 three days later. The fix merged into the project's master branch on Oct. 2, 2025 and was backported to the 30.x, 29.x and 28.x lines over the following five days, the advisory timeline shows.
A second flaw, CVE-2025-62859, let a malicious peer stall a node's block processing by announcing a compact block with a manipulated witness. Affected versions cleared the download state for a reconstructed compact block before checking for that witness malleation, so a failed check sent the node back to the same peer for the full block with a 10-minute timeout. An attacker who got the compact block in first could repeat the stall indefinitely if they controlled the victim's three high-bandwidth peers or the victim ran with the blocksonly option, the advisory says. Eugene Siegel reported the issue on April 28, 2025, and the fix in pull request #32646 merged on June 30, 2025 before a backport to the 29.x line in September.
The third bug, CVE-2025-62860, concerned the optional whitelist setting that relaxes denial-of-service limits and privacy protections for trusted peers. Inbound Tor connections carry the local Tor daemon's address, so whitelisting a range covering that daemon gave every Tor peer the same permissions. Bundled setups led to "thousands of reachable mainnet nodes whitelisting all incoming Tor connections," the project said, adding that popular vendors shipped Bitcoin Core with a Tor daemon and a matching whitelist range, and that client software running alongside a Tor daemon commonly required the option. Nodes that never set it were never affected, and from version 30.0 inbound connections received on an onion bind are never whitelisted. Martin Zumsande and Antoine Poinsot reported the flaw on Sept. 12, 2025; Zumsande's pull request #33395 merged five days later, and Poinsot alerted Bitcoin Knots maintainer Luke Dashjr the same day and several affected software providers two days after that.
All three fixes landed in Bitcoin Core 30.0 on Oct. 10, 2025, in 29.2 four days later and in 28.3 on Oct. 17, so 29.2 and 30.0 are the first releases fixing all three, the timelines show. None of the three reached the "critical" tier Bitcoin Core reserves for coin theft, unauthorized coin creation or permanent chain splits, and the developers found no evidence the flaws were exploited, Decrypt reported; the flaws span denial-of-service and privacy issues rather than anything letting an attacker steal coins or forge Bitcoin, and the project's four severity tiers place them in the middle of that range.
Disclosure waited on the release calendar rather than a fresh fix. The write-ups came after the 29.x line reached end of life on Oct. 27, 2026, leaving 396 days between the releases and the public advisories, Unchained calculated. The advisories do not say whether any of the bugs was exploited in the wild.
The disclosures are separate from three AI-found bugs Bitcoin Core released without its usual embargo on Oct. 28, and node operators are generally urged to run the latest software to stay protected, Decrypt noted. That round's release notes said three more bugs fixed in 30.0 were due two weeks later, Unchained reported. Bitcoin Core had also rewritten its security policy to add a category for "easily discoverable" vulnerabilities that a simple AI prompt can surface, which the project patches and discloses immediately rather than holding under a long embargo.