Building Career Paths for Web3 Privacy Engineers
A comprehensive career roadmap for Web3 privacy engineers, detailing zero-knowledge circuit development, transport-layer anonymity, programmable compliance, compensation bands, and portfolio architectures.
Building Career Paths for Web3 Privacy Engineers
As decentralized ledgers transition from speculative trading platforms into global institutional settlement layers, the industry faces an architectural paradox: radical transparency guarantees verifiable auditability, but completely destroys commercial confidentiality and user autonomy. Transparent blockchains such as the Ethereum Foundation execution layer and the Bitcoin Network broadcast every financial balance, smart contract parameter, corporate payroll distribution, and trading execution to the entire world.
This radical visibility has enabled predatory Maximal Extractable Value (MEV) arbitrageurs to siphon billions from ordinary users while preventing multinational corporations, healthcare entities, and traditional finance institutions from running balance-sheet operations on public chains. Resolving this structural tension has driven an explosion in demand for a new technical discipline: the Web3 Privacy Engineer.
Unlike traditional Web2 privacy engineers who focus on regulatory data governance frameworks such as GDPR compliance, user consent popups, and database access control lists, Web3 privacy engineers build mathematical and cryptographic rails. They design zero-knowledge circuits, confidential state execution machines, anonymous network transports, and programmable compliance layers. This technical roadmap provides an empirical guide to mastering the engineering competencies, architectural pillars, compensation bands, and portfolio requirements necessary to build an elite career in Web3 privacy engineering.
The Four Architectural Pillars of Web3 Privacy
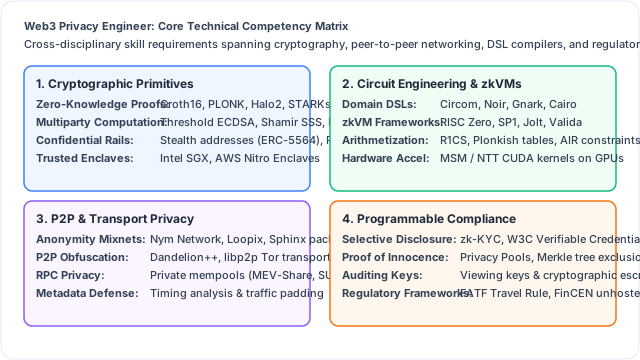
To operate effectively at protocol scale, a Web3 privacy engineer must master four interconnected architectural pillars spanning abstract algebra, circuit compilers, peer-to-peer transport obfuscation, and zero-knowledge compliance rails.
Pillar 1: Cryptographic Primitives and Confidential State
The bedrock of Web3 privacy engineering resides in applied cryptography. Engineers must understand how to construct mathematical systems that verify computations without revealing underlying secrets:
- Zero-Knowledge Proofs (ZKPs): Designing non-interactive zero-knowledge arguments (NIZKs). Engineers must differentiate between pairing-friendly systems like Groth16 and PLONK requiring structured reference strings, transparent hash-based systems like zk-STARKs, and discrete-log systems like Bulletproofs.
- Stealth Addresses: Implementing non-interactive stealth address schemes, specifically the EIP-5564 Standard and EIP-6538 Stealth Meta-Address Registry. These protocols allow recipients to publish a single public identifier while senders generate unique, mathematically unlinkable, one-time destination addresses on-chain using Diffie-Hellman key exchanges over curves such as
secp256k1. - Ring Signatures and Confidential Transactions: Understanding UTXO obfuscation techniques pioneered by Monero Project via Ring Confidential Transactions (RingCT) and Pedersen commitments, ensuring that input ownership and transferred quantities remain hidden in mathematical anonymity sets.
- Secure Multi-Party Computation (MPC): Constructing threshold signature schemes (TSS) utilizing protocols such as FROST (Flexible Round-Optimized Schnorr Threshold) documented by Chelsea Komlo and Ian Goldberg and threshold ECDSA algorithms analyzed across the IACR Cryptology ePrint Archive.
Pillar 2: Circuit Engineering, Compilers, and zkVMs
Writing privacy-preserving smart contracts requires compiling business logic into arithmetic circuits evaluated over finite fields. Modern privacy engineers work across two primary compilation models:
1. Domain-Specific Circuit Languages
For high-performance applications where proof size and constraint counts must be minimized, engineers write custom arithmetic circuits:
- Circom: Maintained by iden3, Circom compiles Rank-1 Constraint Systems (R1CS) for integration with SnarkJS. It is widely utilized in identity circuits such as Semaphore and privacy protocols like Tornado Cash.
- Noir: Developed by Aztec Network, Noir is a Rust-inspired domain-specific language designed specifically for confidential smart contracts. It abstracts algebraic constraint generation while compiling down to an intermediate representation (ACIR) compatible with multiple proving backends, including Barretenberg.
- Gnark: Engineered by Consensys Software, Gnark is a high-performance Go framework providing expressive primitives for constructing Plonk and Groth16 circuits with native zero-knowledge testing harnesses.
2. General-Purpose zkVM Frameworks
Rather than writing hand-crafted arithmetic constraints, the industry is rapidly adopting zero-knowledge virtual machines (zkVMs) that execute compiled standard binaries:
- RISC Zero: Utilizing a STARK-based arithmetization, RISC Zero executes standard RISC-V 32IM target binaries compiled directly from Rust or C++, allowing engineers to embed complex cryptographic routines without manual circuit wiring.
- Succinct SP1: Open-sourced by Succinct Labs, SP1 provides a performant 100% RISC-V zkVM with specialized precompiled coprocessors for sha256, keccak256, and ed25519 arithmetic, enabling light-client proofs and cross-chain messaging.
- Jolt: Conceived by Justin Thaler and collaborators, Jolt pioneers lookup-argument-driven execution, drastically simplifying the mathematical auditability of virtual machine state transitions.
// Example Noir Circuit: Verifying accredited investor status without revealing salary
use dep::std;

fn main(
    salary: Field,              // Private witness input
    threshold: pub Field,       // Public input parameter
    signature: [u8; 64],        // Private signature from financial auditor
    auditor_pubkey: pub [u8; 32]// Public key of auditor
) {
/ 1. Verify salary meets regulatory threshold blindly
    assert(salary as u64 >= threshold as u64);

/ 2. Compute cryptographic commitment to prevent replay
    let salary_hash = std::hash::pedersen_hash([salary]);

/ 3. Verify digital signature from certified auditor over the commitment
    let is_valid = std::ecdsa_secp256k1::verify_signature(
        auditor_pubkey,
        signature,
        salary_hash
    );
    assert(is_valid);
}
Pillar 3: Peer-to-Peer and Transport-Layer Anonymity
A protocol can implement flawless on-chain zero-knowledge circuits, but if a user broadcasts the transaction via an unshielded RPC provider or standard P2P gossip network, network surveillance nodes can link the transaction hash directly to the user IP address and physical location.
Web3 privacy engineers must design defenses across the network transport layer:
- Decentralized Mixnets: Built by Nym Technologies, mixnets encrypt packets into layered Sphinx envelopes. Packets traverse multiple decentralized mix nodes that scramble packet ordering and inject Poisson-distributed timing delays, rendering automated traffic correlation and metadata analysis mathematically infeasible.
- Dandelion++ Routing: Analyzed by Giulia Fanti et al. at Carnegie Mellon University, Dandelion++ splits transaction broadcasting into an anonymizing "stem" phase (hopping anonymously across sequential nodes) followed by a "fluff" broadcast phase, decoupling the originating IP address from the transaction payload.
- Private Mempools and RPC Rails: Implementing MEV-protected private transaction submission pipelines using tools from Flashbots Protect and encrypted order flow networks like SUAVE.
Pillar 4: Programmable Compliance and Selective Disclosure
Historically, crypto privacy protocols operated as blunt, binary instruments: transactions were either completely transparent or entirely opaque. This binary architecture created severe regulatory friction, culminating in global enforcement sanctions against mixer protocols by the U.S. Treasury Office of Foreign Assets Control (OFAC) and international directives formulated by the Financial Action Task Force (FATF).
Modern Web3 privacy engineers design programmable compliance architectures that reconcile user confidentiality with regulatory oversight:
- Privacy Pools: Formalized in research co-authored by Vitalik Buterin, Ameen Soleimani, Jacob Illum, Matthias Nadler, and Fabian Schar in 2023, Privacy Pools allow depositors to generate zero-knowledge exclusion proofs. A user proves they are withdrawing funds from an anonymity set that contains zero deposits originating from sanctioned, illicit, or hacker-associated addresses, without revealing their specific deposit transaction.
- Selective Viewing Keys: Implementing cryptographic viewing keys that permit users to voluntarily disclose decrypted transactional histories, counterparties, and balances to tax authorities, financial auditors, or legal institutions without exposing that data to the public internet.
- W3C Verifiable Credentials and zk-KYC: Integrating zero-knowledge identity rails using standards established by the World Wide Web Consortium (W3C). Protocols like Privado ID (formerly Polygon ID) and World Network permit individuals to prove citizenship, age of majority, or regulatory accreditation without exposing national identity documents.
Career Stages, Progression Tiers, and Compensation
The shortage of engineers proficient in both low-level cryptography and production smart contract architecture has driven Web3 privacy compensation to the upper tier of software engineering globally.
Level 1: Junior Circuit Engineer
- Experience: 0 to 2 years in Web3, or transitioning from traditional backend / cryptography academia.
- Scope: Writing arithmetic circuits in Circom or Noir for standardized components: Merkle tree inclusion proofs, hash pre-image validations (Poseidon, MiMC), and digital signature verifications.
- Target Employers: Specialized ZK rollups, privacy dApps, identity infrastructure providers.
Level 2: Privacy Systems Engineer
- Experience: 2 to 5 years in distributed systems and applied cryptography.
- Scope: Architecting end-to-end confidential systems. Responsibilities include integrating zkVM pipelines (RISC Zero / SP1), managing on-chain EVM verification contracts, optimizing circuit constraint counts, and developing client-side proving architectures using WebAssembly (Wasm) or WebGPU.
- Target Employers: Layer 2 rollups like Scroll, zkSync Era, StarkWare, and confidential networks like Railgun Project.
Level 3: Principal Privacy Architect
- Experience: 5+ years of cryptographic engineering leadership.
- Scope: Designing novel cryptographic mechanisms, authoring protocol whitepapers, selecting polynomial commitment schemes (KZG vs FRI), architecting threshold decryption validator networks, and ensuring post-quantum cryptographic migration roadmaps.
- Target Employers: Core protocol foundations, tier-1 venture research labs such as Paradigm Research and a16z crypto, and confidential execution layers like Zama Cryptography and Fhenix.
Specialized Track: Cryptographic Security Auditor
- Focus: Reviewing zero-knowledge circuits and confidential protocols for subtle mathematical bugs, including underconstrained signals, unconstrained arithmetic loops, shadow variables, and side-channel leakage.
- Firms: Leading security auditor organizations including OpenZeppelin, Trail of Bits, Veridise, and Consensys Diligence.
- Incentive Model: Auditors frequently combine high base retainers with competitive bug bounty payouts on platforms like Immunefi, where critical zero-knowledge vulnerabilities routinely command multi-million-dollar bounties.
Building a Production-Grade Portfolio
Recruiters and engineering directors in Web3 privacy prioritize verifiable open-source code over formal educational credentials. A winning portfolio demonstrates the ability to solve concrete cryptographic challenges:
Critical Security Concept: Finding Underconstrained Circuits
The single most destructive vulnerability class in zero-knowledge circuit engineering is the underconstrained bug.
In conventional programming, a developer writes imperative code that assigns values. In circuit programming, an engineer defines declarative mathematical relations. If a variable is assigned a value in the witness generator but is not mathematically constrained in the circuit equation, an attacker can submit an arbitrary forged value that satisfies the algebraic constraints, allowing unauthorized withdrawals.
// DANGEROUS: Underconstrained Circuit Vulnerability
template BrokenMultiplier() {
    signal input a;
    signal input b;
    signal output c;

/ Assignment without constraint: the prover calculates c,
/ but no constraint equation enforces that c === a * b!
    c <-- a * b;

/ An attacker can forge c = 999999999 without satisfying the multiplication!
}

// CORRECT: Fully Constrained Circuit
template SecureMultiplier() {
    signal input a;
    signal input b;
    signal output c;

/ Both assigns the witness AND generates the R1CS constraint: c === a * b
    c <== a * b;
}
Demonstrating familiarity with formal verification tools such as Ecne and Veridise Picus immediately distinguishes an engineer during technical screenings.
Essential Developer Tooling and Educational Resources
Aspiring Web3 privacy engineers should master the following foundational frameworks, academic hubs, and developer communities:
Authoritative Reading and Academic Hubs
- ZKProof Community Standards: An international academic and industrial initiative standardizing zero-knowledge proof verification algorithms and security definitions.
- 0xPARC Foundation: Applied research organization advancing programmable cryptography, homomorphic encryption, and recursive SNARK architectures.
- Privacy and Scaling Explorations (PSE): An applied research division supported by the Ethereum Foundation, developing open-source cryptographic primitives including Semaphore, MACI (Minimal Anti-Collusion Infrastructure), and blind signatures.
- IACR (International Association for Cryptologic Research): The premier global scientific association organizing Eurocrypt, Crypto, and Asiacrypt, hosting the latest research on polynomial commitments and post-quantum cryptography.
- Coin Center and the Electronic Frontier Foundation (EFF): Essential policy research organizations defending the constitutional right to publish privacy-preserving code and mathematical software.
The Future Landscape of Privacy Engineering
The coming decade will see privacy engineering evolve from an optional protocol feature into an essential prerequisite for decentralized infrastructure:
- ZK and FHE Convergence: Hybrid architectures will pair zero-knowledge proofs for client-side validity verification with Fully Homomorphic Encryption for shared-state smart contract execution, powered by systems like Zama fhEVM and Fhenix.
- Hardware Acceleration Parity: As dedicated ASIC coprocessors manufactured by Cysic and Ingonyama enter production data centers, proof generation latency will shrink toward real-time transaction broadcast speeds.
- Institutional Confidential Settlement: Regulatory clarity under frameworks such as European MiCA and compliant selective disclosure standards will trigger massive capital deployments by institutional custodians like Coinbase Institutional and decentralized asset managers.
Engineers who master the intersection of applied abstract algebra, circuit compilers, transport-layer anonymity, and programmable compliance will lead the architectural evolution of the decentralized internet.