
Cryptocurrency Token Burning
A comprehensive technical and financial analysis of token burning mechanisms in blockchain protocols, covering cryptographic provability, economic supply dynamics, governance models, tax implications, and smart contract implementations.
In tokenomics and decentralized protocol design, token burning serves as a foundational economic mechanism for supply control, value accrual, and cryptographic proof of resource expenditure. By permanently removing digital assets from circulating supply, token burns attempt to mimic equity buyback programs, offset inflationary emissions, enforce deflationary monetary dynamics, or implement consensus mechanisms like Proof of Burn.
Understanding token burning requires an analysis of smart contract engineering, cryptographic verifiability, economic equilibrium modeling, regulatory implications, and governance risks. This technical guide examines how token burns operate across major L1 networks, L2 rollups, and decentralized applications.
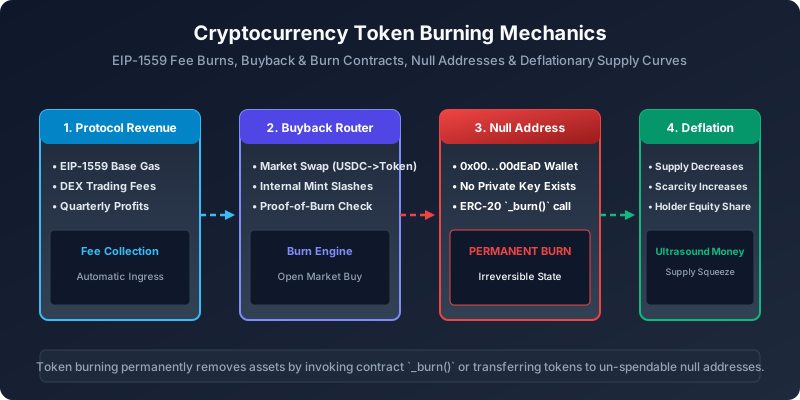
Cryptographic and Technical Mechanics of Token Burning
At a fundamental technical level, tokens residing on a blockchain cannot simply be deleted from existence. Blockchain state machines maintain an immutable ledger of transfers and account balances. Therefore, burning a token is defined as transferring a digital asset to a cryptographic location where retrieval is mathematically impossible.
Null Addresses and Unspendable Keys
The primary technique for burning tokens involves transferring them to a designated null address or unspendable account key. A null address is a public address for which no corresponding private key exists or could ever be feasibly calculated given current cryptographic standards.
-
The Ethereum Zero Address (
0x0000000000000000000000000000000000000000): The most common burn target on EVM-compatible chains is the zero address. Because the probability of deriving a private key corresponding to0x0via elliptic curve cryptography (secp256k1) is effectively zero ($1 \text{ in } 2^{160}$), any tokens transferred to this address are permanently locked out of circulation. -
Eater Addresses and Vanity Dead Addresses: Protocols frequently utilize custom unspendable addresses such as
0x000000000000000000000000000000000000dEaD(often called thedEaDaddress). These addresses are derived by concatenating recognizable hex strings. Because the private key derivation path for an arbitrary 160-bit hex string is computationally infeasible, tokens sent to0x...dEaDare verifiably unspendable. -
Bitcoin Proof-of-Burn (
OP_RETURN): In the Bitcoin network, burning non-native tokens or committing data via Proof of Burn relies on theOP_RETURNscript opcode. An output marked withOP_RETURNis declared provably unspendable by protocol consensus rules. Nodes instantly removeOP_RETURNoutputs from the active UTXO (Unspent Transaction Output) set, keeping the ledger state trim while confirming that the associated satoshis cannot be spent.
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import "@openzeppelin/contracts/token/ERC20/ERC20.sol";
import "@openzeppelin/contracts/access/Ownable.sol";

contract VerifiableBurnToken is ERC20, Ownable {
    address public constant DEAD_ADDRESS = 0x000000000000000000000000000000000000dEaD;

    event TokensBurned(address indexed burner, uint256 amount, string reason);

    constructor(uint256 initialSupply) ERC20("Verifiable Burn Token", "VBT") Ownable(msg.sender) {
        _mint(msg.sender, initialSupply * 10**decimals());
    }

// Direct state reduction burn modifying internal supply state variable
    function burnStateReduction(uint256 amount) external {
        _burn(msg.sender, amount);
        emit TokensBurned(msg.sender, amount, "STATE_REDUCTION");
    }

// Transfer-to-dead-address burn preserving total historical mint metric
    function burnToDeadAddress(uint256 amount) external {
        _transfer(msg.sender, DEAD_ADDRESS, amount);
        emit TokensBurned(msg.sender, amount, "DEAD_ADDRESS_TRANSFER");
    }
}
State Reduction vs. Null Address Transfers
Smart contract developers implement token burning through two distinct architectural paradigms: direct state reduction or null address transfers.
Internal State Reduction (_burn)
Standard token implementations, such as OpenZeppelin's ERC-20 contract, expose an internal _burn(address account, uint256 value) method. This function performs two direct mutations on storage variables:
- Decrements
_balances[account]byvalue. - Decrements
_totalSupplybyvalue. - Emits a standard
Transfer(account, address(0), value)event log.
Direct state reduction is computationally efficient because it reduces storage overhead and directly updates the canonical supply total. When querying totalSupply(), off-chain aggregators like CoinGecko or CoinMarketCap instantly register the supply contraction without requiring custom queries for dead address balances.
Null Address Transfer
Under the null address transfer paradigm, the smart contract does not decrement the _totalSupply state variable. Instead, tokens are transferred via standard ERC-20 transfer(DEAD_ADDRESS, amount) logic.
While the on-chain total supply metric remains unchanged, the circulating supply is calculated off-chain:
$$\text{Circulating Supply} = \text{Total Supply} - \text{Balance}(\text{DEAD_ADDRESS}) - \text{Balance}(\text{ZERO_ADDRESS})$$
Protocols choose null address transfers when using non-upgradable legacy contracts lacking internal burn functions or when preserving absolute historical mint metrics in contract storage is strictly required for programmatic dividend calculations.
Taxonomies of Token Burning Mechanisms
Token burn mechanisms vary in execution timing, trigger events, and underlying economic incentives. Blockchain architects categorize burns into four distinct archetypes.
                  ┌─────────────────────────────────────────┐
                  │       TOKEN BURNING TAXONOMY            │
                  └────────────────────┬────────────────────┘
                                       │
         ┌─────────────────────────────┼─────────────────────────────┐
         ▼                             ▼                             ▼
┌─────────────────┐           ┌─────────────────┐           ┌─────────────────┐
│ Systemic/Base   │           │ Programmatic    │           │ Buyback and     │
│ Protocol Burns  │           │ Transaction Fees│           │ Burn Modules    │
└────────┬────────┘           └────────┬────────┘           └────────┬────────┘
         │                             │                             │
         ▼                             ▼                             ▼
  Ethereum EIP-1559            Solana/BNB Gas              DeFi DEX Fee Split
  Base Fee Destruction         Percentage Destruction      Protocol Revenue Buyback
1. Systemic Base Fee Burning (EIP-1559 Model)
Ethereum's EIP-1559 update restructured transaction fee mechanics by introducing a two-tiered gas fee model consisting of a dynamic baseFee and a priorityFee (tip).
- Base Fee (
baseFee): Mandatory fee per gas unit required for transaction inclusion. ThebaseFeeis algorithmically adjusted block-by-block based on block space demand relative to a target gas limit. - Destruction Logic: The entire
baseFeecollected in ETH is automatically burned by the protocol. It is neither sent to the block proposer (validator) nor redirected to a treasury.
The primary engineering objective of burning the base fee is preventing validator collusion. If block proposers received the base fee, miners could fabricate zero-cost synthetic transactions to artificially inflate the base fee for subsequent blocks, extracting higher fees from users. Burning the base fee aligns validator incentives while linking network usage directly to supply contraction.
2. Programmatic Buyback and Burn
Popularized by centralized exchanges and decentralized protocols (e.g., MakerDAO's MKR Flop/Flap auctions, BNB quarterly burns, and PancakeSwap CAKE burns), buyback-and-burn systems allocate protocol revenue toward purchasing native tokens from open secondary markets and burning them.
Automated Market Maker (AMM) Buyback Engine Mechanics
- Protocol fees accumulate in secondary assets (e.g., USDC, USDT, ETH) within a vault contract.
- An automated keeper contract calls the buyback function once a fee threshold is breached.
- The contract executes an exact-input single-hop or multi-hop swap via an AMM router (e.g., Uniswap V3 pool).
- The acquired native tokens are routed directly to
address(0)or the_burn()function within a single atomic transaction.
[Users/Traders] ──> (Pay Trading Fees in USDC) ──> [Protocol Treasury Vault]
                                                             │
                                                             ▼
                                                    [Keeper Executor]
                                                             │
                                                             ▼
[Native Supply Decreased] <── (Burn Function) <── [AMM Router Swap: USDC -> TOKEN]
3. Proof-of-Burn (PoB) Consensus
Proof of Burn is an alternative consensus mechanism where miners or validators demonstrate network commitment by destroying native assets or coins from a parent blockchain (e.g., burning Bitcoin to bootstrap a layer-2 sidechain token).
In PoB systems, a miner's probability of mining a block and collecting block rewards is proportional to the total value of tokens they have burned relative to network-wide burns over a specific time window:
$$P(\text{Mining Block } i) = \frac{\sum_{t=0}^{T} \text{BurnedTokens}{\text{miner}, t} \cdot e^{-\lambda (T-t)}}{\sum{j=1}^{M} \sum_{t=0}^{T} \text{BurnedTokens}_{j, t} \cdot e^{-\lambda (T-t)}}$$
Where $\lambda$ represents a decay constant ensuring older burns gradually lose weight, forcing miners to continuously expend resources to preserve mining power.
4. Dynamic Algorithmic Supply Burning (Seigniorage & Stablecoins)
Algorithmic stablecoins and dual-token seigniorage protocols (such as Frax Finance, or historically Terra/Luna) enforce price pegs through programmatic mint-and-burn arbitrage loops. When a stablecoin trades below its target peg ($1.00), the protocol incentivizes arbitrageurs to buy the discounted stablecoin on the open market and burn it in exchange for $1.00 worth of volatile governance collateral tokens, thereby contracting stablecoin supply until parity is restored.
Quantitative Economic Impact and Supply Dynamics
Proponents of token burning frequently draw direct comparisons to corporate stock buybacks. While both mechanisms reduce circulating units, the quantitative economic impact depends heavily on market elasticity, demand shifts, liquidity pool depth, and investor expectations.
Quantity Theory of Money and Token Dynamics
The theoretical relationship between token supply contraction and valuation can be analyzed through the Quantity Theory of Money framework:
$$M \cdot V = P \cdot Y$$
Where:
- $M$ = Circulating Token Supply
- $V$ = Velocity of Money (frequency of token turnover per unit time)
- $P$ = Price level of goods/services per token (inverse of token purchasing power)
- $Y$ = Real transaction volume/economic output of the network
Holding economic activity ($Y$) and token velocity ($V$) constant, a reduction in token supply ($M \rightarrow M'$) requires an offsetting increase in token unit value ($P^{-1}$):
$$\Delta P \approx -\frac{\Delta M}{M}$$
However, in real-world crypto-asset markets, velocity ($V$) is non-constant. Token burns often trigger speculative rallies that temporarily increase token velocity, obscuring the long-term deflationary price effect.
Impact of EIP-1559 on Ethereum Monetary Policy
Following Ethereum's EIP-1559 integration and subsequent transition to Proof of Stake (The Merge), Ethereum's net monetary issuance model became dynamic:
$$\text{Net Annual Issuance Rate } (\gamma) = \frac{\text{Validator Rewards Issued} - \text{ETH Base Fee Burned}}{\text{Total ETH Supply}}$$
                      ETHEREUM NET ISSUANCE SPECTRUM

 Low Gas Demand (< 15 gwei)               High Gas Demand (> 25 gwei)
──────────────────────────────────┬───────────────────────────────────►
        NET INFLATIONARY          │          NET DEFLATIONARY
 (Issuance > Base Fee Burn)       │    (Base Fee Burn > Issuance)
                                  │
                          Ultrasound Money
                         Equilibrium Boundary
When gas fees exceed approximately 15 to 25 gwei (depending on total staked ETH), the ETH burn rate surpasses new staking issuance, rendering Ethereum net deflationary ("ultrasound money").
Token Burning Mechanics Across Major Blockchains
| Network / Protocol | Burn Mechanism Type | Primary Asset Burned | Trigger / Cadence | Primary Objective |
|---|---|---|---|---|
| Ethereum | EIP-1559 Base Fee Burn | ETH | Per transaction block | Eliminate MEV/collusion, reduce total supply |
| BNB Chain | Auto-Burn Algorithm + BEP-95 | BNB | Real-time gas + Quarterly auto-burn | Supply contraction down to 100M BNB target |
| Solana | Transaction Fee Burn | SOL | Per transaction (50% of base fee) | Offset inflation rate, penalize spam transactions |
| Shiba Inu (SHIB) | Community & Portal Burn | SHIB | Ad-hoc user & dApp actions | Speculative supply reduction |
| MakerDAO / Sky | Flap Auctions (Surplus Burn) | MKR | When system surplus exceeds target | Accrue protocol revenue to MKR holders |
| PancakeSwap | Automated AMM Revenue Burn | CAKE | Weekly scheduled execution | Counteract high liquidity provider emissions |
Step-by-Step Security and Implementation Analysis
Implementing burn functions in production smart contracts requires strict validation and access control to avoid standard security vulnerabilities.
Vulnerability 1: Unauthorized Public Burn Functions
If a custom token exposes an un-guarded public burn(address account, uint256 amount) method without checking whether msg.sender == account or verifying allowances, malicious actors can invoke the function to destroy tokens belonging to arbitrary wallet addresses.
// VULNERABLE CODE - DO NOT USE IN PRODUCTION
function unsafeBurn(address targetAccount, uint256 amount) external {
/ Missing require(msg.sender == targetAccount) check!
    balances[targetAccount] -= amount;
    totalSupply -= amount;
}
// SECURE IMPLEMENTATION
function safeBurnFrom(address account, uint256 amount) external {
    if (account != msg.sender) {
        uint256 currentAllowance = allowance(account, msg.sender);
        require(currentAllowance >= amount, "ERC20: burn amount exceeds allowance");
        _approve(account, msg.sender, currentAllowance - amount);
    }
    _burn(account, amount);
}
Vulnerability 2: Reentrancy Risks in Buyback Mechanics
Automated buyback-and-burn contracts interacting with decentralized exchanges must manage reentrancy risks, especially when calling untrusted liquidity pools or processing fee-on-transfer tokens.
When executing an AMM swap:
- Deposit input asset to pool.
- Execute swap router.
- Validate received token quantity matches slippage parameters.
- Burn tokens within an isolated non-reentrant execution context.
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import "@openzeppelin/contracts/token/ERC20/IERC20.sol";
import "@openzeppelin/contracts/utils/ReentrancyGuard.sol";

interface ISwapRouter {
    function swapExactTokensForTokens(
        uint amountIn,
        uint amountOutMin,
        address[] calldata path,
        address to,
        uint deadline
    ) external returns (uint[] memory amounts);
}

contract SecureBuybackBurn is ReentrancyGuard {
    ISwapRouter public immutable swapRouter;
    address public immutable nativeToken;
    address public immutable feeToken;
    address public constant DEAD = 0x000000000000000000000000000000000000dEaD;

    constructor(address _router, address _nativeToken, address _feeToken) {
        swapRouter = ISwapRouter(_router);
        nativeToken = _nativeToken;
        feeToken = _feeToken;
    }

    function executeBuybackAndBurn(uint256 feeAmountIn, uint256 minNativeOut) external nonReentrant {
        IERC20(feeToken).transferFrom(msg.sender, address(this), feeAmountIn);
        IERC20(feeToken).approve(address(swapRouter), feeAmountIn);

        address[] memory path = new address[](2);
        path[0] = feeToken;
        path[1] = nativeToken;

/ Route output tokens directly to dead address
        swapRouter.swapExactTokensForTokens(
            feeAmountIn,
            minNativeOut,
            path,
            DEAD,
            block.timestamp + 300
        );
    }
}
Regulatory, Accounting, and Governance Considerations
Token burns carry distinct regulatory, tax, and governance implications across major jurisdictions.
1. SEC and Securities Regulation (Howey Test Analysis)
Under the United States SEC's Howey Test framework, an investment contract exists if there is an investment of money in a common enterprise with an expectation of profits derived primarily from the entrepreneurial or managerial efforts of others.
Protocols using active buyback-and-burn campaigns managed by a centralized team risk triggering the "expectation of profit derived from managerial efforts" prong:
- Centralized Buybacks: If a core executive team manually calculates quarterly profits and executes discretion-based buybacks (similar to traditional stock buybacks), regulators may classify the asset as a security.
- Programmatic Systemic Burns: Protocol-level burns (like EIP-1559 base fee destruction) that execute algorithmically without human intervention present a lower risk of classification as managerial buybacks.
2. Taxation Models for Token Burns
Tax treatment of token burns varies across legal jurisdictions depending on whether the burn is executed by an individual token holder or by the protocol.
- Individual User Burns: When an investor sends tokens to a dead address to reduce supply or claim a utility benefit, tax authorities in several jurisdictions (e.g., IRS in the USA, HMRC in the UK) may treat the transaction as a disposal event. If the cost basis of the burned asset exceeds zero, it may trigger a capital loss or capital gain realization based on the fair market value at the time of disposal.
- Protocol-Level Burns: Programmatic base fee burns do not constitute taxable events for individual holders, though they alter the overall cost-basis tracking for protocols accounting for treasury assets.
Career Opportunities in Tokenomics and Smart Contract Engineering
Designing resilient token burn architectures requires expertise spanning tokenomics design, smart contract auditing, and quantitative DeFi analytics. As Web3 ecosystems grow, specialized roles have emerged focused on protocol sustainability and monetary engineering.
Essential Roles in Protocol Engineering
-
Tokenomics Architect / Quantitative Financial Modeler:
- Responsibilities: Design mathematical issuance curves, simulate EIP-1559 style burn parameters, build CadCAD/Python simulations to model supply contraction under extreme market volatility.
- Required Skills: Applied game theory, Python, differential equations, liquidity pool mechanics, risk modeling.
-
Smart Contract Protocol Engineer:
- Responsibilities: Implement secure ERC-20/ERC-4626 standard burn routines, build automated AMM buyback vaults, write comprehensive Foundry/Hardhat unit and invariant tests.
- Required Skills: Solidity, Yul/Assembly optimization, EVM memory layout, OpenZeppelin primitives, Foundry.
-
DeFi Security Auditor:
- Responsibilities: Inspect burn mechanisms for reentrancy bugs, access control bypasses, and flash-loan-assisted price manipulation vulnerabilities in buyback routers.
- Required Skills: Static analysis tools (Slither, Mythril), symbolic execution, formal verification, EVM execution tracing.
Verification and Testing Frameworks for Burn Functions
When deploying token burn functionality, protocol developers must execute invariant testing to verify that state updates match expected mathematical bounds.
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import "forge-std/Test.sol";
import "../src/VerifiableBurnToken.sol";

contract BurnTokenInvariantTest is Test {
    VerifiableBurnToken token;
    address user = address(0x123);

    function setUp() public {
        token = new VerifiableBurnToken(1_000_000);
        token.transfer(user, 100_000 * 10**18);
    }

// Fuzz test verifying that burning reduces total supply equal to balance reduction
    function testFuzz_BurnStateReduction(uint256 burnAmount) public {
        uint256 userBalance = token.balanceOf(user);
        vm.assume(burnAmount > 0 && burnAmount <= userBalance);

        uint256 supplyBefore = token.totalSupply();

        vm.prank(user);
        token.burnStateReduction(burnAmount);

        uint256 supplyAfter = token.totalSupply();
        uint256 userBalanceAfter = token.balanceOf(user);

        assertEq(supplyBefore - supplyAfter, burnAmount, "Total supply must decrease by exact burn amount");
        assertEq(userBalance - userBalanceAfter, burnAmount, "User balance must decrease by exact burn amount");
    }
}
Summary and Key Takeaways
Token burning is a core design tool in crypto-economic architecture. Whether implemented through Ethereum's EIP-1559 base fee destruction, programmatic DEX buyback engines, or proof-of-burn consensus algorithms, token destruction establishes verifiable supply boundaries across decentralized networks.
Successful protocol implementation requires balancing smart contract security, cryptographic verifiability, market liquidity constraints, and regulatory compliance. As protocol architectures evolve toward modular layer-2 rollups and decentralized infrastructure networks (DePIN), token burn mechanisms will remain essential for driving long-term protocol sustainability and economic alignment.