Loading article...

A technical guide to cryptographic nonces. Compare Proof-of-Work mining nonces used in Nakamoto consensus against EVM account nonces used for transaction ordering and replay attack prevention.
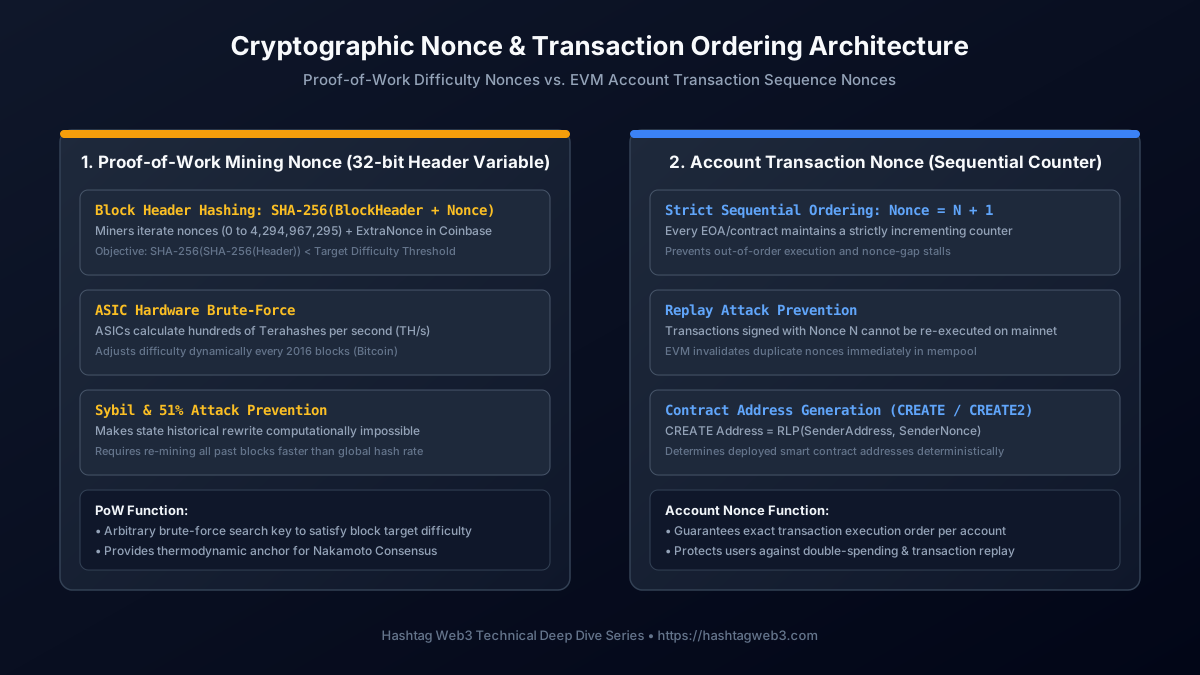
In computer science and cryptography, a nonce is an abbreviation for "number used once." It represents an arbitrary or sequential numerical value included in cryptographic calculations to ensure that identical data payloads yield unique hash outputs and to prevent unauthorized replay attacks across networks.
However, in blockchain software engineering, the term "nonce" refers to two distinct operational primitives depending on the context:
Understanding how both types of nonces function is essential for protocol engineers, security auditors, node operators, and Web3 developers.
In Proof-of-Work (PoW) blockchains like Bitcoin, mining is the mechanism by which decentralized nodes agree on block validity without trusting a central authority. The mining nonce serves as the primary variable enabling this competitive brute-force computation.
To publish a valid block to the Bitcoin network, a miner compiles candidate transactions into a block, constructs a Merkle tree root hash, and builds a 80-byte block header consisting of six parameters:
┌────────────────────────────────────────────────────────────────────────┐
│                   Bitcoin 80-Byte Block Header Structure               │
├──────────────────┬────────────┬────────────────────────────────────────┤
│ Field            │ Size       │ Purpose                                │
├──────────────────┼────────────┼────────────────────────────────────────┤
│ Version          │ 4 bytes    │ Block validation rules version         │
│ Previous Hash    │ 32 bytes   │ SHA-256 hash of the preceding block    │
│ Merkle Root Hash │ 32 bytes   │ Combined hash of all block transactions│
│ Timestamp        │ 4 bytes    │ Current Unix block creation time       │
│ Bits (Target)    │ 4 bytes    │ Encoded mining difficulty threshold    │
│ Nonce            │ 4 bytes    │ Miner-iterated variable (0 - 2^32-1)   │
└──────────────────┴────────────┴────────────────────────────────────────┘
The miner processes this 80-byte header through double SHA-256 hashing:
$$\text{Block Hash} = \text{SHA256}(\text{SHA256}(\text{Block Header}))$$
For the block to be accepted by network nodes, the resulting 256-bit block hash must be mathematically less than or equal to the current target difficulty value defined by the network protocol:
$$\text{Block Hash} \le \text{Target}$$
Because cryptographic hash functions like SHA-256 exhibit the avalanche effect (modifying a single bit in the input produces a completely unpredictable, pseudo-random 256-bit output), miners cannot mathematically predict or solve for a valid hash. The only method is brute-force trial and error: incrementing the Nonce value, re-hashing the header, and checking if the output starts with the required number of leading zeros.
A 32-bit nonce field allows $2^{32}$ (approximately 4.29 billion) unique combinations. Modern ASIC (Application-Specific Integrated Circuit) mining rigs execute hundreds of Terahashes per second (TH/s), meaning a single ASIC exhausts all 4.29 billion nonce values in less than a millisecond.
To continue searching for valid hashes without waiting for block timestamps to change, miners modify an ExtraNonce field located inside the Coinbase transaction (the first transaction in a block paying block rewards). Modifying the Coinbase ExtraNonce changes the Merkle Root Hash in the block header, resetting the 32-bit standard nonce search space and allowing ASICs to iterate billions of hashes continuously.
The computational work required to discover a valid mining nonce fulfills two primary security functions:
While PoW mining nonces are arbitrary numbers iterated for block difficulty, account nonces in the Ethereum Virtual Machine (EVM) serve as sequential counters to enforce transaction ordering and prevent transaction replay.
In Ethereum's account-based model, every address (EOA or Smart Contract) stores an internal state containing four fields:
$$\text{Account State} = { \text{nonce}, \text{balance}, \text{codeHash}, \text{storageRoot} }$$
CREATE opcodes) initiated by that contract.┌────────────────────────────────────────────────────────────────────────┐
│ Account Nonce Sequence Execution Flow │
├────────────────────────────────────────────────────────────────────────┤
│ EOA Current State: Nonce = 5 │
│ │
│ Tx A (Nonce = 5): Transfer 1 ETH ──> [ VALID: Executed in Block N ] │
│ Tx B (Nonce = 5): Transfer 1 ETH ──> [ REJECTED: Duplicate Nonce ] │
│ Tx C (Nonce = 7): Transfer 2 ETH ──> [ STALED: Waiting for Nonce 6 ] │
└────────────────────────────────────────────────────────────────────────┘
When an EOA initiates a transaction, it explicitly includes its current expected nonce in the signed payload. The EVM evaluates account nonces according to strict rules:
Nonce = 5 is executed in a block, the network increments the account's state nonce to 6. If an attacker copies transaction Nonce = 5 and broadcasts it again, network nodes reject it immediately as a duplicate nonce call.Nonce = 5 and Nonce = 7, the transaction with Nonce = 7 cannot execute. It remains in the mempool until a transaction with Nonce = 6 is broadcast and included in a block.When network gas prices surge, a transaction broadcast with a low gas fee can remain stuck in the mempool indefinitely. To cancel or replace a stuck transaction, developers issue a new transaction with the exact same nonce as the stuck transaction, but with a significantly higher gas price (typically at least 10% to 12% higher tip). EVM nodes replace the low-fee transaction in their local mempools with the high-fee transaction, executing the new transaction while invalidating the old payload.
CREATE / CREATE2Account nonces directly determine the cryptographic addresses of deployed smart contracts:
CREATE Opcode: The contract address is derived deterministically from the deployer's address and account nonce:$$\text{Contract Address} = \text{keccak256}(\text{rlp.encode}([\text{deployerAddress}, \text{nonce}]))[12:]$$
CREATE2 Opcode (EIP-1014): CREATE2 bypasses the sender's account nonce entirely, relying instead on a custom salt, deployer address, and init code hash. This enables cross-chain deterministic contract deployments regardless of varying account nonces across chains.Understanding cryptographic nonces, execution memory models, and state synchronization is essential across core software engineering roles:
Interested in building node software, auditing EVM state execution, or engineering high-throughput blockchain infrastructure? Explore active technical positions across protocol development, security, and developer tooling on our curated list of Web3 engineering jobs.
Explore more guides and career playbooks