Loading article...

An empirical technical thesis on DAO treasury architecture, analyzing balance sheet diversification, multi-signature custody, timelock governance controllers, and risk mitigation against hostile takeovers.
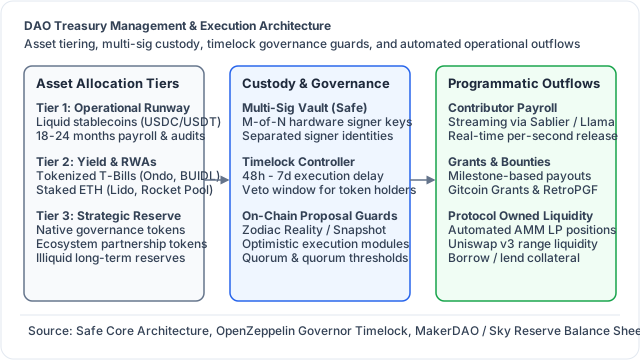
Decentralized Autonomous Organizations (DAOs) represent one of the most significant experiments in decentralized corporate governance and collective capital allocation in modern economic history. Operating across networks like Ethereum Foundation, Arbitrum, and Optimism, decentralized treasuries collectively control billions of dollars in digital assets.
However, managing a decentralized treasury involves fundamentally different engineering, legal, and cryptoeconomic constraints than operating a traditional corporate balance sheet. In traditional enterprise finance, funds reside in regulated commercial banks managed by executive fiduciaries subject to board oversight and company law.
In a DAO, capital is custodied entirely in immutable smart contracts, managed across programmatic multi-signature vaults, and governed through token-weighted on-chain votes. This structure eliminates single points of failure, but introduces severe operational risks: balance sheet volatility, flash loan governance takeovers, and legal liability exposure.
At its foundational level, a DAO treasury is an on-chain repository of digital assets whose movement is programmatically restricted to authorized state transitions.
Unlike a venture capital fund or traditional technology enterprise, a DAO treasury operates with total public transparency:
The most critical operational failure documented across DAO history is the "Native Token Trap."
According to financial analytics compiled on Token Terminal and DeepDAO, over eighty percent of aggregate DAO treasury reserves are denominated in the DAO's own native governance token (such as UNI for Uniswap Labs, ARB for Arbitrum Foundation, or OP for Optimism Collective).
Treating uncirculated native governance tokens as liquid balance sheet assets is an accounting illusion. In reality, native tokens in a DAO treasury represent unissued equity. If a treasury attempts to liquidate a substantial position of its own native token on automated market makers like Uniswap Protocol or Curve Finance, price slippage and low market depth dramatically destroy market capitalization.
To achieve financial durability across multi-year market contractions, leading organizations like MakerDAO / Sky, Aave Governance, and the Lido DAO implement a structured, three-tier asset allocation framework:
A DAO treasury cannot rely on standard private keys held by individuals. To secure capital against insider theft, phishing, and single-point-of-failure compromises, organizations deploy layered cryptographic custody frameworks:
The global standard for decentralized asset custody is Safe (formerly Gnosis Safe).
A Safe is a programmable smart contract account that enforces an M-of-N signature requirement before any transaction can execute:
A multisig alone is insufficient for true decentralization because a colluding majority of signers could theoretically drain the treasury in a single transaction.
To eliminate this vulnerability, DAOs place a TimelockController contract (pioneered by Compound Finance and standardized by OpenZeppelin) between the governance voting system and the treasury vault:
The timelock delay window (typically 48 hours to 7 days) provides a defensive grace period. If a malicious proposal passes (via a governance exploit or voting manipulation), the timelock gives token holders and emergency security councils the time required to trigger an emergency veto or allow liquidity providers to withdraw their capital before the transaction executes.
As organizations grow, requiring a full token-holder vote for every minor expense creates governance fatigue and stalls operations. To balance decentralization with operational agility, modern DAOs implement pod architectures using Zodiac modules developed by Gnosis Guild.
Under this model:
Transferring lumpsum grants to contributors creates moral hazard: recipients receive all funds upfront with no cryptographic guarantee of milestone completion.
To formalize financial operations, DAOs deploy automated payment protocols:
Protocols like Sablier, LlamaPay, and Superfluid transform payroll into continuous mathematical streams:
For software development and external security audits, treasuries partner with platforms like Gitcoin and CharmVerse to deploy milestone-escrow contracts. Funds are released in tranches only when specific, verifiable technical deliverables (such as public GitHub pull requests, test suites, or audit reports) are formally reviewed and approved by the engineering pod.
The financial history of decentralized finance includes several sophisticated attacks targeting liquid DAO treasuries:
In early governance frameworks where voting weight was measured strictly at the exact block a proposal was executed, attackers exploited instant capital liquidity.
In the infamous Beanstalk Farms exploit of April 2022:
Modern governance frameworks neutralize this attack vector by enforcing snapshot checkpoints: voting power is calculated based on token balances recorded at a historical block height prior to proposal publication, rendering flash loans useless for acquiring voting weight.
When a DAO native governance token market capitalization falls below the liquid net asset value (NAV) of its treasury, the DAO becomes vulnerable to economic takeover by activist hedge funds or malicious cartels:
To defend against economic liquidations, protocols deploy specialized "ragequit" mechanisms (modeled on the original MolochDAO framework) or implement constitutional veto rights held by a trusted security council.
To reconcile decentralized autonomy with rapid emergency response, mature protocols deploy emergency Security Councils and dual-governance architectures:
Security Council Veto Modules: Deployed on Arbitrum and Optimism, Security Councils are independent bodies of vetted security experts holding a high-threshold multi-signature key (e.g. 9-of-12 signers). If an on-chain proposal contains a critical exploit, reentrancy bug, or economic attack vector, the Security Council can invoke emergency pause precompiles or veto the queued transaction before the TimelockController delay expires.
Dual-Governance and Staker Vetoes: Pioneered by the Lido DAO, dual-governance creates checks and balances between governance token holders (LDO) and protocol capital depositors (stETH). If LDO holders approve a proposal that endangers stETH collateral (such as modifying oracle parameters or draining protocol reserves), stETH holders can lock their assets into an escrow contract to trigger a governance deadlock, preventing execution until both parties align or enabling users to safely exit the system.
A critical oversight of early DAOs was assuming that operating on a decentralized blockchain shields participants from legal liability.
In landmark judicial rulings, including CFTC v. Ooki DAO and Sero v. Block-O-To, United States federal courts established that an unincorporated DAO is legally categorized as a General Partnership:
To mitigate personal liability, modern DAOs wrap their operations in specialized legal entity structures:
Engineering teams establishing a decentralized protocol should adhere to these baseline principles:
TimelockController with at least a 72-hour delay.By treating decentralized treasury management as an exercise in adversarial engineering, mathematical asset allocation, and strict cryptographic custody, DAOs can build robust financial foundations capable of surviving cyclical market downturns and sustaining decentralized protocols for decades to come.
Explore more guides and career playbooks