
How to Pass a Solidity Technical Interview
An empirical thesis and comprehensive preparation guide for passing senior Solidity technical interviews, analyzing live coding challenges, EVM storage mechanics, adversarial exploit modeling, and protocol architecture rounds.
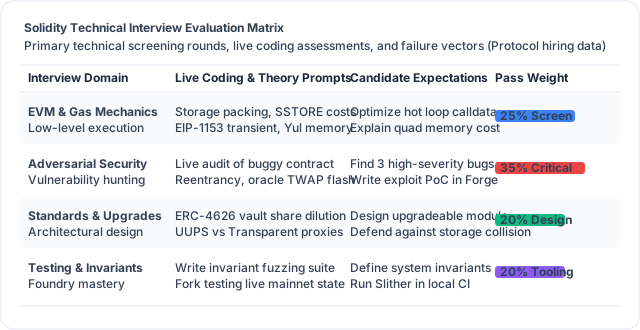
The technical evaluation process for smart contract developers differs fundamentally from conventional Web2 software engineering interviews. In standard cloud application interviews, interviewers evaluate algorithmic complexity using abstract data structures, asymptotic Big-O runtime notations, and distributed system caching patterns. In smart contract engineering, candidate evaluations prioritize economic security, adversarial vulnerability identification, gas consumption optimization, and deep familiarity with low-level Ethereum Virtual Machine (EVM) specified by the Ethereum Foundation opcodes.
Because deployed smart contracts manage hundreds of millions of dollars in user collateral verified on Etherscan without the possibility of post-exploit transaction rollbacks, protocol teams maintain rigorous screening filters. According to industry hiring telemetry from Web3.career and the Electric Capital Developer Report, protocol engineering teams accept fewer than five percent of applicants who enter live technical interview loops. A candidate must demonstrate far more than basic syntax fluency. They must show that they think like a defensive security researcher, an assembly-level gas optimizer, and a protocol architect.
The Structure of a Modern Smart Contract Technical Loop
Institutional protocol teams, venture-backed decentralized finance protocols, and security research firms structure technical evaluations across four sequential assessment rounds:
Round 1: EVM Fundamentals and Gas Mechanics
This technical screen evaluates whether a candidate understands the virtual machine beneath the Solidity language abstraction. Interviewers probe low-level memory layouts, storage packing rules, gas costs associated with specific opcodes, and call context semantics.
Candidates are asked to contrast CALL, STATICCALL, and DELEGATECALL, explaining how storage pointer resolution functions in upgradeable proxy patterns.
Round 2: Live Adversarial Coding and Exploit Proof-of-Concept
The live coding round rarely asks candidates to build trivial web forms. Instead, candidates are presented with an intentionally vulnerable, stripped-down smart contract in a live Foundry environment.
The interviewer expects the candidate to identify the vulnerability (such as a read-only reentrancy or an uninitialized proxy slot), explain the attack mechanism, and author an executable Foundry Forge exploit test that simulates an attacker draining the protocol balance within a single transaction.
Round 3: Protocol Architecture and Standard Design Patterns
Senior candidates participate in an architecture design session. Prompts frequently involve designing a simplified lending pool, an automated market maker vault like Uniswap Labs v4 hooks, a staking distributor like Lido Finance, or a cross-chain bridging module.
Interviewers evaluate standard interface selections, such as the ERC-4626 Tokenized Vault Standard or the ERC-20 Specification, oracle integration choices, and fee distribution math.
Round 4: Production Take-Home Review and Invariant Testing
Many teams require candidates to complete a 48-hour take-home project, such as implementing a custom Uniswap v4 hook or an escrow system. In the subsequent review session, the panel challenges the candidate's test coverage, invariant property formulations, fuzzing configurations, and static analysis outputs.
EVM Data Locations and Storage Slot Mathematics
A primary separator between junior developers and senior smart contract engineers is a mathematical comprehension of the EVM memory hierarchy. Interviewers frequently probe candidate understanding across four distinct data spaces:
Storage Slot Packing and SSTORE Economics
EVM storage is structured as a mapping of 2^256 slots, each measuring 32 bytes. Writing to an uninitialized storage slot using the cold SSTORE opcode consumes 20,000 gas units, whereas reading a cold slot with SLOAD costs 2,100 gas. In contrast, memory writes cost 3 gas plus memory expansion fees.
Candidates must demonstrate how variable ordering enables storage packing. When adjacent state variables require less than 32 bytes, the compiler packs them into a single storage slot:
// Inefficient ordering: Consumes 3 storage slots (96 bytes)
contract Inefficient {
    uint128 public a; // Slot 0 (16 bytes used, 16 bytes wasted)
    uint256 public b; // Slot 1 (32 bytes used)
    uint128 public c; // Slot 2 (16 bytes used, 16 bytes wasted)
}

// Packed ordering: Consumes 2 storage slots (64 bytes)
contract Packed {
    uint128 public a; // Slot 0 (16 bytes)
    uint128 public c; // Slot 0 (16 bytes, packed together)
    uint256 public b; // Slot 1 (32 bytes)
}
Senior candidates are expected to calculate how complex mappings and dynamic arrays store data. In Solidity, the storage slot for a mapping element mapping(address => uint256) at declaration slot p is derived using the Keccak-256 hash:
$$ ext{Slot Key} = ext{keccak256}( ext{abi.encode}(k, p))$$
For dynamic arrays declared at slot p, the length of the array resides in slot p, while elements are stored sequentially starting at $ ext{keccak256}( ext{abi.encode}(p))$.
Transient Storage and EIP-1153
Interviewers in 2026 frequently test candidate familiarity with recent hard fork features, specifically EIP-1153 Transient Storage. Candidates must explain that transient storage provides gas-efficient storage slots that persist across external calls within a single transaction, but automatically discard once transaction execution finishes.
Transient storage opcodes (TSTORE and TLOAD) cost a fixed 100 gas, eliminating expensive warm SSTORE writes for temporary reentrancy locks and ERC-20 approval forwarding.
Adversarial Vulnerability Hunting: The Live Coding Arena
During live coding rounds, candidates must demonstrate structured defensive problem-solving. Interviewers assess whether the candidate mechanically rushes into writing syntax or methodically analyzes threat models.
The most common live coding scenarios involve detecting and remediating classic and subtle exploit vectors:
Scenario 1: Spot Oracle Flash Loan Manipulation
The candidate is presented with a lending contract that calculates user borrow limits based on the instantaneous token reserve balances of a Uniswap Labs pair.
Expected Candidate Response: The candidate immediately flags that spot reserves are susceptible to single-block flash loan manipulation. An attacker can borrow millions in DAI, trade through the pool to manipulate spot price ratios, borrow unbacked collateral, and exit.
Remediation: The candidate demonstrates how to integrate decentralized oracle networks like Chainlink Documentation or Pyth Network, or compute a geometric Time-Weighted Average Price (TWAP) with an extensive observation window.
Scenario 2: ERC-4626 Share Inflation Attacks
The candidate is asked to review an implementation of the ERC-4626 Tokenized Vault Standard.
Expected Candidate Response: The candidate checks whether the vault implements virtual shares and virtual assets (dead shares) to defend against the first-depositor share inflation attack. In an unprotected vault, an initial depositor can deposit 1 wei of underlying tokens, receive 1 share, and subsequently donate a large asset amount directly to the vault contract. Subsequent depositors face severe rounding down to zero due to integer division truncation, losing their deposits without receiving minted vault shares.
Remediation: The candidate refactors the exchange rate formula to include virtual offsets:
$$ ext{Shares} = rac{ ext{Assets} imes ( ext{TotalShares} + 10^d)}{ ext{TotalAssets} + 1}$$
// Defense against first-depositor share inflation using OpenZeppelin ERC4626
function _convertToShares(uint256 assets, Math.Rounding rounding) internal view virtual override returns (uint256) {
    return assets.mulDiv(totalSupply() + 10 ** _decimalsOffset(), totalAssets() + 1, rounding);
}
Scenario 3: Delegatecall Proxy Storage Collisions
The interviewer provides a Transparent or UUPS proxy contract from OpenZeppelin with an updated implementation contract.
Expected Candidate Response: The candidate analyzes the storage variable layout, checking whether the new implementation contract inserts new state variables before existing variables. The candidate explains that inserting variables shifts storage offsets, corrupting state in the proxy contract. They explain the ERC-7201 namespaced storage pattern, which assigns distinct storage root hashes to modular state structs to prevent layout collisions during upgrades.
Mastering the Modern Testing Stack: Foundry, Invariants, and Fuzzing
Demonstrating mastery of Foundry has become a non-negotiable requirement in technical interviews. Interviewers expect candidates to write clean test suites using Forge cheatcodes, perform fork testing against live networks tracked on DefiLlama and Dune Analytics, including Arbitrum Docs, Optimism, and Polygon Labs, like Arbitrum Docs or Base, and configure automated fuzzers.
Candidates should demonstrate fluency with core Forge cheatcodes:
-
vm.prank(address): Simulatesmsg.senderfor the subsequent external call. -
vm.deal(address, uint256): Sets an account's ether balance. -
vm.warp(uint256)andvm.roll(uint256): Advances block timestamps and block numbers to test timelocks and vesting schedules. -
vm.expectRevert(bytes4): Asserts that the subsequent call reverts with an exact custom error selector.
// SPDX-License-Identifier: MIT
pragma solidity 0.8.28;

import {Test} from "forge-std/Test.sol";
import {StakingRewards} from "../src/StakingRewards.sol";

contract StakingRewardsInterviewTest is Test {
    StakingRewards public pool;
    address public user = makeAddr("user");

    function setUp() public {
        pool = new StakingRewards();
        vm.deal(user, 10 ether);
    }

// @notice Property-based fuzz test with bound enforcement
    function testFuzz_StakingAccountingIntegrity(uint96 amount) public {
        vm.assume(amount > 0.05 ether && amount < 10 ether);

        vm.prank(user);
        pool.stake{value: amount}();

        assertEq(pool.userStake(user), amount);
        assertEq(address(pool).balance, amount);
    }
}
Senior candidates distinguish themselves by explaining invariant property testing. They define system properties that must hold true across randomized sequence calls, such as ensuring that total issued protocol claims never exceed underlying reserve deposits.
Candidates also discuss static analysis integration using Slither and Solhint, formal verification via Halmos and Certora, and transaction debugging using Tenderly.
Advanced Live Coding: Reentrancy and Transient Storage Mutexes
A staple live coding prompt in senior interviews involves refactoring a vulnerable withdrawal mechanism into a high-performance, non-reentrant contract.
The candidate is presented with code vulnerable to cross-function reentrancy, where multiple functions interact with the same underlying state balances. The interviewer assesses whether the candidate grasps both the classical Checks-Effects-Interactions (CEI) mitigation and modern transient storage optimizations:
// SPDX-License-Identifier: MIT
pragma solidity 0.8.28;

contract HighPerformanceVault {
    mapping(address => uint256) public balances;

/ EIP-1153 Transient Storage Mutex slot identifier
    bytes32 private constant REENTRANCY_GUARD_SLOT = keccak256("vault.transient.guard");

    error ReentrancyGuarded();
    error TransferFailed();
    error InsufficientBalance();

    modifier nonReentrantTransient() {
        bytes32 slot = REENTRANCY_GUARD_SLOT;
        assembly {
            if tload(slot) {
/ Revert with ReentrancyGuarded() selector (0x8b8e01ce)
                mstore(0x00, 0x8b8e01ce)
                revert(0x1c, 0x04)
            }
            tstore(slot, 1)
        }
        _;
        assembly {
            tstore(slot, 0)
        }
    }

    function deposit() external payable {
        balances[msg.sender] += msg.value;
    }

    function withdraw(uint256 amount) external nonReentrantTransient {
        uint256 balance = balances[msg.sender];
        if (balance < amount) revert InsufficientBalance();

/ 1. Checks & Effects: Apply state mutation before external call
        balances[msg.sender] = balance - amount;

/ 2. Interaction: External transfer
        (bool success, ) = msg.sender.call{value: amount}("");
        if (!success) revert TransferFailed();
    }
}
By leveraging inline Yul assembly with tstore and tload, the candidate demonstrates awareness of cutting-edge gas optimization, reducing reentrancy guard overhead from 2,100 gas to a mere 100 gas per execution.
The Signature Verification Assessment: EIP-712 and Permit Standards
Senior technical interviews frequently examine cryptographic signature verification. In decentralized finance protocols like Aave Governance, Compound Finance, and MakerDAO / Sky, users execute gasless approvals via the permit standard, eliminating separate approval transactions.
The interviewer expects candidates to articulate the core requirements of EIP-712 Typed Structured Data:
- Domain Separator Formulation: Preventing replay attacks across multiple chains or distinct contracts by binding signatures to a domain separator:
$$ ext{DomainSeparator} = ext{keccak256}( ext{abi.encode}( ext{TYPE_HASH}, ext{NAME_HASH}, ext{VERSION_HASH}, ext{chainId}, ext{verifyingContract}))$$
-
Signature Malleability Defense: The candidate explains that in raw ECDSA, for any valid signature pair $(r, s)$, the inverted signature $(r, -s \pmod n)$ is also mathematically valid. To prevent signature malleability, production contracts use audited utility libraries from OpenZeppelin or Solady that reject signatures where $s > ext{secp256k1n} / 2$.
-
Nonce Tracking: Ensuring that each signed permit or meta-transaction increments an internal user nonce to prevent transaction replay within the same contract.
Candidates comfortable with signature verification can effortlessly discuss Account Abstraction architectures under ERC-4337 and EIP-7702, explaining how bundlers and paymasters validate off-chain UserOperations before submitting them to the singleton EntryPoint.
Multi-token standards like the ERC-1155 Multi Token Standard and decentralized liquidity designs like Curve Finance are cited to demonstrate breadth across different DeFi sectors.
Architecture and System Design: The DeFi Protocol Round
In system design rounds, interviewers evaluate how a candidate designs composable financial infrastructure. Prompts commonly request the architecture for an automated lending market or a multi-tier staking contract:
-
Modularity and Separation of Concerns: The candidate separates accounting state, oracle price calculation, risk parameters, and user-facing entry points into modular contracts rather than building a monolithic file.
-
Access Control Architecture: Implementing role-based access control (RBAC) via OpenZeppelin AccessControl or two-step ownership transfers (
Ownable2Step) to prevent accidental ownership transfers to unrecoverable addresses. -
Emergency Controls and Circuit Breakers: Incorporating pause capabilities, rate limiters on withdrawals, and timelocks to mitigate damage in the event of an unforeseen economic vulnerability.
-
Client and Indexing Integration: Emitting indexed events that allow off-chain indexers such as The Graph or frontend client libraries like Viem and Wagmi to display protocol metrics without overloading public JSON-RPC nodes provisioned by Alchemy or Infura.
Candidate Communication, Red Flags, and Interview Pitfalls
Technical competence alone does not guarantee an offer. Smart contract hiring panels evaluate candidate communication and intellectual rigor:
Critical Failure Vectors in Interviews
-
Ignoring Security Assumptions: Writing code that assumes input addresses or external contract calls are honest and non-malicious.
-
Neglecting Gas Consequences: Writing loops that iterate over unbounded dynamic arrays, which will inevitably hit block gas limits as state grows.
-
Silent Assumption Making: Coding without articulating assumptions regarding reentrancy guards, decimal scaling (e.g. 6 decimals for USDC vs 18 for ETH), or division precision loss.
-
Defensiveness During Code Review: Resisting interviewer feedback when an edge case or potential vulnerability is pointed out.
High-Signal Candidate Behaviors
-
Explicit Threat Modeling: Before writing logic, listing all potential attackers, trusted actors, and external dependencies.
-
Proactive Invariant Definition: Stating the mathematical invariants of the system before authoring implementation code.
-
Gas-Aware Refactoring: Demonstrating how variable caching, custom errors, and calldata references reduce transaction gas overhead.
-
Practical Experience Citing: Referencing established audit reports from Trail of Bits or OpenZeppelin, wargame challenges on Damn Vulnerable DeFi or Ethernaut, and competitive audit contests on Code4rena and Sherlock.
Compensation Benchmarks and Negotiation Dynamics
Smart contract engineering commands some of the highest compensation packages across software engineering. According to compensation reports compiled by Pantera Capital and Web3.career:
-
Junior to Mid-Level Smart Contract Engineers: Starting base salaries typically range from $110,000 to $160,000 USD, accompanied by token grants vesting over three to four years.
-
Senior Smart Contract Engineers: Base compensations range between $170,000 and $240,000 USD, with significant token incentive packages.
-
Protocol Leads and Security Architects: Lead engineers managing core protocol repositories at high-TVL protocols earn base salaries from $220,000 to $320,000 USD, often augmented by project advisory shares or profit-sharing mechanisms.
Candidates negotiate effectively by presenting verifiable on-chain proof of work: public GitHub repositories featuring comprehensive Foundry test suites, high rankings on competitive audit leaderboards, and documented bug disclosures on Immunefi.
Passing a senior Solidity technical interview requires disciplined preparation across virtual machine mechanics, rigorous invariant testing, and adversarial security thinking. By mastering EVM memory layouts, adopting modern native toolchains, and demonstrating defensive design instincts, engineers can navigate demanding technical loops and secure leadership roles building decentralized financial infrastructure.