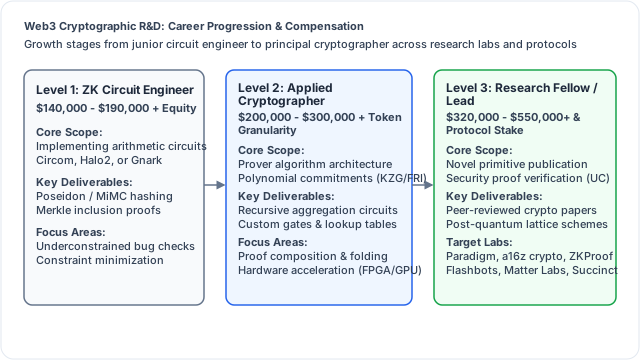
A comprehensive career roadmap for breaking into Web3 cryptographic research and development, examining mathematical prerequisites, polynomial commitment schemes, research lab structures, and compensation tiers.
How to Break Into Web3 Cryptographic Research and Development
For decades, advanced academic cryptography operated largely within theoretical computer science departments, defense intelligence agencies, and corporate standards committees. Breakthroughs in zero-knowledge proofs, multi-party computation, and lattice mathematics often spent years relegated to peer-reviewed conference proceedings before finding practical implementation in industrial software.
The rapid rise of public decentralized networks has inverted this dynamic. Modern distributed state machines such as the Ethereum Foundation, Solana Protocol, and the Bitcoin Network are essentially applied economic and cryptographic experiments operating in hostile adversarial environments. The requirements of scaling transaction throughput via validity rollups, eliminating frontrunning through encrypted mempools, and preserving user sovereignty have transformed theoretical cryptography into a commercial imperative.
Today, cryptographic research and development (R&D) in Web3 represents one of the highest-impact and most lucrative domains in computer science. Venture-backed research laboratories, protocol foundations, and zero-knowledge infrastructure companies compete intensely for talent capable of formulating novel cryptographic primitives and translating abstract algebra into high-throughput production code. This roadmap details the mathematical foundations, core specialization tracks, institutional landscape, compensation trajectories, and practical contribution pathways required to build a career in Web3 cryptographic R&D.
Foundational Mathematical Prerequisites
Breaking into cryptographic research requires building deep mathematical fluency across four foundational pillars: abstract algebra, number theory, lattice geometry, and computational complexity theory.
1. Abstract Algebra and Finite Field Arithmetic
Computations in zero-knowledge systems and threshold protocols do not operate over classical 32-bit or 64-bit IEEE floating-point representations. Instead, they operate over finite fields $\mathbb{F}_p$, where $p$ is a large prime number chosen to correspond to the scalar field of an elliptic curve:
- Galois Field Extensions: Understanding extension fields $\mathbb{F}{p^2}, \mathbb{F}{p^6}, \mathbb{F}_{p^{12}}$ required for computing pairing maps and tower field constructions such as Binius Tower Fields.
- Polynomial Quotient Rings: Manipulating polynomial rings $\mathcal{R}_q = \mathbb{Z}_q[X] / (X^N + 1)$ which form the fundamental algebraic structures behind lattice-based schemes like BGV, BFV, and Ring Learning With Errors (RLWE).
- Roots of Unity and Cosets: Applying multiplicative cyclic subgroups for evaluating Number Theoretic Transforms (NTTs) in polynomial interpolation and evaluations.
2. Elliptic Curves and Bilinear Pairings
Elliptic curves provide the geometric framework for asymmetric signatures and pairing-based polynomial commitments:
- Weierstraß, Montgomery, and Edwards Curves: Converting equations across different coordinate models (projective coordinates, Jacobian coordinates) to eliminate expensive modular inversions during group operations.
- Pairing-Friendly Curves: Analyzing parameters of pairing-friendly curves such as BN254 (alt_bn128), BLS12-381, and BLS12-377, evaluating embedding degrees and CM discriminant requirements.
- Cycles of Curves: Constructing cycles of pairing-friendly curves, such as the Tweedledee/Tweedledum pair or the Pasta curves (Pallas and Vesta) designed by Daira Hopwood, Sean Bowe, Jack Grigg, and Str4d at the Electric Coin Company, where the scalar field of one curve equals the base field of the other. This algebraic property enables recursive zero-knowledge proof verification without non-native field simulation overhead.
3. Lattice-Based Cryptography and Post-Quantum Mechanics
With classical public-key infrastructure vulnerable to Shor's Algorithm on Quantum Computers, cryptographic R&D is heavily focused on lattice-based primitives:
- Learning With Errors (LWE): Formalized by Oded Regev at Tel Aviv University, proving security reductions from worst-case lattice problems such as the Shortest Vector Problem (SVP).
- NIST Post-Quantum Standards: Studying standardized algorithms selected by the NIST Post-Quantum Cryptography Project, including ML-KEM (Kyber) for key encapsulation and ML-DSA (Dilithium) for digital signatures.
4. Complexity Theory and the Simulation Paradigm
Understanding reductionist security proofs is essential for formal cryptographic verification:
Core Specialization Tracks in Web3 Cryptographic R&D
Cryptographic R&D is not a monolithic discipline. Aspiring researchers generally specialize across one of four core technical tracks:
Track 1: Proof Systems, PCS, and Folding Schemes
Researchers in proof systems design algorithms that compress arbitrary execution traces into succinct cryptographic arguments:
- Polynomial Commitment Schemes (PCS): Designing commitment protocols that balance prover time, verifier time, and proof size. Schemes span Kate-Zaverucha-Goldberg (KZG Commitments), Fast Reed-Solomon Interactive Oracle Proofs of Proximity (FRI Protocol), and inner-product arguments like Bulletproofs.
- Folding and Accumulation Schemes: Pioneered by Abhiram Kothapalli, Srinath Setty, and Riad Wahby in Nova, and expanded in Supernova and HyperNova. Rather than verifying expensive SNARK proofs recursively via inner circuits, folding schemes accumulate repetitive execution steps into a single instance via simple vector linear combinations, deferring final succinct proof generation to the very end of computation.
- Lookup Arguments: Inventing high-throughput lookup protocols such as Lasso by Srinath Setty, Justin Thaler, and Riad Wahby and cq (Cached Quotients), drastically reducing the gate cost of non-algebraic instructions like bitwise operations.
Track 2: Threshold Cryptography and Secure MPC
Multi-Party Computation enables mutually distrusting nodes to jointly compute a function over their private inputs without any single party learning the inputs of others:
Track 3: Fully Homomorphic Encryption (FHE)
Specialists in FHE work at the bleeding edge of confidential smart contracts and blind cloud computation:
- Noise Management and Programmable Bootstrapping: Implementing torus-based FHE algorithms developed by Ilaria Chillotti et al. in TFHE, optimizing bootstrap evaluation keys to run within millisecond thresholds.
- Confidential Virtual Machines: Designing execution models such as the Zama fhEVM, abstracting homomorphic operations into Solidity opcodes for protocols like Fhenix and Inco Network.
Track 4: Consensus Cryptography, Randomness, and VDFs
Designing cryptographic primitives that protect distributed consensus and prevent transaction manipulation:
- Verifiable Delay Functions (VDFs): Implementing sequential, non-parallelizable functions formulated by Benjamin Wesolowski and Krzysztof Pietrzak. VDFs enforce verifiable wall-clock time delays on-chain, securing leader election randomness and frontrunning prevention.
- Verifiable Random Functions (VRFs): Providing unbiased, publicly verifiable pseudorandomness for smart contracts and proof-of-stake slot selection, championed by Micali, Rabin, and Vadhan and deployed across systems like Chainlink VRF and Algorand.
Research Institutions, Venture Labs, and Academic Consortia
Unlike traditional corporate engineering where research happens behind closed doors, Web3 cryptographic research is inherently open and collaborative:
Key Ecosystem Organizations
- Paradigm Research: Produces high-impact applied research across MEV mitigation, rollup architectures, and succinct proving pipelines.
- a16z crypto research: An applied research team consisting of leading academic cryptographers and multidisciplinary scientists focusing on polynomial commitment schemes, SNARK security, and mechanism design.
- Stanford Center for Blockchain Research (CBR): Co-directed by Professor Dan Boneh, the Stanford CBR serves as a premier academic center for zero-knowledge proofs, threshold signatures, and blockchain security.
- Berkeley RDI (Center for Responsible, Decentralized, and Distributed Intelligence): Directed by Professor Dawn Song, Berkeley RDI conducts research on zero-knowledge systems, secure computing, and decentralized AI.
- Privacy and Scaling Explorations (PSE): An applied research initiative funded by the Ethereum Foundation, building open-source cryptographic libraries including Semaphore, MACI, and zero-knowledge identity primitives.
- ZKProof Community Standards: An international organization coordinating academic researchers, industrial practitioners, and standards committees to establish uniform mathematical specifications and security benchmarks for zero-knowledge proofs.
Career Trajectory, Roles, and Compensation Bands
Because cryptographic talent is exceptionally scarce, compensation in Web3 cryptographic R&D outpaces most traditional software engineering and academic tracks:
1. Associate Cryptographic Researcher
- Profile: Recent Ph.D. or Master's graduate in computer science, mathematics, or physics, or exceptional self-taught software engineers with demonstrated mastery of abstract algebra.
- Responsibilities: Implementing published cryptographic papers in performant Rust or C++, constructing circuit prototypes in Circom, Halo2, or Noir, and profiling constraint counts and memory usage.
- Deliverables: Reproducing academic benchmarks, building unit-test harnesses for arithmetic circuits, and auditing edge-case constraints.
2. Applied Cryptographer / Research Scientist
- Profile: 3 to 6 years of applied cryptographic experience with a track record of open-source contributions or peer-reviewed academic publications.
- Responsibilities: Designing custom polynomial commitment schemes, architecting recursive folding pipelines, formalizing security reductions, and optimizing finite field arithmetic for specialized instruction sets (AVX-512, NEON).
- Deliverables: Co-authoring technical whitepapers, optimizing prover performance by multiples, and architecting zero-knowledge virtual machine components.
3. Principal Cryptographer / Research Fellow
- Profile: Recognized authority in the cryptographic community with multiple tier-1 publications (IACR Crypto, Eurocrypt, Asiacrypt) and substantial contributions to production blockchain protocols.
- Responsibilities: Setting the technical and cryptographic roadmap for foundational protocols, proving universal composability theorems, advising executive leadership on security and post-quantum migration, and serving as a public thought leader.
- Deliverables: Architectural conception of novel proof systems, groundbreaking academic preprints, and safeguarding billions in economic security.
Practical Pathways to Break Into the Industry
Aspiring researchers and developers generally transition into Web3 cryptographic R&D through one of three pathways:
1. The Academic Transition
Academic cryptographers often struggle with production software patterns. To stand out to hiring directors, researchers must demonstrate that their theoretical work compiles and executes efficiently:
- Take a published theoretical paper (such as a novel polynomial commitment scheme or vector commitment) and build an open-source Rust implementation using libraries like arkworks.
- Profile memory allocations, multi-threading bottlenecks via Rayon, and serialization costs.
- Publish clear documentation and reproducible automated benchmarks.
2. The Systems Engineer Transition
Experienced low-level systems engineers can enter cryptographic R&D by focusing on the computational bottlenecks of proof generation:
- Master Multi-Scalar Multiplication (MSM) algorithms, including Pippenger's bucket method and signed-digit representations.
- Optimize Number Theoretic Transforms (NTT) using hardware vectorization (SIMD) and cache-friendly memory layouts.
- Contribute GPU acceleration kernels to open-source libraries like Ingonyama ICICLE or write custom CUDA kernels for finite field arithmetic.
3. The Independent Researcher Transition
Self-taught engineers can build an undeniable portfolio through competitive research challenges and cryptographic capture-the-flag (CTF) competitions:
- Compete in the annual ZPrize Competition, which awards millions in non-dilutive grants for pioneering hardware acceleration and circuit optimization.
- Participate in cryptographic CTFs such as the Paradigm CTF and write detailed, mathematically rigorous post-mortems analyzing the underlying algebraic vulnerabilities.
- Review and formally verify open-source circuits using tools like Veridise Picus or Ecne, reporting missing constraints via Immunefi bug bounties, alongside research methodologies detailed by Trail of Bits and OpenZeppelin Security.
Essential Developer Tooling and Academic Resources
To accelerate your preparation, immerse yourself in the following production libraries, educational platforms, and cryptographic hubs:
Essential Study Curriculum
- zk-learning.org MOOC: A comprehensive zero-knowledge proofs course organized by leading academic faculty including Professor Dan Boneh at Stanford, Turing Laureate Shafi Goldwasser, Professor Dawn Song at UC Berkeley, and Professor Justin Thaler at Georgetown.
- The arkworks Ecosystem: The premier open-source Rust ecosystem for programming zero-knowledge proof systems, providing modular traits for finite fields, elliptic curves, and SNARK gadgets.
- Thaler's "Proofs, Arguments, and Zero-Knowledge": The definitive modern academic textbook by Professor Justin Thaler, available freely online, detailing multilinear polynomial commitments, sumcheck protocols, and interactive oracle proofs.
- 0xPARC Applied ZK Programs: Practical seminars, hackathons, and research residencies designed to onboard software engineers into advanced cryptographic research and homomorphic computing.
The Road Ahead for Cryptographic R&D
Cryptographic R&D in Web3 is evolving at an unprecedented pace. The coming decade will witness the practical deployment of:
- Tower-Field and Multilinear SNARKs: Architectures like Binius operating over 1-bit binary base fields, eliminating the need for expensive elliptic curve group arithmetic entirely.
- Post-Quantum Layer 1 Migrations: Upgrading the core signature schemes and state commitment trees of major blockchains to quantum-resistant lattice alternatives.
- Composable Confidential Computing: Merging zero-knowledge validity proofs, threshold multi-party computation, and fully homomorphic encryption into a unified, privacy-preserving distributed state machine.
Researchers and engineers who invest the effort to master foundational abstract algebra, mathematical reductions, and low-level systems engineering will find themselves at the center of the next generation of cryptographic protocols.