How Regulations and Culture Are Changing the Game in Web3 Compliance Guide
An in-depth analysis of the dual forces shaping the Web3 ecosystem - global regulatory frameworks (EU MiCA, US SEC/CFTC) and crypto-native culture - exploring legal engineering and compliance careers.

Decentralized Finance (DeFi) protocols manage tens of billions of dollars in Total Value Locked (TVL), yet the permissionless nature of smart contracts introduces unique operational vectors: reentrancy exploits, oracle price manipulation, flash loan attacks, and economic de-pegging events. Over the past decade, billions of dollars have been lost due to protocol vulnerabilities and unhedged market risks.
Historically operating in a permissionless, regulatory gray zone, the expansion of digital assets into a multi-trillion-dollar global asset class has drawn intense scrutiny from financial regulators, tax authorities, and law enforcement agencies worldwide. Simultaneously, the core culture of Web3 - grounded in cypherpunk principles of open-source transparency, self-sovereign key ownership, and decentralized governance - resists centralized encroachment.
This comprehensive guide examines global regulatory frameworks (including the EU Markets in Crypto-Assets regulation, US SEC/CFTC enforcement actions, and FinCEN Travel Rule mandates), the core tenets of crypto-native culture, hybrid compliance architectures, and expanding career opportunities for Web3 legal counsel and compliance engineers.
1. The Global Regulatory Landscape: Key Jurisdictions & Frameworks
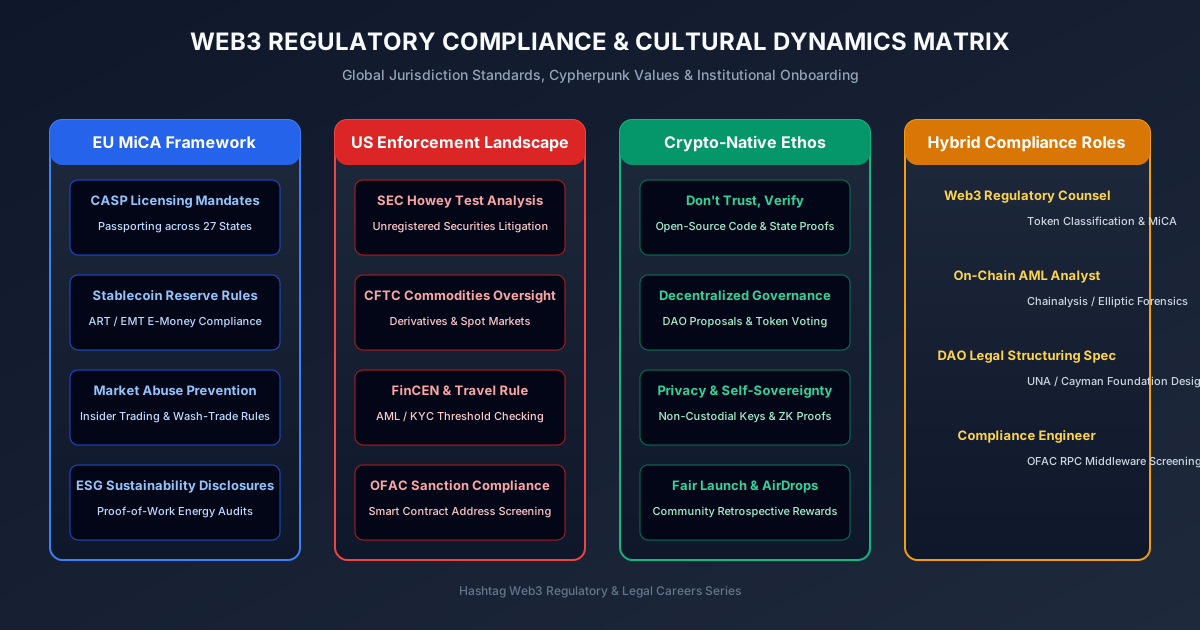
As governments integrate crypto assets into global financial systems, different regions have adopted contrasting regulatory methodologies ranging from comprehensive legislation to enforcement-led supervision.
                      GLOBAL REGULATORY APPROACH COMPARISON

 ┌────────────────────────────────────────────────────────────────────────┐
 │ 3. ASIA-PACIFIC REGIONS  (Hong Kong VASP, Singapore MAS Licensing)     │
 ├────────────────────────────────────────────────────────────────────────┤
 │ 2. UNITED STATES         (Enforcement-Led, SEC Howey Test, CFTC Spot)  │
 ├────────────────────────────────────────────────────────────────────────┤
 │ 1. EUROPEAN UNION        (MiCA Legislation, Passporting across 27 States)│
 └────────────────────────────────────────────────────────────────────────┘
1. European Union: Markets in Crypto-Assets (MiCA)
The EU's MiCA framework represents the world's first comprehensive regulatory regime for digital assets, establishing uniform rules across all 27 EU member states:
- Crypto-Asset Service Provider (CASP) Licensing: Regulates exchanges, custodians, and advisory firms under strict capital requirements, operational resilience standards, and customer asset segregation mandates.
- Asset-Referenced Tokens (ARTs) and E-Money Tokens (EMTs): Imposes strict liquidity reserve ratios and issuer authorization rules for stablecoins pegged to fiat currencies or baskets of assets.
- DeFi and NFT Scope Exemptions: Fully decentralized protocols operating without central intermediaries are excluded from direct CASP licensing, incentivizing true protocol decentralization.
2. United States: Enforcement-Driven Supervision
In contrast to single-legislation frameworks, the US regulatory landscape relies on existing statutory authorities and judicial enforcement actions:
- SEC and the Howey Test: The Securities and Exchange Commission (SEC) applies the 1946 Howey Test to evaluate whether token sales constitute "investment contracts" (unregistered securities).
- CFTC Derivatives Jurisdiction: The Commodity Futures Trading Commission (CFTC) regulates digital commodities (such as Bitcoin and Ethereum) and oversight of crypto derivatives and futures markets.
- FinCEN Travel Rule & FATF Standards: The Financial Crimes Enforcement Network mandates that virtual asset service providers (VASPs) collect and transmit originator and beneficiary information for transfers exceeding $1,000 USD.
2. Crypto-Native Cultural Tenets vs. Regulatory Mandates
The tension between regulatory mandates and community values creates complex operational challenges for Web3 protocol builders.
                COMMUNITY CULTURE vs. REGULATORY MANDATES

  Crypto-Native Ethos                    Regulatory Compliance Mandate
 ┌──────────────────────────────┐        ┌──────────────────────────────┐
 │ • Self-Sovereign Keys        │        │ • Mandated KYC Identity Checks│
 │ • Open-Source Transparent Code│       │ • OFAC Sanctions Screening   │
 │ • Permissionless Execution   │  VS.  │ • Anti-Money Laundering (AML)│
 │ • Pseudonymous Privacy       │        │ • Centralized Tax Reporting  │
 └──────────────────────────────┘        └──────────────────────────────┘
Core Cultural Principles
- Don't Trust, Verify: Reliance on open-source, verifiable smart contract bytecode and cryptographic state proofs rather than institutional brand promises or legal contracts.
- Community Ownership & Progressive Decentralization: Projects initiate with core founding teams but progressively transfer treasury management, fee parameters, and code upgrades to token-weighted DAOs.
- Permissionless Access: Ensuring protocols remain accessible to anyone globally with an internet connection and a Web3 wallet, regardless of geographic location or accredited investor status.
3. Hybrid Compliance Architectures: Progressive Decentralization
To navigate global regulations while maintaining community trust, modern Web3 protocols adopt Progressive Decentralization and hybrid legal-technical structures.
                   PROGRESSIVE DECENTRALIZATION TIMELINE

 ┌─────────────────┐       ┌─────────────────┐       ┌─────────────────┐
 │ Stage 1:        │ ────► │ Stage 2:        │ ────► │ Stage 3:        │
 │ Core Team Corp  │       │ Foundation &    │       │ Fully Autonomous│
 │ (C-Corp / DevCo)│       │ DAO Governance  │       │ Immutable DAO   │
 └─────────────────┘       └─────────────────┘       └─────────────────┘
Legal Structuring for Web3 Protocols
- DevCo / Foundation Split: Software development is conducted by a commercial entity (DevCo), while protocol IP and treasury assets are held by an offshore non-profit foundation (e.g., Swiss Foundation, Cayman Foundation Company, or Marshall Islands DAO LLC).
- Unincorporated Nonprofit Associations (UNA): Utilizing state-level UNA frameworks (such as Wyoming's Decentralized Unincorporated Nonprofit Association Act) to provide DAO members with limited liability protection without requiring centralized corporate registration.
- Front-End Compliance vs. Protocol Layer: Centralized web front-ends enforce geoblocking or OFAC wallet screening to satisfy local laws, while the underlying smart contracts remain permissionless on the blockchain layer.
4. Comprehensive Regulatory Matrix Across Asset Classes
Understanding how different token types are classified globally is essential for tokenomics design and protocol structuring.
| Token Classification | Primary Examples | Regulatory Risk Level | Primary Regulatory Bodies | Compliance Requirements |
|---|---|---|---|---|
| Payment / Utility Tokens | ETH, SOL, AVAX | Moderate | CFTC (US), ESMA (EU), MAS (Singapore) | AML/KYC checks on fiat ramps, tax reporting |
| Governance Tokens | UNI, AAVE, MKR | High | SEC (US), BaFin (Germany) | Howey test scrutiny, DAO liability structuring |
| Fiat Stablecoins | USDC, USDT, PYUSD | High | Banking Regulators, EU MiCA, NYDFS | 1:1 liquid reserve audits, e-money issuer licensing |
| Security Tokens / Tokenized RWAs | BUIDL, Ondo OUSG | Ultra-High | SEC, FINRA, FCA (UK) | Accredited investor verification, Reg D / Reg S filings |
| Non-Fungible Tokens (NFTs) | CryptoPunks, Art Blocks | Low to Moderate | Consumer Protection, Tax Authorities | Copyright/IP law compliance, VAT/sales tax tracking |
5. On-Chain Forensic Analytics and AML Middleware
Compliance in Web3 relies heavily on specialized on-chain forensic analytics platforms (such as Chainanalysis, Elliptic, and TRM Labs) that monitor transaction graphs in real time.
                  ON-CHAIN AML & SANCTION SCREENING FLOW

 ┌─────────────────┐       ┌─────────────────┐       ┌─────────────────┐
 │ Incoming Tx /   │ ────► │ Forensics API   │ ────► │ Risk Score      │
 │ RPC Request     │       │ (Chainalysis)   │       │ Evaluation      │
 └─────────────────┘       └─────────────────┘       └────────┬────────┘
                                                              │
                                                              ▼
 ┌─────────────────┐       ┌─────────────────┐       ┌─────────────────┐
 │ Execute App     │ ◄──── │ Pass / Reject   │ ◄──── │ OFAC / Mixer    │
 │ Action          │       │ Decision Gate   │       │ Flag Check      │
 └─────────────────┘       └─────────────────┘       └─────────────────┘
- Risk Scoring Algorithms: Forensics engines calculate risk scores for wallet addresses based on direct or indirect exposure to sanctioned entities (OFAC list), Tornado Cash mixers, darknet markets, or ransomware addresses.
- RPC Middleware Screening: Decentralized applications integrate compliance middleware (such as TRM Wallet Screening API) at the RPC provider layer to block flagged addresses from interacting with dApp interfaces.
9. Zero-Knowledge Cryptography & Privacy-Preserving Compliance (ZK-KYC)
The single greatest technological bridge between crypto-native privacy culture and institutional AML mandates is Zero-Knowledge Proof-Based Compliance (ZK-KYC).
                    ZK-KYC PRIVACY-PRESERVING COMPLIANCE FLOW

 ┌─────────────────┐       ┌─────────────────┐       ┌─────────────────┐
 │ User Identity   │ ────► │ Licensed Identity│ ────► │ Issue ZK         │
 │ Documents (ID)  │       │ Provider (KYC)  │       │ Credential (VC) │
 └─────────────────┘       └─────────────────┘       └────────┬────────┘
                                                              │
                                                              ▼
 ┌─────────────────┐       ┌─────────────────┐       ┌─────────────────┐
 │ Permit dApp     │ ◄──── │ Verify ZK Proof │ ◄──── │ Generate ZK-   │
 │ Execution       │       │ (`isOver18==true`)│      │ SNARK Proof     │
 └─────────────────┘       └─────────────────┘       └─────────────────┘
ZK-KYC Architecture Mechanics
- Off-Chain Verification: An accredited identity provider verifies the user's passport or driver's license off-chain, issuing a W3C Verifiable Credential containing a cryptographic public key signature.
- On-Chain Proof Verification: When interacting with a regulated DEX pool, the user generates a zero-knowledge proof (ZK-SNARK) on their device proving key attributes (e.g., "User is over 18 years old and not a resident of an OFAC-sanctioned country") without revealing their real-world name, date of birth, or home address on-chain.
10. Cross-Border Tax Reporting Frameworks (CARF & DAC8)
Tax authorities worldwide are implementing global automated financial account information exchange agreements specifically targeting digital assets:
- OECD Crypto-Asset Reporting Framework (CARF): Standardizes automatic tax reporting across participating countries, requiring Virtual Asset Service Providers (VASPs) to report annual aggregate gross transaction values for tax residents.
- EU DAC8 Directive: Extends European administrative cooperation rules to crypto assets, requiring CASPs to collect and report transaction data for EU-based users to tax authorities.
11. Step-by-Step Technical Implementation Guide
Below is a Python script demonstrating how to integrate automated OFAC sanction screening for Ethereum wallet addresses using a simulated compliance API:
import json

class MockComplianceAPI:
    """Simulates an on-chain forensics API (e.g., Chainalysis / TRM Labs)."""
    def __init__(self):
        # Simulated sanctioned and high-risk address database
        self.sanctioned_addresses = {
            "0x7FF4154b5B49D5b2AD9809E69f15D18557241306": {"risk_score": 10.0, "category": "OFAC Sanctioned"},
            "0x12D66b265719c3558A75dE256b72B17865653240": {"risk_score": 9.5, "category": "Tornado Cash Mixer"}
        }

    def evaluate_address_risk(self, wallet_address):
        checksum_address = wallet_address.strip()
        if checksum_address in self.sanctioned_addresses:
            data = self.sanctioned_addresses[checksum_address]
            return {"is_blocked": True, "risk_score": data["risk_score"], "reason": data["category"]}
        return {"is_blocked": False, "risk_score": 0.1, "reason": "Low Risk"}

class ComplianceGate:
    def __init__(self, compliance_api):
        self.api = compliance_api

    def validate_transaction_request(self, user_address, requested_amount_usd):
        screening = self.api.evaluate_address_risk(user_address)
        if screening["is_blocked"]:
            print(f"[ACCESS DENIED] Address {user_address} blocked. Reason: {screening['reason']}")
            return False

        # Travel Rule Threshold Check ($1,000 USD)
        if requested_amount_usd >= 1000.00:
            print(f"[TRAVEL RULE TRIGGERED] Tx of ${requested_amount_usd:,.2f} requires VASP KYC exchange.")

        print(f"[ACCESS GRANTED] Transaction approved for {user_address}.")
        return True

# Execution Example
checker = ComplianceGate(MockComplianceAPI())
checker.validate_transaction_request("0x7FF4154b5B49D5b2AD9809E69f15D18557241306", 500.00)
checker.validate_transaction_request("0x388C8150059270105B94261d00344d56A4956d68", 2500.00)
12. Career Opportunities in Web3 Legal, Risk & Compliance
As regulatory clarity expands, legal and compliance talent has become one of the highest-paid and most sought-after categories in Web3 recruiting.
                           CAREER PROGRESSION ROADMAP

 [Traditional Lawyer / Compliance Officer / Developer]
                             │
                             ├───────────────────────┬───────────────────────┐
                             ▼                       ▼                       ▼
                  [Web3 Regulatory Counsel]    [Compliance Engineer]  [DAO Legal Structuring Spec]
                  - MiCA & SEC Token Analysis  - On-Chain Sanction API - Foundation Company Setup
                  - Exchange Licensing         - Travel Rule Systems   - UNA Entity Structuring
In-Demand Roles
-
Web3 Regulatory Counsel:
- Responsibilities: Advise protocol teams on token classification under SEC Howey and EU MiCA frameworks, manage exchange listings, and draft token whitepapers.
- Required Skills: JD / LLM degree, corporate law, securities regulation, deep understanding of blockchain tokenomics.
-
On-Chain Compliance Engineer:
- Responsibilities: Build automated AML/KYC RPC middleware, integrate Chainanalysis/Elliptic APIs, and construct Travel Rule data exchange protocols.
- Required Skills: Python, TypeScript, REST APIs, Web3 RPC integration, knowledge of FATF/FinCEN regulations.
-
DAO Legal Architect:
- Responsibilities: Design legal wrapper structures for DAOs (Cayman Foundations, Marshall Islands DUNA), structure contributor agreements, and minimize member liability.
- Required Skills: Corporate governance, international law, DAO operational mechanics, smart contract governance frameworks.
13. Interview Preparation Playbook for Web3 Legal & Regulatory Roles
Candidates interviewing for legal, regulatory, and compliance engineering roles are routinely tested on real-world regulatory scenarios.
Technical Interview Questions & Answers
Scenario 1: Applying the Howey Test to a New Protocol Governance Token
Question: "A decentralized protocol plans to launch a governance token via an airdrop and liquidity mining program. How do you analyze its risk under the US SEC Howey Test?"
Answer:
- Prong 1: Investment of Money: Airdrops with zero financial contribution reduce Prong 1 risk, but liquidity mining where users lock capital can be interpreted as an investment of money.
- Prong 2: Common Enterprise: Pooled liquidity contracts create horizontal commonality among token holders.
- Prong 3: Expectation of Profits from Managerial Efforts: If token marketing highlights token price appreciation resulting from the core team's development efforts, the token risks classification as an unregistered security. Mitigation involves achieving true protocol decentralization before token launch.
Scenario 2: Complying with the FATF Travel Rule for Self-Custodial Wallets
Question: "How does a crypto exchange comply with the FATF Travel Rule when a user withdraws funds to a self-custodial MetaMask wallet?"
Answer:
- Wallet Ownership Verification: The exchange issues a cryptographic challenge (such as signing a message with the private key) to confirm the user controls the destination address.
- Threshold Assessment: If the withdrawal exceeds $1,000 USD, the exchange verifies the self-custodial status and logs the transaction details in accordance with local regulator guidelines before executing the transfer.
Scenario 3: Legal Liability Analysis for DAO Governance Voters
Question: "If an unincorporated DAO suffers a security breach or legal judgment, can individual token holders who voted on governance proposals be held personally liable?"
Answer:
- General Partnership Risks: Courts in jurisdictions like the US have ruled that unincorporated DAOs operating without a legal wrapper (such as a Cayman Foundation or DUNA) may be classified as General Partnerships, exposing active voting members to joint and several personal liability.
- Legal Wrapper Mitigation: Protocol engineers must establish formal legal wrappers (e.g., Wyoming DUNA or Swiss Foundation) to grant DAOs separate legal personality and limit member liability.
Scenario 4: Structuring a Cayman Foundation for Protocol IP
Question: "Why do Web3 protocols establish Cayman Foundation Companies, and how does this legal entity interface with on-chain DAO governance?"
Answer:
- Orphan Foundation Structure: A Cayman Foundation Company operates without shareholders or equity owners, acting as an independent legal wrapper dedicated exclusively to protocol development.
- DAO Operating Agreement: The Foundation's Memorandum of Association specifies that directors must execute non-binding on-chain DAO governance votes, ensuring legal compliance while maintaining decentralized community control.
14. W3C Decentralized Identifiers (DIDs) in Reusable KYC
Using W3C Decentralized Identifiers (DIDs) and Verifiable Credentials (VCs) enables compliant user identity verification across multiple dApps without redundant KYC submissions:
- Self-Sovereign Identity Storage: Users store identity attestations locally in encrypted mobile wallets or account abstraction smart contract enclaves.
- On-Chain Verifier Execution: DApps verify public key attestations signed by trusted issuers on-chain in sub-milliseconds without storing sensitive personally identifiable information (PII) on public databases.
- Selective Disclosure Proofs: Users present verifiable presentations proving specific compliance thresholds (such as accredited investor status) without disclosing full identity documents or account balances.
15. Real-Time On-Chain Sanction Screening Architecture
Modern Web3 compliance gateways implement real-time sanction screening at both the Web3 provider layer and smart contract router level:
- Smart Contract Blacklisting Hooks: Protocols integrate OpenZeppelin ERC-20 compliance modifiers (
beforeTokenTransfer) linked to oracle feeds that instantly restrict token transfers to or from addresses added to global sanctions registries. - Privacy-Preserving Compliance Routers: Decentralized compliance routers allow users to generate ZK proofs proving their deposit funds have zero transactional history with flagged mixers or illicit entities before depositing into institutional DeFi pools.
Summary and Key Takeaways
The Web3 industry is entering a mature phase where regulatory compliance and crypto-native culture must coexist. By bridging the gap between global legal frameworks (MiCA, SEC, Travel Rule) and decentralized software architectures, compliance engineers and legal specialists play a vital role in enabling institutional adoption while safeguarding protocol decentralization.
Mastering regulatory analysis, DAO legal structuring, and on-chain compliance middleware provides a resilient foundation for a high-impact career in Web3 law and regulatory engineering. As decentralized protocols scale to support global commerce, professionals who possess both technical blockchain expertise and deep regulatory knowledge will continue to command premium compensation and shape the future of legal compliance in decentralized finance.