Loading article...

An empirical technical thesis on blockchain-based voting systems, exploring token-weighted governance, quadratic preference aggregation, gasless off-chain signaling, and zero-knowledge anti-collusion infrastructure.
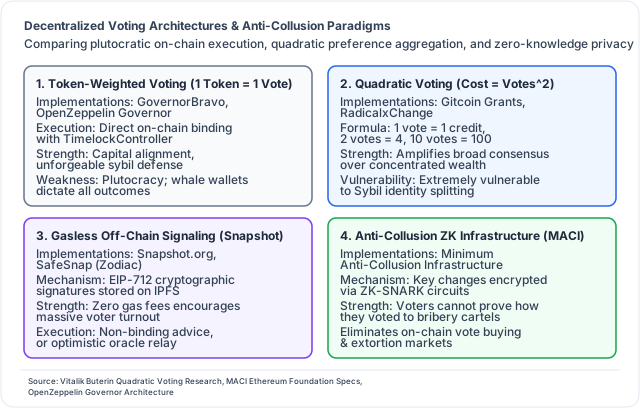
A blockchain voting system records eligibility, ballots, a tally, or the execution of a decision in a shared ledger. That description covers very different systems. A token-holder vote on a protocol parameter is not a public election. It can tolerate unequal voting weight and public ballots because token balances and governance actions are already public. A municipal election has harder requirements: one eligible person gets one ballot, nobody can learn a voter's choice, and a voter cannot prove that choice to a buyer or coercer.
The ledger does not supply those properties by itself. It can make a published result easier to inspect, but it does not establish who may vote, protect a compromised phone, or turn a visible ballot into a secret one. The National Academies' review of election security makes the broader point: internet voting faces serious risks from malware and denial-of-service attacks, while a voter-verifiable paper record remains central to evidence-based audits. A blockchain does not remove the device and network from that threat model. The report recommends against returning marked ballots over the internet for elections in the near term.
Blockchain voting is therefore most useful as a set of tools. Cryptographic signatures can authorize a ballot. A fixed block number can freeze voting weight. Smart contracts can count according to published rules and execute an approved transaction. Zero-knowledge proofs can show that a tally followed those rules without exposing each ballot. Whether those tools fit depends on the group making the decision and on the cost of a bad outcome.
In the simplest on-chain design, an address sends a transaction to a voting contract. The contract checks that the voting period is open, reads the address's voting weight, records a choice, and rejects a second vote. After the deadline, it compares the totals with a quorum and approval threshold. A passed proposal may be queued in a timelock before the contract performs the approved calls.
OpenZeppelin's Governor documentation describes this pattern. Its voting modules can read past token balances through checkpoints rather than current balances. The snapshot block matters. Without it, a holder could transfer the same tokens among addresses while voting, or borrow tokens after a proposal begins. A past-balance snapshot stops repeated use of one balance, though it does not stop a wealthy party from acquiring voting power before the snapshot.
The public record gives participants several checks. They can inspect the proposal code, verify the voting period and threshold, reproduce the count from transactions, and see whether the executed calls match the proposal. For a treasury or protocol upgrade, that link between decision and execution is valuable. It reduces reliance on an administrator to transcribe a result into an action.
It also makes individual choices visible when addresses can be linked to people, funds, or delegates. Public ballots are often acceptable in token governance because delegates are expected to explain their positions. They are usually unsuitable for an election where employers, family members, political groups, or local officials could use a ballot as evidence of compliance.
Some communities split voting from execution. Snapshot asks voters to sign a typed message rather than submit a blockchain transaction. The platform calculates voting power at a specified block and stores signed votes off-chain. This avoids transaction fees and lets a community use several voting-power rules, such as a token balance plus a membership credential. The outcome is a signal unless a separate system turns it into an on-chain action. A Safe controlled by signers can still decline to act, and an automated bridge from an off-chain result must define who can challenge an incorrect result and how.
Off-chain signatures lower the cost of participation. They do not create secrecy. A signature remains evidence of a choice, and the service that receives ballots becomes part of the availability and integrity model. A community should state which data source fixes voting weight, where signed ballots are published, how the final count is reproduced, and what happens if that service is unavailable.
Addresses prove control of private keys. They do not prove that their holders are distinct people, residents, shareholders, or members. This gap is the Sybil problem. It is irrelevant when a system deliberately assigns one vote per token, but it is decisive when a rule claims one person, one vote.
An eligibility system needs an issuer or process that binds a person or organization to a credential. A government might rely on a civil registry. A cooperative might rely on a membership roll. A company can rely on its share register and a record date. These are governance choices, not blockchain features.
The W3C Verifiable Credentials data model offers a format for signed claims. A credential can state that its holder belongs to a group, while a presentation can disclose only the claim needed for a ballot. The specification does not vouch for the issuer's accuracy or solve duplicate registration. It defines how credentials can be expressed and verified. Revocation, expiry, recovery after a lost key, and disputes about eligibility still require operating rules.
Proof-of-personhood systems attempt to make duplicate identities expensive. They use social verification, government identity checks, biometrics, or a combination. Each choice has costs. Social graphs may exclude newcomers. Identity-document checks collect sensitive information. Biometric systems ask voters to trust hardware, enrollment operators, and policies for biometric data. A system can use zero-knowledge techniques to limit what reaches the voting contract, yet the enrollment provider may still see identifying information.
Quadratic voting makes the identity question sharper. A participant buys or receives voice credits, and the cost of additional votes rises with the square of the votes cast. Four votes cost sixteen credits, for example. The rule limits the influence a single identity can buy with a fixed credit allocation. If one participant can register sixteen identities and receive one credit through each, the intended limit disappears. Glen Weyl's paper on quadratic voting treats the mechanism as a way to express preference intensity; deployment still depends on a credible account of who is distinct.
Token voting avoids pretending that wallets are people. Its rule is closer to shareholder voting: capital at risk receives voting weight. That may align a protocol's control with people who bear its financial consequences. It also concentrates power when ownership is concentrated. Delegation can reduce the burden of reading every proposal, but it can concentrate practical power in a small group of active delegates. Published delegate votes make that concentration inspectable; they do not correct it.
An append-only ledger is well suited to public audit trails. Anyone can check that a governance contract received a valid transaction and applied the written counting rule. Yet a public audit trail exposes more than administrators need for a secret ballot. Encrypting a vote before placing it on-chain can hide the choice, but the system still needs a trustworthy method to decrypt or tally it without giving one party control over every ballot.
Election cryptography offers techniques for this. Homomorphic encryption allows encrypted ballots to be combined, so trustees decrypt an aggregate rather than every individual vote. Mixnets shuffle encrypted ballots before decryption, breaking the direct link between a voter and a ballot. Zero-knowledge proofs can show that a ballot is well formed and that a tally was calculated correctly. The U.S. Election Assistance Commission's Voluntary Voting System Guidelines describes cryptographic protections as part of a larger voting-system standard, including auditability and accessibility requirements.
Privacy is necessary but insufficient. A secret ballot must also be receipt-free. If a voter can produce a durable receipt showing a choice, a buyer can pay only voters who support a specified option. If a coercer can stand beside the voter during an online ballot, encryption does not help. Remote voting cannot reproduce the privacy of a supervised polling place without assumptions about the voter's surroundings and device.
MACI, or Minimum Anti-Collusion Infrastructure, is an attempt to weaken one form of coercion in blockchain communities. Participants register a public key and send encrypted commands, including key changes and votes. A coordinator processes those commands and produces a zero-knowledge proof for an on-chain verifier. Because a voter can change keys privately, a coercer cannot reliably tell whether a key shown during a demand remains the one used for the final vote. MACI's documentation is explicit about its boundary: it reduces collusion opportunities but does not solve all coercion, and the coordinator has operational responsibilities. It fits a constrained governance setting better than it settles the problem of remote public elections.
Transparency also has limits beyond ballot privacy. Contract code can be open while the proposal is hard to understand. A proposal may call several contracts through encoded data, and an ordinary voter may not be able to determine its practical effect. Timelocks, human-readable descriptions, independent simulation, and cancellation powers can make an execution path easier to review. They add processes and trusted roles, which should be disclosed rather than described as decentralization.
Protocol and DAO governance is the clearest use case. The electorate is usually defined by a token or membership credential, the decisions are native blockchain actions, and participants can inspect the same state that the contract uses. Compound's governance documentation shows a familiar arrangement: governance tokens may be delegated, proposals require a threshold of delegated votes, and successful proposals pass through a timelock before execution. These rules are visible in code and can be changed only through the governance process they define.
Grant programs and community budgets are another fit when the group accepts the identity system and voting rule. Gitcoin's quadratic funding documentation explains a related allocation method: matching funding responds more to many small contributors than to one large contribution. The approach can direct a shared pool toward broadly supported projects. It is exposed to fake accounts and coordinated donation patterns, so its outcomes depend on the anti-Sybil checks, eligibility rules, and review process around the formula.
Shareholder voting has a different starting point. Voting rights derive from legally recognized shares, record dates, intermediaries, and corporate law. A distributed ledger might improve reconciliation if the legal share register and the voting system use the same authoritative data. It cannot bypass beneficial ownership rules, securities lending, proxy rules, or the jurisdiction's requirements for notices and records. The SEC's proxy rules remain part of the system even if ballot instructions use cryptographic signatures.
Public elections have the highest bar. They need inclusive registration, accessible voting methods, secret and coercion-resistant ballots, credible recounts, dispute resolution, and continuity when devices or networks fail. Estonia's i-voting system is often called blockchain voting, but its election authority describes a national internet-voting process based on state digital identity and repeat voting, where the last electronic vote counts and an in-person paper vote overrides it. Its experience shows that digital voting depends on identity infrastructure, election law, and administration. A ledger label does not describe the whole system.
Smart contracts apply rules exactly as written, including mistakes. A flaw in eligibility logic, a bad quorum setting, or an unsafe execution call can produce a valid on-chain result with damaging effects. Upgrade authority and emergency controls can reduce the consequences of an error, but they introduce another question: who can override voters and under what conditions?
Participation is not guaranteed by low fees. Token holders may lack the time or information to assess a proposal. Delegates can provide informed review, but voters must be able to replace them, and conflicts of interest need public disclosure. A quorum can prevent a small turnout from changing rules, yet it can also let organized abstention block action.
Finally, no ballot protocol can settle a disagreement about the rule itself. Groups still have to decide who belongs, what voting power represents, when a result is legitimate, and who resolves an appeal. Blockchain systems can preserve evidence about those decisions and, in some settings, execute them. They do not remove the institutions and judgment that make a vote legitimate.
Explore more guides and career playbooks